

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
71.1k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 canyie/cve-2024-0044
Proof-of-concept and writeup for bypassing the initial patch of CVE-2024-0044, an Android framework vulnerability enabling privilege escalation from…
 not-matthias/amd_hypervisor
Rust AMD SVM hypervisor framework with customizable vmexit handlers (MSR, CPUID, RDTSC) and NPT hooking for kernel-level monitoring and research.
 zcutlip/bowcaster
Python-based exploit development framework with payloads, encoders, and connect-back servers, focused on MIPS CPU architecture but designed for…
 bw3ll/jop_rocket
This framework enables user to discover JOP gagdets and can automate building a complete JOP chain to bypass DEP. JOP ROCKET is the ultimate solution…
 abdsec/cve-2016-0801
C-based proof-of-concept exploit for CVE-2016-0801, demonstrating a specific vulnerability in Android components for security research and testing.
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 flankerhqd/cve-2015-6612poc-form
Proof-of-concept exploit for CVE-2015-6612 targeting Android media decoder vulnerability. Demonstrates binary exploitation in the Android AV…
 j4ck3lsyn-gen2/cve-2026-39047
Epson Printer RAW Protocol Exploit Framework
 timwr/cve-2019-5825
Chrome V8 exploit for CVE-2019-5825 targeting version 73.0.3683.86 with --no-sandbox. Includes proof-of-concept code and integration with Metasploit…
 audiobahn/cve-2021-4034
Local privilege escalation exploit for CVE-2021-4034 targeting pkexec, providing proof-of-concept code for security testing and research.
 34zy/cve-2026-86950
Exploitation framework for CVE-2026-86950, a CoreGraphics integer overflow: crafts malicious TrueType fonts and PDFs, extracts ASLR leaks, and builds…
 kosmokato/bad-dicom
Explotation framework for CVE-2019-11687
 infiniteloopers/cve-2019-2107
Proof-of-concept exploit for CVE-2019-2107, demonstrating remote code execution via crafted HEVC video on Android media framework. Includes crash…
 feliam/cve-2014-4481
Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
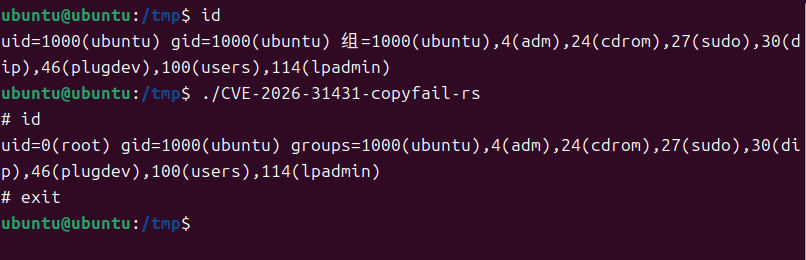 kanbaraakihito/cve-2026-31431-copyfail-rs
Pure Rust proof-of-concept for CVE-2026-31431, targeting Linux x86_64 kernels with AF_ALG AEAD support. Static musl build, no runtime dependencies,…
 fevar54/cve-2025-48595-android-framework-integer-overflow-
PoC de CVE-2025-48595: desbordamiento de entero en multiples ubicaciones del Framework de Android.
 whatswrongandwhy/cve-2017-16995
Standalone exploit for CVE-2017-16995, a Linux kernel local privilege escalation vulnerability, providing a ready-to-use proof-of-concept for…