
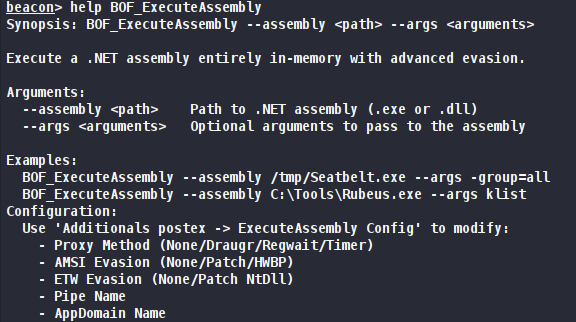
BOF_ExecuteAssembly
 ntdallas/bof_executeassembly
Beacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
binary-exploitationcommand-and-controlids-ips-evasion+4
200
ntdallas/bof_executeassemblyBeacon Object File for Cobalt Strike that executes .NET assemblies in beacon with evasion techniques.
 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 silentisvox/syscallrevenant
Clean Indirect Syscalls with Syscall Tampering.
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
 bikini/exploitarium
Curated archive of public proof-of-concept exploits and vulnerability research writeups covering web, binary, and network security, with a focus on…
 henryreed/cve-2022-0486
Fidelis Network and Deception - Insecure File Permissions Privilege Escalation - Multiple
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
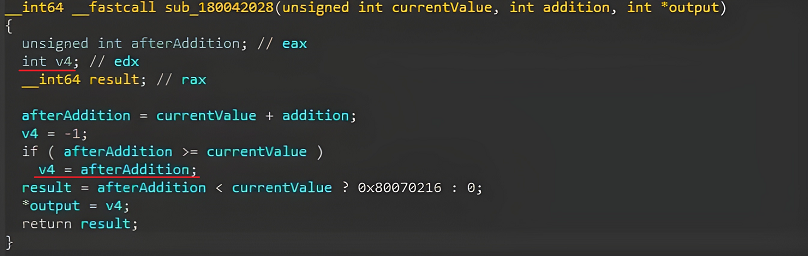 websecnl/cve-2022-26809
Remote Code Execution Exploit in the RPC Library
 justintroup85/exploits-forsale-collateral-damage
Kernel exploit for Xbox SystemOS using CVE-2024-30088
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 anyaschukin/override
Binary Exploitation and Reverse-Engineering (from assembly into C)
 warxim/vucsa
Deliberately vulnerable client-server application for learning penetration testing of non-HTTP thick clients. Includes challenges for SQL injection,…
 fortra/cve-2022-30136
Windows Network File System Remote exploit for CVE-2022-30136
 0xcyberstan/cve-2026-46215-poc
Exploit for CVE-2026-46215, a Linux kernel DRM GEM use-after-free local privilege escalation. Uses racing, slab spraying, and Dirty Pipe-style file…