

CVE-2026-53359
 horkimhab/cve-2026-53359
CVE-2026-53359 - Draft
binary-exploitationeducationexploitation+3
horkimhab/cve-2026-53359CVE-2026-53359 - Draft
 ayushx007/cve-2022-0847-dirtypipe-exploits
Collection of exploits and documentation for the Linux Dirty Pipe vulnerability (CVE-2022-0847), enabling arbitrary file overwrite and SUID binary…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 v4bel/dirtyfrag
Linux kernel privilege escalation exploit chaining two page-cache write vulnerabilities (CVE-2026-43284, CVE-2026-43500) for deterministic root…
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 theori-io/copy-fail-cve-2026-31431
Exploits a 9-year-old Linux kernel local privilege escalation (CVE-2026-31431); provides tested exploit logic for Ubuntu, Amazon Linux, RHEL, and…
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 chompie1337/smbghost_rce_poc
Proof-of-concept remote code execution exploit for CVE-2020-0796 (SMBGhost) targeting Windows SMBv3 compression vulnerability with kernel shellcode…
 timwr/cve-2016-5195
CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android
 mortenoir1/virtualbox_e1000_0day
VirtualBox E1000 Guest-to-Host Escape
 arthepsy/cve-2021-4034
Proof-of-concept exploit for CVE-2021-4034 (PwnKit), a local privilege escalation vulnerability in polkit's pkexec, allowing unprivileged users to…
 blasty/cve-2021-3156
Exploit for CVE-2021-3156 (Baron Samedit), a heap-based buffer overflow in sudo, enabling local privilege escalation. Includes target list and…
 arinerron/cve-2022-0847-dirtypipe-exploit
A root exploit for CVE-2022-0847 (Dirty Pipe)
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
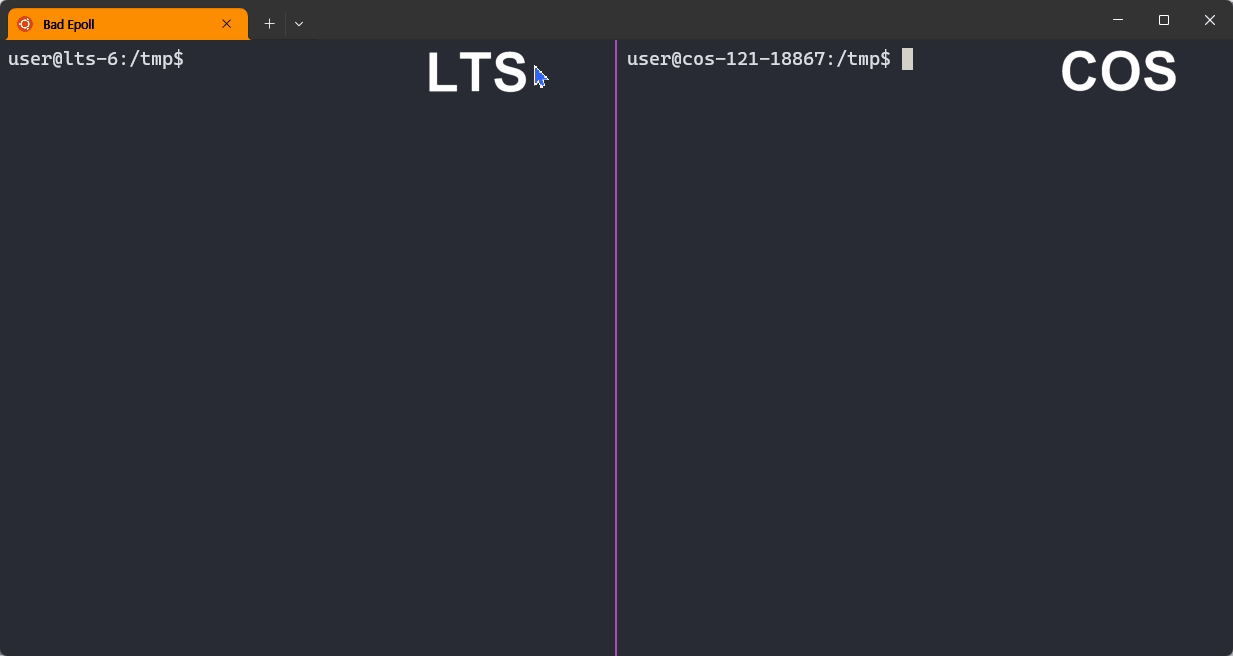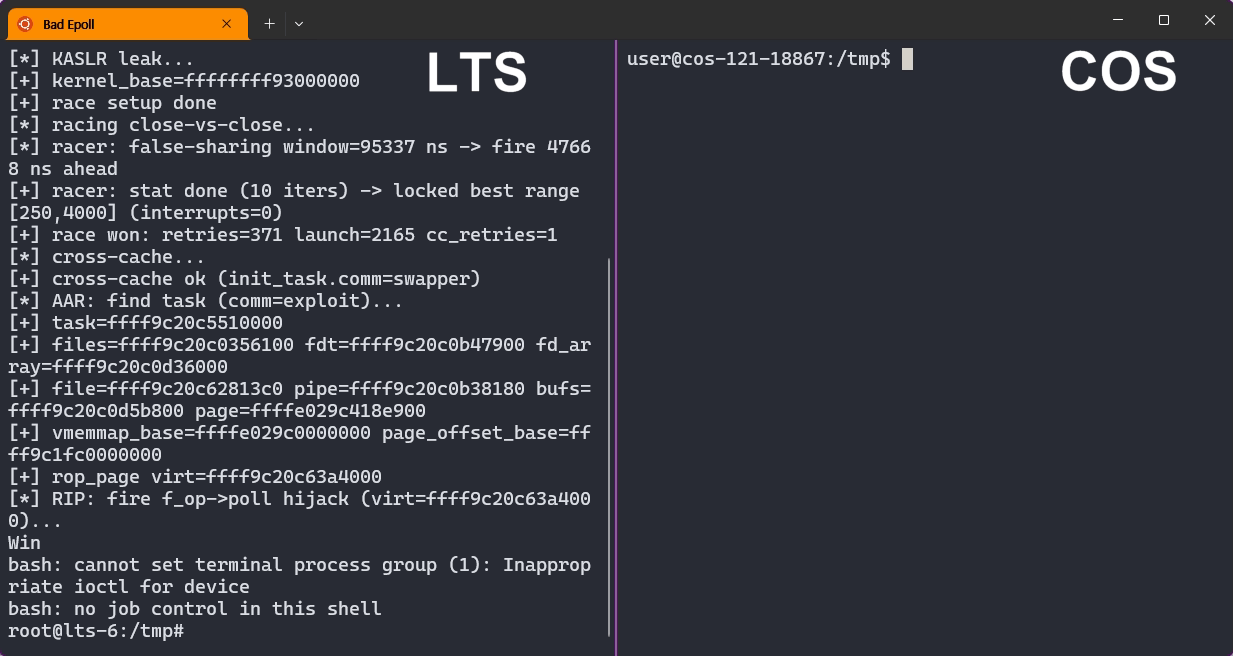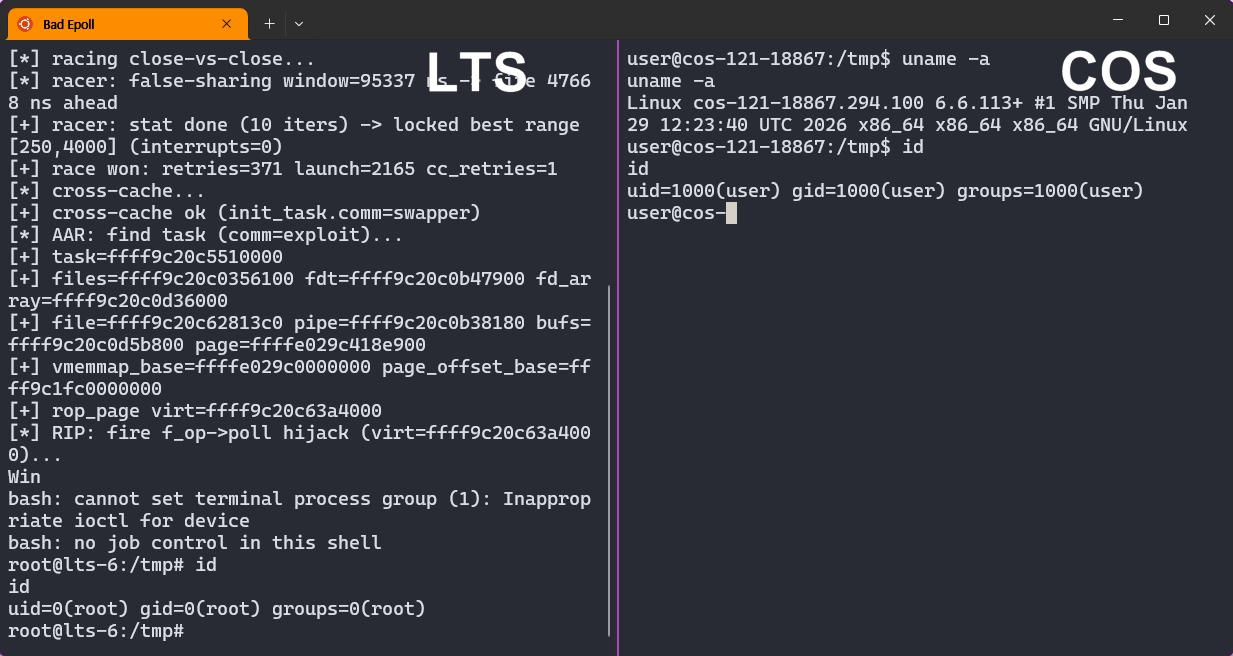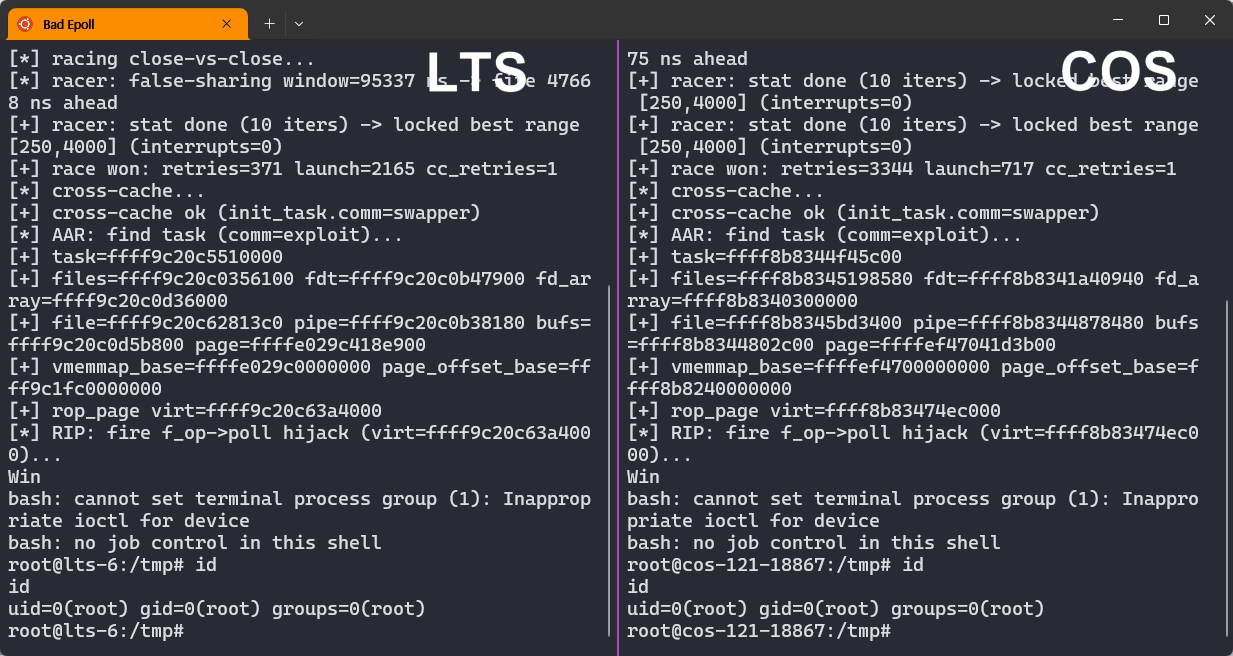 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
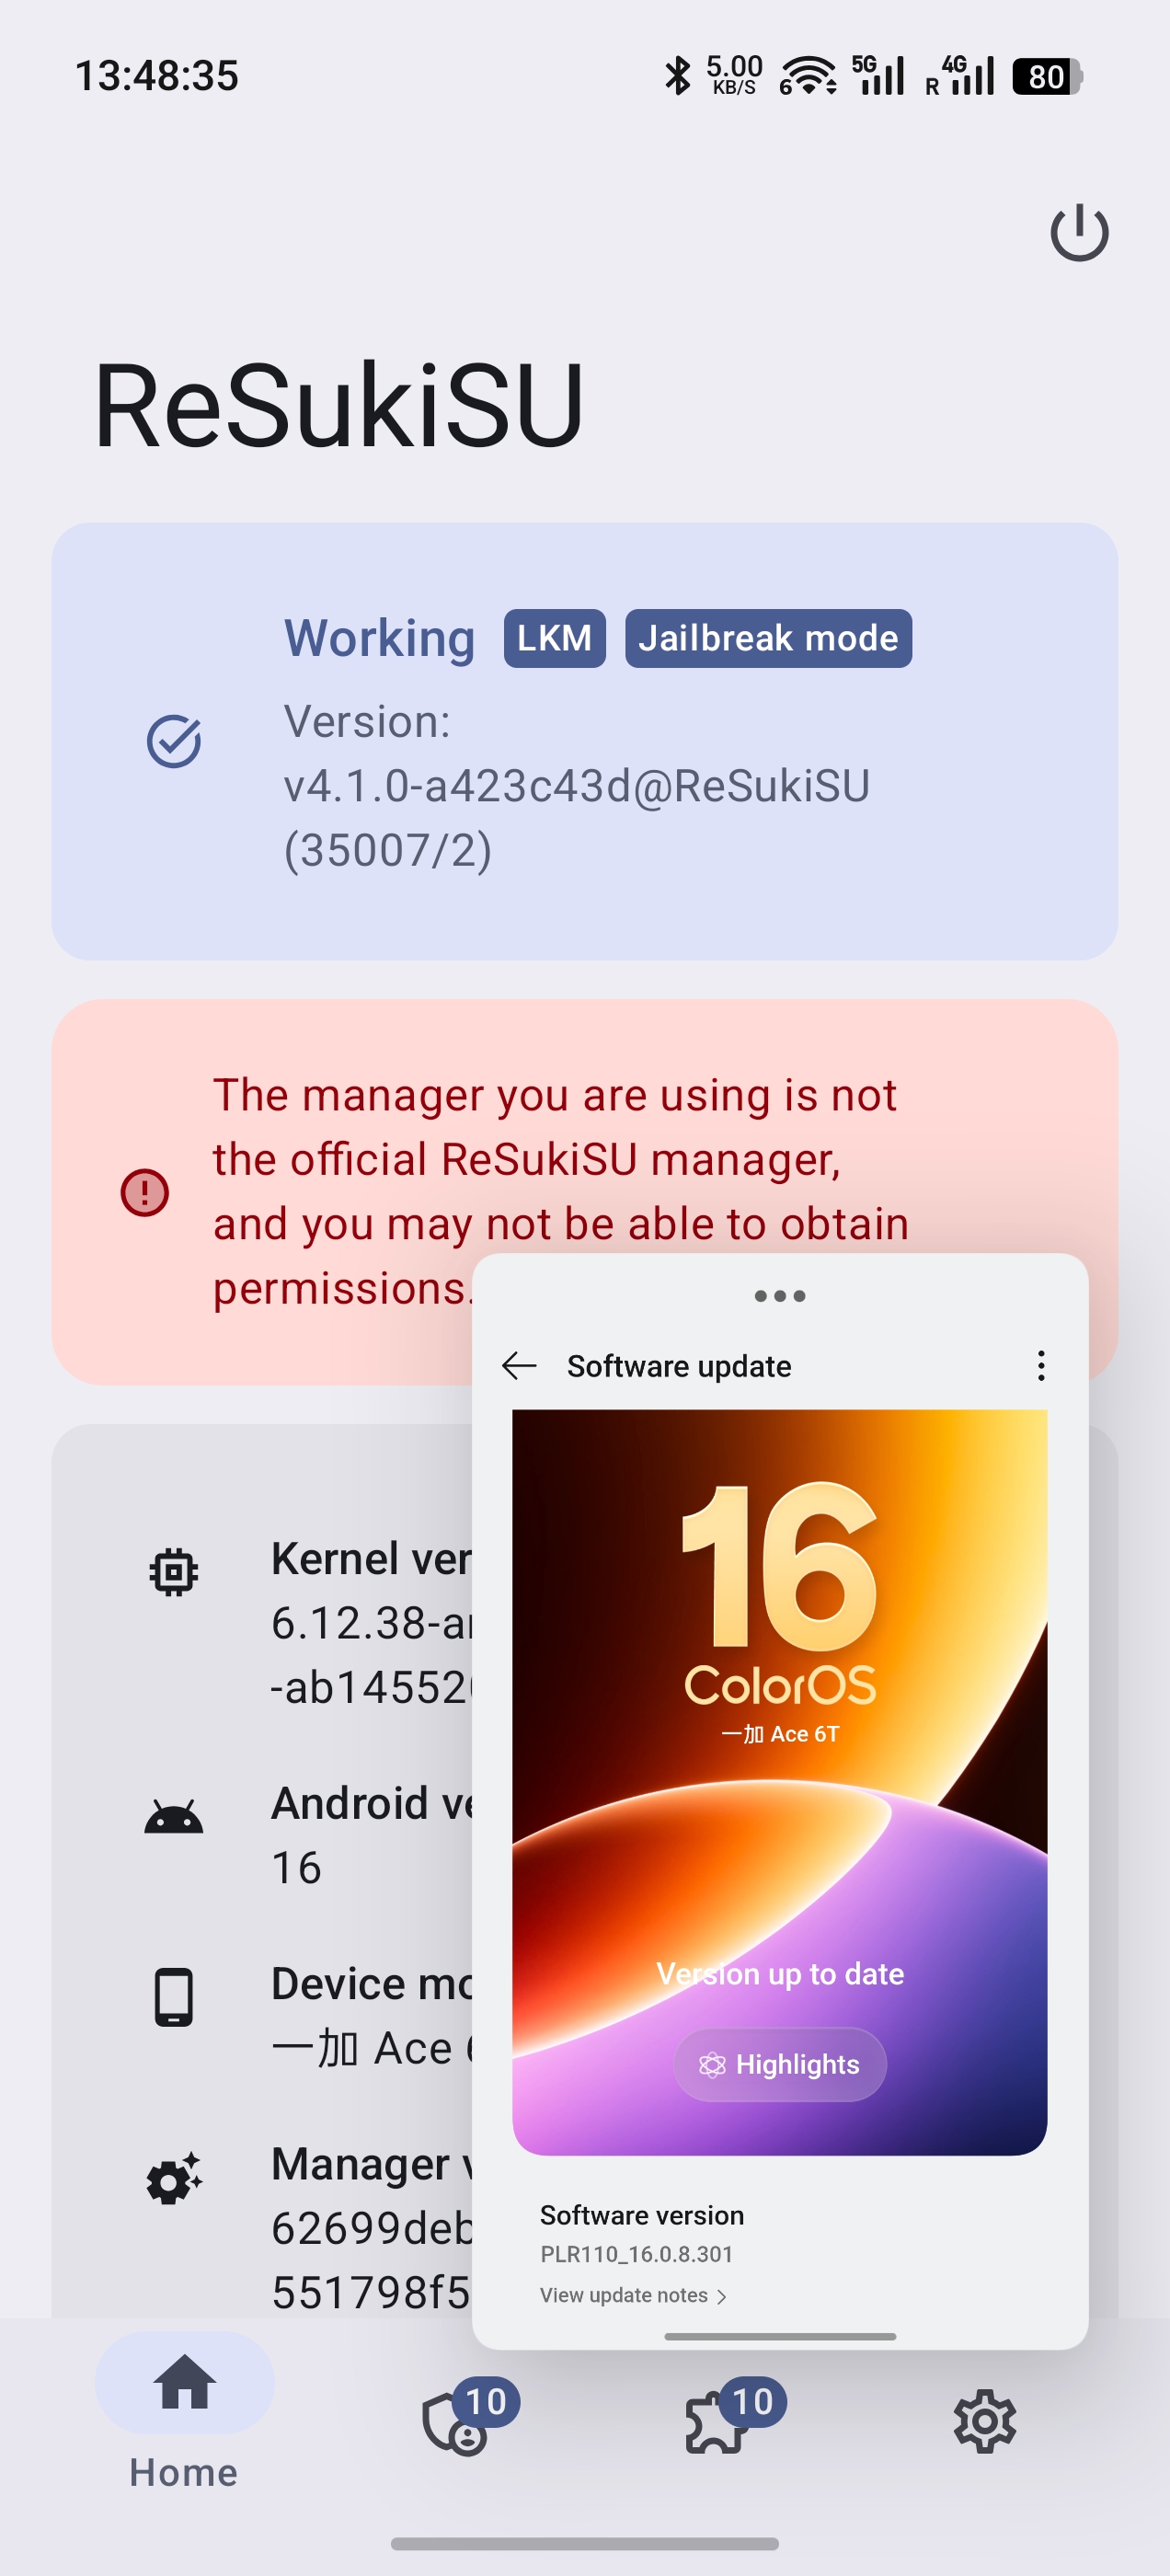 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader