

dirtycow-replacer
 droidvoider/dirtycow-replacer
CVE-2016-5195 dirtycow by timwr automated multi file patch tool
android-securitybinary-exploitationeducation+5
4
droidvoider/dirtycow-replacerCVE-2016-5195 dirtycow by timwr automated multi file patch tool
 hackspeak/cve-2026-14669
Proof-of-concept exploit for CVE-2026-14669, a PostgreSQL to_char() timezone abbreviation heap buffer overflow enabling RCE through information leak…
 eduquintanilha/cve-2022-0847-dirtypipe-exploits
C exploit collection for Linux Dirty Pipe (CVE-2022-0847) local privilege escalation, including read-only file overwriting and SUID binary hijacking,…
 kentox493/cve-2026-46300_fragnesia
Linux kernel local privilege escalation exploit with automated prerequisite audit for CVE-2026-46300, validating patch status, XFRM ESP-in-TCP…
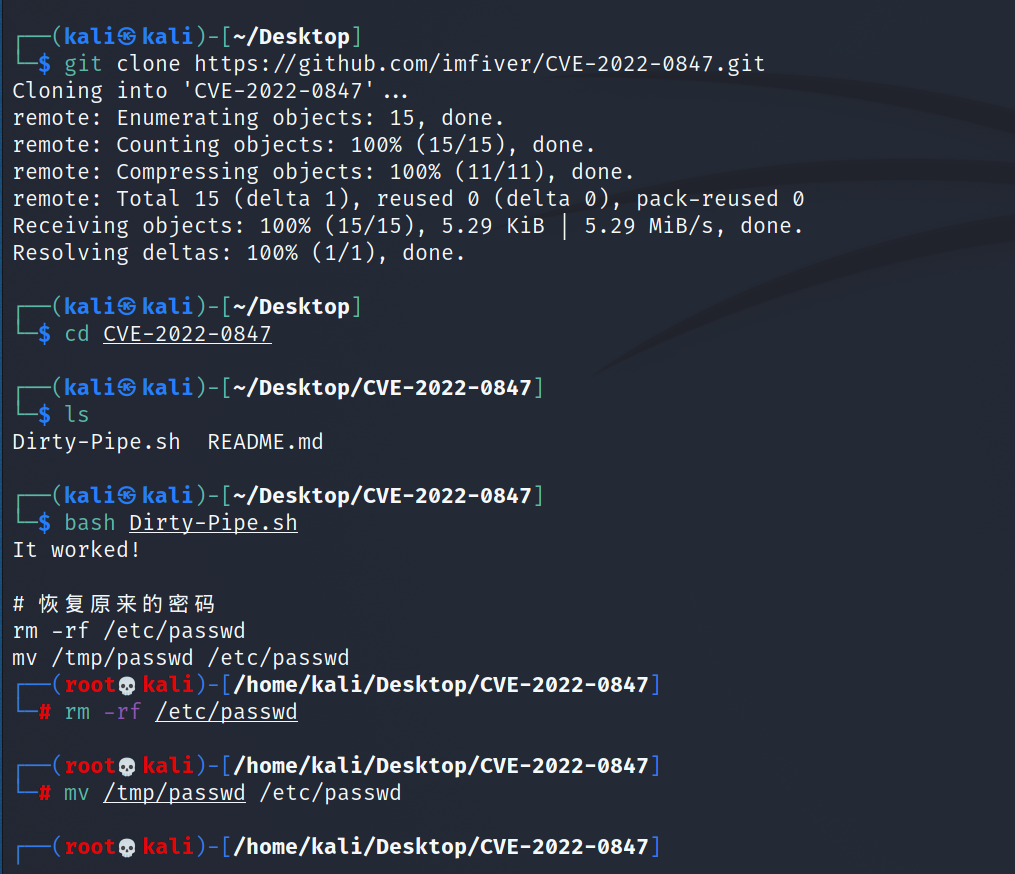 puckiestyle/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe) targeting Linux kernel versions 5.8–5.15. Provides reproduction environment setup and…
 edutko/cve-2024-31497
Proof-of-concept exploit for CVE-2024-31497, demonstrating a critical vulnerability with automated exploitation logic for security testing and…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 binw2018/cve-2021-3156-script
Automated exploit script for CVE-2021-3156, a sudo heap-based buffer overflow, enabling local privilege escalation on vulnerable Linux systems.
 hoangnhoo/reproduce-cve-2023-52927
Reproduction environment for CVE-2023-52927, a Linux kernel vulnerability, with automated scripts to trigger the exploit on a kCTF COS target machine.
 muharremk0/info-sys-security-cve-2025-55182
Academic lab for analyzing CVE-2025-55182 (React2Shell) with vulnerable and patched React Server Components environments, exploit shell, automated…
 pixelotes/lab-cve-2023-4863
Docker-based lab to reproduce CVE-2023-4863 (heap buffer overflow in libwebp) with automated crash demonstration, patched vs vulnerable comparison,…
 secvulnhub/cve-2025-32463-exploit
Proof-of-concept exploit for CVE-2023-42456, demonstrating privilege escalation via sudo NSS library hijacking through chroot injection. Includes…
 dbrumley/extract75-cve-2020-13995
Control flow hijack exploit for CVE-2020-13995 with Docker-based deployment and Mayhem fuzzing integration for automated vulnerability testing.
 solomon12354/lockinggirl-----cve-2022-0847-dirty_pipe_virus
Educational demonstration of CVE-2022-0847 (Dirty Pipe) Linux kernel exploit with automated compilation script for privilege escalation and file…
 orsuprasad/cve-2022-0847-dirtypipe-exploits
C exploit collection for Linux Dirty Pipe (CVE-2022-0847) local privilege escalation, including read-only file overwrite and SUID binary hijacking,…
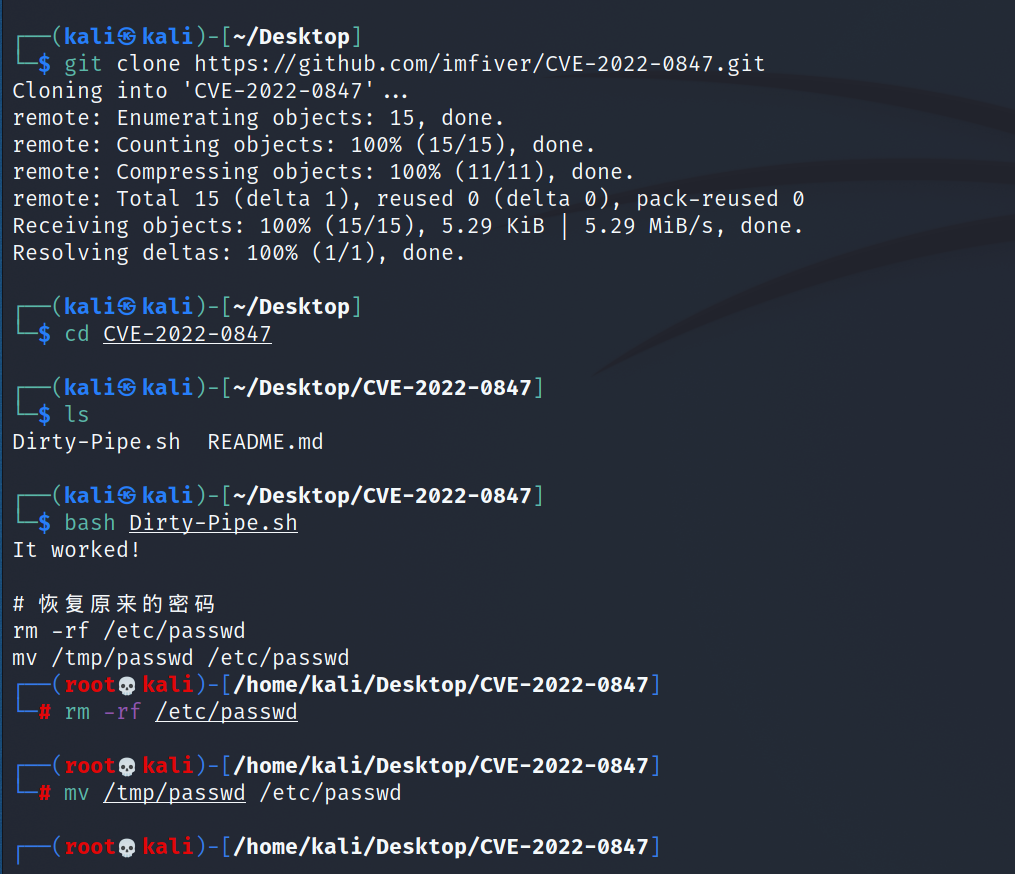 xsxtw/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel vulnerability enabling local privilege escalation via overwriting read-only…
 giovannipajeu1/cve-2024-23740
Automated exploit for CVE-2024-23740 targeting Kap on macOS. Injects code via RunAsNode and enableNodeClilnspectArguments to spawn a remote shell.
 killreal01/cve-2023-4911
Proof-of-concept exploit for CVE-2023-4911 (Looney Tunables) targeting glibc privilege escalation on Linux systems. Includes vulnerability check and…