
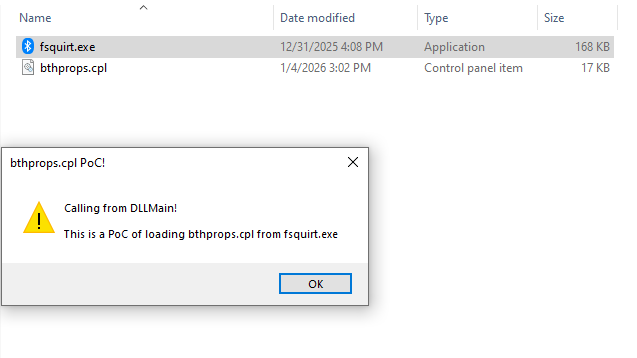
FsquirtCPLPoC
 mhaskar/fsquirtcplpoc
PoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
binary-exploitationcommand-and-controlexploitation+5
121
mhaskar/fsquirtcplpocPoC for generating bthprops.cpl module designed to be loaded by Fsquirt.exe LOLBin
 kungfulon/nf-tables-lpe
Linux kernel privilege escalation exploits targeting Netfilter's nf_table module, developed by Team Orca for multiple CVEs.
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 jelasin/cve-2026-42945
Proof-of-concept exploit for CVE-2026-42945, a heap buffer overflow in NGINX's rewrite module enabling unauthenticated remote code execution via…
 danaepp/pwncat_dirtypipe
pwncat module that automatically exploits CVE-2022-0847 (dirtypipe)
 m4p0/geutebrueck_gcore_x64_rce_bo
Metasploit module for Geutebrueck GCore "video management" system. Tested with version 1.3.8.42 and 1.4.2.37
 sneakynachos/cve-2026-85046-who-put-the-silverback-guerilla-in-the-wasm
Proof-of-concept exploit for CVE-2026-85046 in Chrome 152.0.7977.75, demonstrating type confusion in sort() to achieve arbitrary code execution via a…
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 matrix07ksa/allmediaserver-1.6-buffer-overflow
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.
 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 adityasingh108/cve-2026-31431-metasploit-exploit
Automated Metasploit post-exploitation module for CVE-2026-31431 ("Copy Fail"). Weaponizes a deterministic logic flaw in the Linux kernel AF_ALG…
 hackspeak/cve-2026-23479
Redis UAF RCE PoC collection for CVE-2026-23479: safe version checker, exploit module, GDB-assisted PoC, and Sigma detection rules for authorized…
 quantumworld-dpdns-io/cve-2026-42945
Full CVE-2026-42945 research repository with heap buffer overflow analysis, RCE exploit (heap spray + Feng Shui), detection scripts, and patching…
 dixyes/fuck_cve_2026_31431
Kernel module exploiting CVE-2026-31431 to bypass system stop mechanisms, with configurable fake implementation for testing on non-stoppable machines.
 forxiucn/nginx-cve-2026-42945-poc
Proof-of-concept exploit for CVE-2026-42945, a critical heap overflow in NGINX rewrite module enabling unauthenticated remote code execution via…
 spydomain/cve-2022-0435-poc
Stack overflow exploit for CVE-2022-0435 in the TIPC module, providing local privilege escalation to root on Ubuntu kernels.
 xooxo/cve-2025-40019-essiv
A PoC for CVE-2025-40019 in ESSIV module. (exploit WIP)