
CVE-2021-22204
 trganda/cve-2021-22204
In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…
binary-exploitationcode-analysiseducation+3
3
trganda/cve-2021-22204In-depth technical analysis of CVE-2021-22204 (ExifTool RCE) with PoC reproduction, payload construction, and Perl code review of the vulnerable DjVu…
 gmh5225/gmh5225
LLVM-based security research toolchain: NeverC, a C23 cross-compiler, and NeverD, a binary analysis and decompilation engine that lifts PE, ELF,…
 sprushed/cve-2022-30292
Technical documentation and analysis of CVE-2022-30292, a heap-based buffer overflow in Squirrel 3.2 leading to denial of service, sandbox escape,…
 minsmiths/cve-2023-34446
Proof-of-concept exploit for CVE-2023-36664, a Ghostscript command injection vulnerability. Includes Docker lab environment, detailed analysis of…
 dexsemon/cve-2026-27495
Proof-of-concept exploit and lab environment for CVE-2026-27495
 kavin-jindal/cve-2026-48800-poc
Proof-of-concept exploit for CVE-2026-48800 demonstrating arbitrary code execution in Notepad++ ≤ 8.9.6 via malicious shortcuts.xml. Includes trigger…
 e-corp-demo/cve-2026-44788
Proof-of-concept exploit for CVE-2026-44788, demonstrating vulnerability exploitation in C# for security testing and validation.
 dwgth4i/cve-2026-20817
Proof-of-concept exploit for CVE-2026-20817, demonstrating the vulnerability with a C-based implementation for security research and testing.
 jelasin/cve-2026-42533
Proof-of-concept reproduction of an nginx heap overflow and info leak (CVE-2026-42533) with two attack surfaces, debug analysis, and a full RCE chain.
 pazhanivelmani/av_cve-2020-0162_a10r33
Exploit for CVE-2020-0162 targeting a specific vulnerability, implemented in C++ for binary exploitation and security testing.
 danieltangnes/cve-2026-3888
Proof-of-concept exploit for CVE-2026-3888, written in C. Demonstrates vulnerability exploitation and binary-level attack techniques for security…
 harithlab/cve-2023-6546
C-based exploit for CVE-2023-6546, providing proof-of-concept code to demonstrate and test the vulnerability in affected systems.
 d0rb/cve-2024-4323
Critical heap buffer overflow vulnerability in the handle_trace_request and parse_trace_request functions of the Fluent Bit HTTP server.
 bantu2301/cve-2018-16858
Proof-of-concept exploit for CVE-2018-16858, demonstrating the vulnerability and providing exploitation code for security testing and research.
 y0un9eee/cve-2024-27766
Modified PoC for MariaDB v11.1 RCE via UDF, returning command output inline through SQL queries. Includes detailed code comparison and compilation…
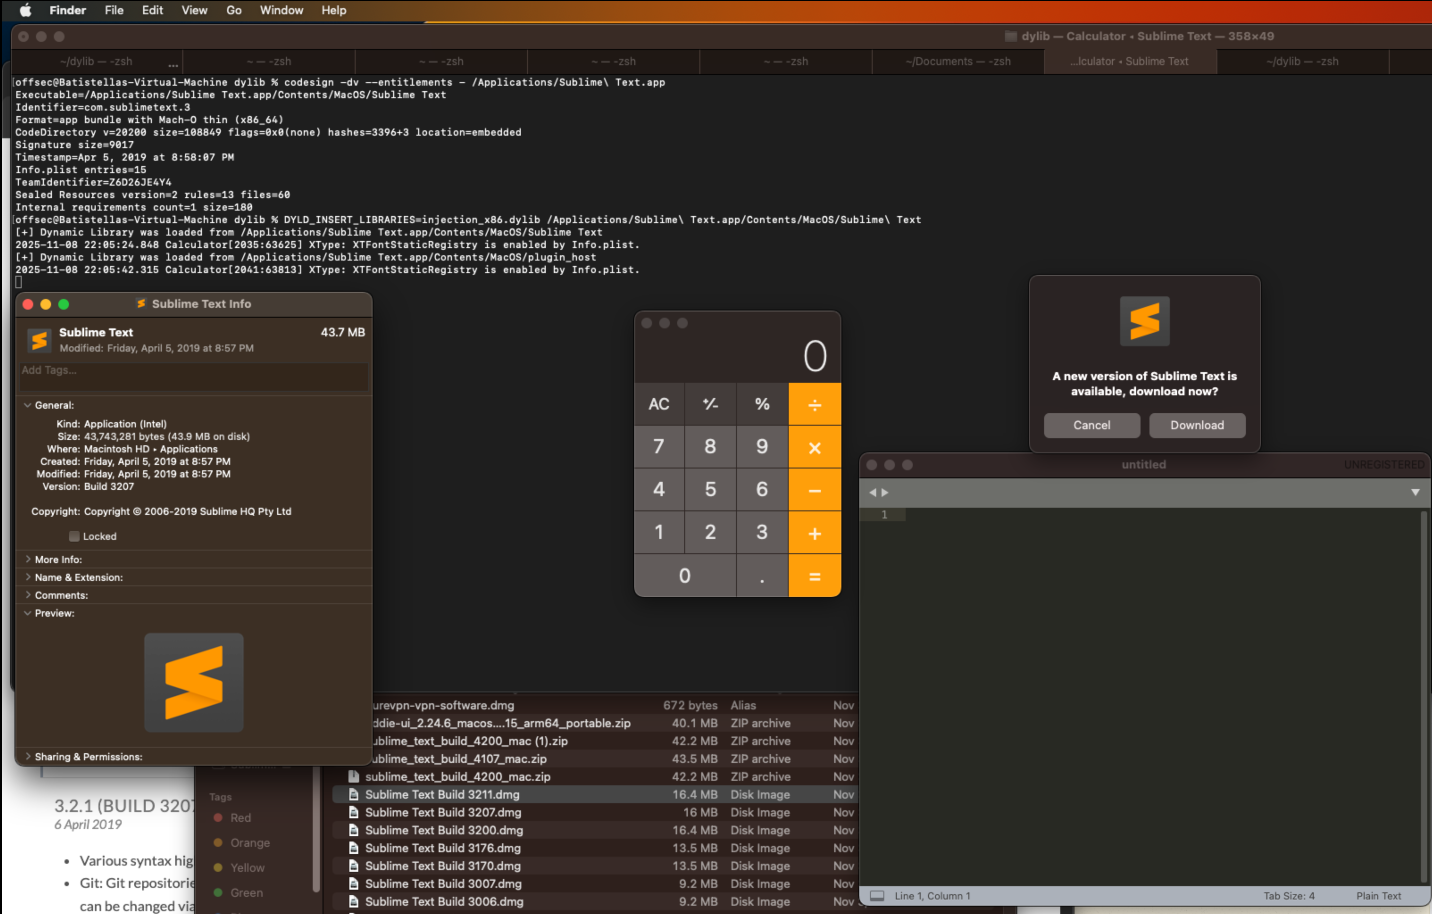 vinicius-batistella/cve-2025-65741
Proof-of-concept for CVE-2025-65741 demonstrating dylib injection in Sublime Text 3 on macOS via unsigned code, with a compiled .dylib payload and…
 x0da6h/poc-for-cve-2024-32019
Proof-of-concept exploit for CVE-2024-32019 vulnerability, written in C for testing and verification of the security flaw.
 naved124/cve-2024-28397-js2py-sandbox-escape
Detailed analysis of CVE-2024-28397, a sandbox escape vulnerability in js2py enabling RCE via Python object traversal. Includes code analysis, PoC,…