
CVE-2026-62735
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
binary-exploitationexploitationexploit-frameworks+3
5
hackspeak/cve-2026-62735Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
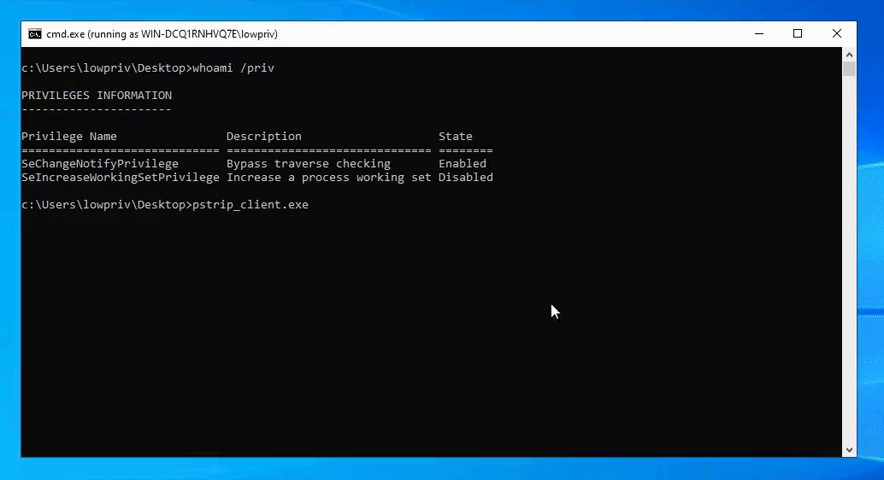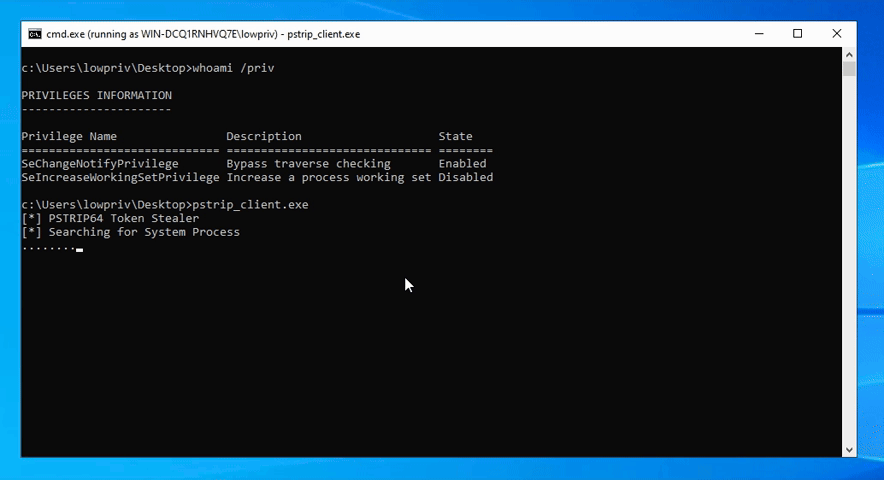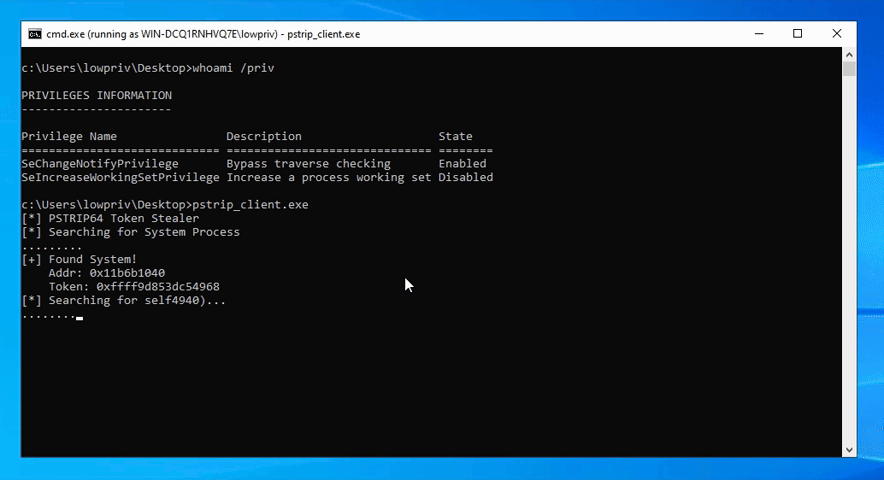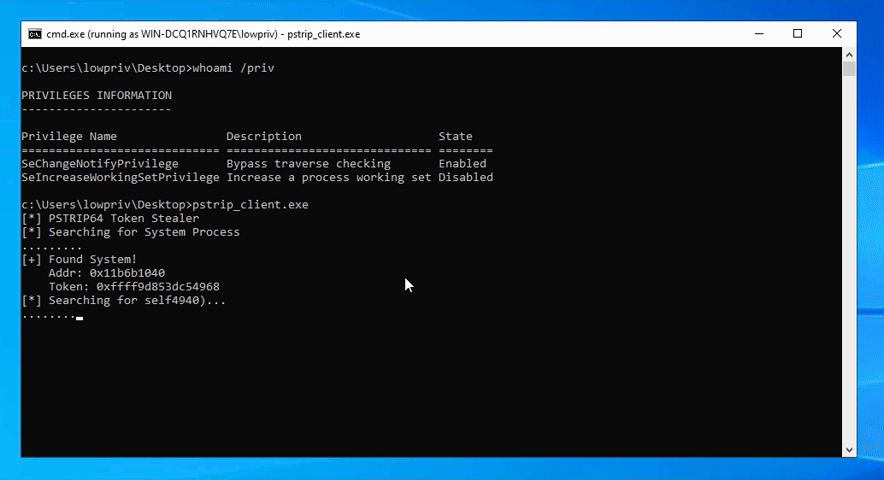 smarttfoxx/cve-2026-29923
The pstrip64.sys kernel driver exposes an IOCTL that allows low-privileged users to map arbitrary ranges of physical memory into their own virtual…
 wired0ut/cve-2019-2215
Full exploit for the Android vulnerability Bad Binder found in early Google Pixel phones.
 spiralbl0ck/-cve-2018-0834-aab-aar
CVE-2018-0834 full code exec
 5ky9uy/glass-cage-i18-2025-24085-and-cve-2025-24201
Glass Cage is a zero-click PNG-based RCE chain in iOS 18.2.1, exploiting WebKit (CVE-2025-24201) and Core Media (CVE-2025-24085) to achieve sandbox…
 simoesctt/ctt-nfs-vortex-rce
New Physics Disclosure This repository contains a full weaponized exploit for **CVE-2026-21509**, targeting the Windows Network File System (NFSv4.1)…
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
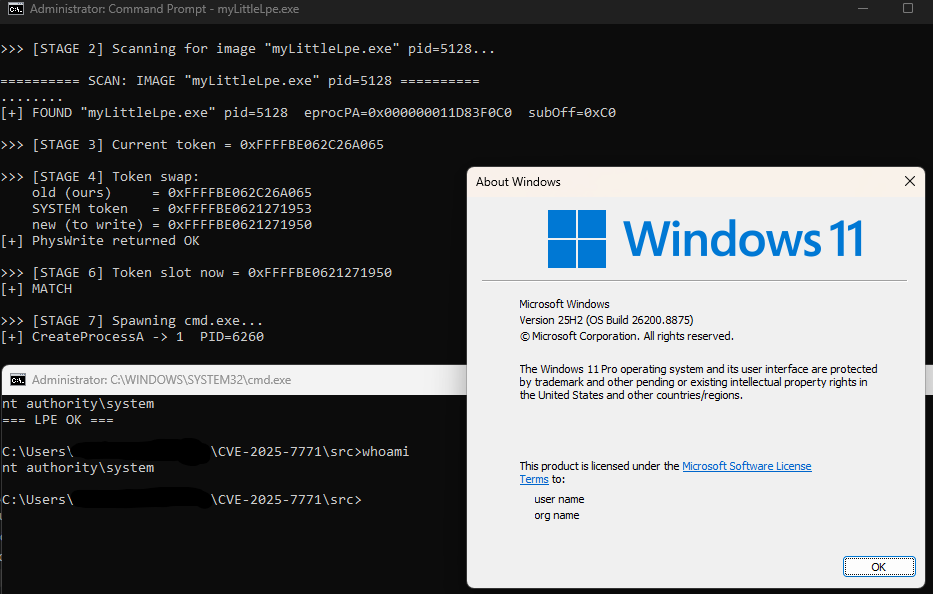 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 dinosn/cve-2026-25243-debugfree
Reliable remote code execution exploit for CVE-2026-25243 targeting jemalloc Redis. Executes arbitrary commands via a single crafted RESTORE command…
 liyuxuan504-byte/cve-2026-14266
7-Zip XZ Decoder Heap Buffer Overflow - Full analysis, root cause, PoC, and RCE exploitation roadmap
 l1m3syc/cve-2024-4947-poc
Educational proof-of-concept for CVE-2024-4947, a V8 Maglev type confusion, demonstrating a full chain from trigger to arbitrary code execution on a…
 suruurism/cve-writeups-and-pocs
CVE-2026-80724 PoC + full write-up — Linux kernel ptp/vmclock read-only mapping becomes writable (VM_MAYWRITE). Discovered, reported & fixed by…
 sneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box
Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
 kungaocode/vulnerability-analysis-
Automated reproduction and analysis of CVE-2021-26708 — a use-after-free vulnerability in the Linux kernel's AF_VSOCK subsystem (v5.10.12). Includes…
 0xdtc/below-logger-symlink-attack_cve-2025-27591
A Bash-based privilege escalation exploit targeting the `below` system performance monitoring tool. This refurbished exploit leverages a symlink…
 quantumworld-dpdns-io/cve-2026-42945
Full CVE-2026-42945 research repository with heap buffer overflow analysis, RCE exploit (heap spray + Feng Shui), detection scripts, and patching…
 mbanyamer/rtos-f-16-exploit---cve-2019-7711
Proof-of-concept exploit for CVE-2019-7711, a format string vulnerability in Green Hills INTEGRITY RTOS. Demonstrates a full attack chain with memory…
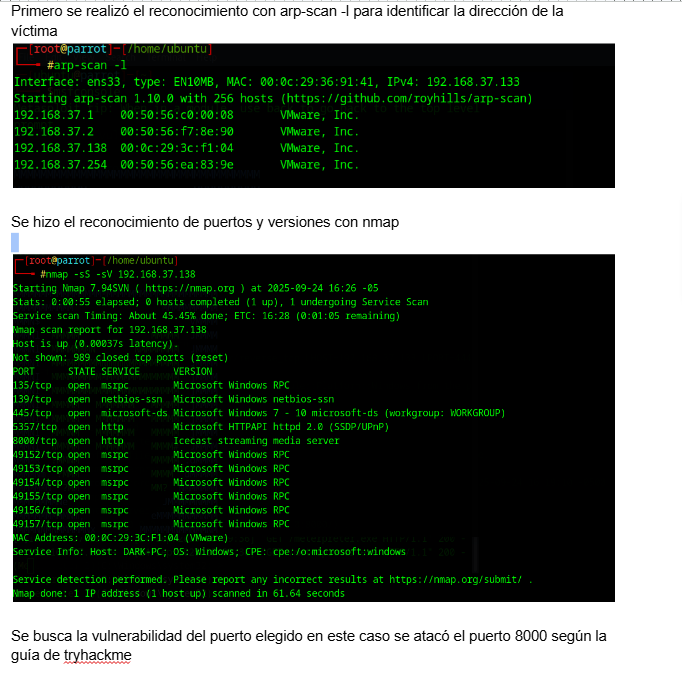 monseigneurpatas/thm-ice-icecast-rce-privesc
Full compromise of TryHackMe's Ice machine — Icecast 2.0.1 RCE (CVE-2004-1561) via buffer overflow, followed by Windows privilege escalation through…