
throttlestop-exploit-rw
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
binary-exploitationeducationexploitation+3
amrhuss/throttlestop-exploit-rwArbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 chompie1337/windows_lpe_afd_cve-2023-21768
Local privilege escalation exploit for CVE-2023-21768 targeting Windows AFD driver. Elevates arbitrary process to SYSTEM using I/O Ring read/write…
 guhe120/cve20131491-jit
Proof-of-concept exploit for CVE-2013-1491 using Java JIT-Spray technique to demonstrate memory corruption in JRE 7u17 on Windows 7 32-bit.
 yuanlink/cve-2022-26809
PoC and analysis for CVE-2022-26809, a Windows RPC runtime integer overflow vulnerability. Includes trigger scripts using PetitPotam-style UNC path…
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
 michealadams30/cve-2022-26809
Proof-of-concept exploit for CVE-2022-26809, a Windows RPC runtime integer overflow vulnerability. Includes trigger scripts using PetitPotam-style…
 azorfus/cve-2010-0232
Development of an exploit for privilege escalation in Windows systems ( NT / 2k / XP / 2K3 / VISTA / 2k8 / 7 ) using the vulnerability CVE-2010-0232
 fsecurelabs/cve-2016-7255
An exploit for CVE-2016-7255 on Windows 7/8/8.1/10(pre-anniversary) 64 bit
 synacktiv/windows-kernel-segmentheap-aligned-chunk-confusion
PoC exploiting Aligned Chunk Confusion on Windows kernel Segment Heap
 darksprings/cve-2021-38639
Windows win32k ascension UAC poc
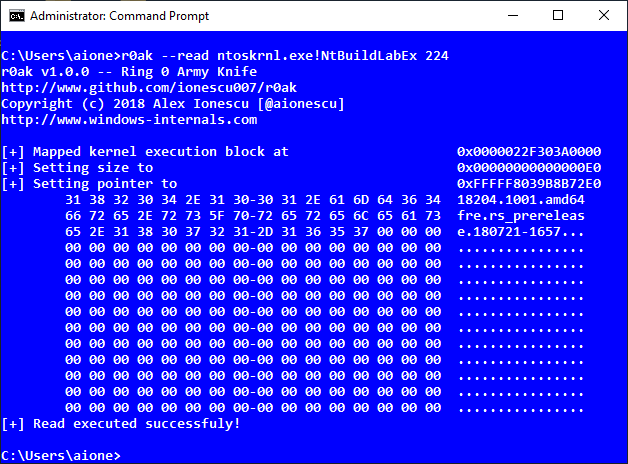 harryanon/r0ak
Windows command-line utility for reading, writing, and executing kernel-mode code from Administrator context using a font validation execution…
 de7ec7ed/cve-2016-0040
64-bit Windows kernel privilege escalation exploit for CVE-2016-0040 (WMI Receive Notification vulnerability) using GDI bitmap manipulation for token…
 syrins/cve-2025-8088-winrar-tool-gui
A Windows GUI tool demonstrating a proof-of-concept archive traversal technique related to CVE-2025-8088 using WinRAR’s CLI. Allows building crafted…
 int0/cve-2015-1769
Proof-of-concept exploit for CVE-2015-1769 using a crafted VHD file and symbolic link to trigger a Windows privilege escalation via Mount Manager.
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 donkey0xshot/cve-2017-11882-blocker
Kernel-mode Windows driver that blocks CVE-2017-11882 exploitation by intercepting process creation and denying malicious child processes spawned by…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…