
CVE-2016-5195
 timwr/cve-2016-5195
CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android
android-securitybinary-exploitationexploitation+3
1.0k5 years ago
timwr/cve-2016-5195CVE-2016-5195 (dirtycow/dirtyc0w) proof of concept for Android
 joinchang/ghostlock-oneplus
GhostLock (CVE-2026-43499) kernel exploit for Android devices with locked bootloader

 externalist/exploit_playground
Analysis of public exploits or my 1day exploits
 cloudfuzz/android-kernel-exploitation
Hands-on workshop for learning Android kernel vulnerability analysis and exploitation, with Docker-based build environment and practical exercises.
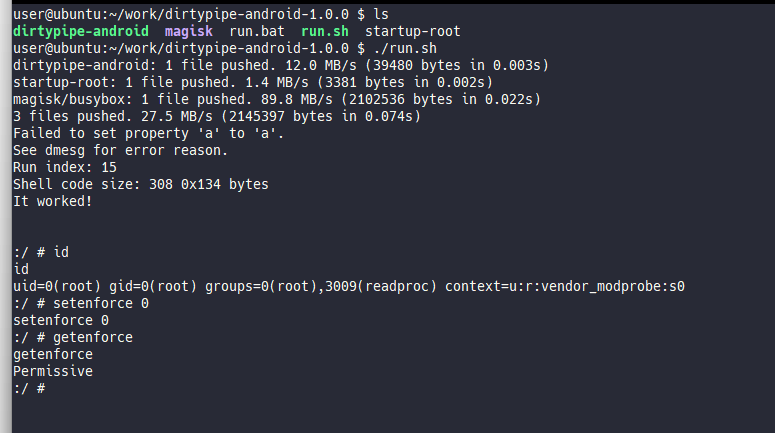 polygraphene/dirtypipe-android
Dirty Pipe root exploit for Android (Pixel 6)
 0x36/pixel_gpu_exploit
Android 14 kernel exploit for Pixel7/8 Pro
 grant-h/qu1ckr00t
A PoC application demonstrating the power of an Android kernel arbitrary R/W.
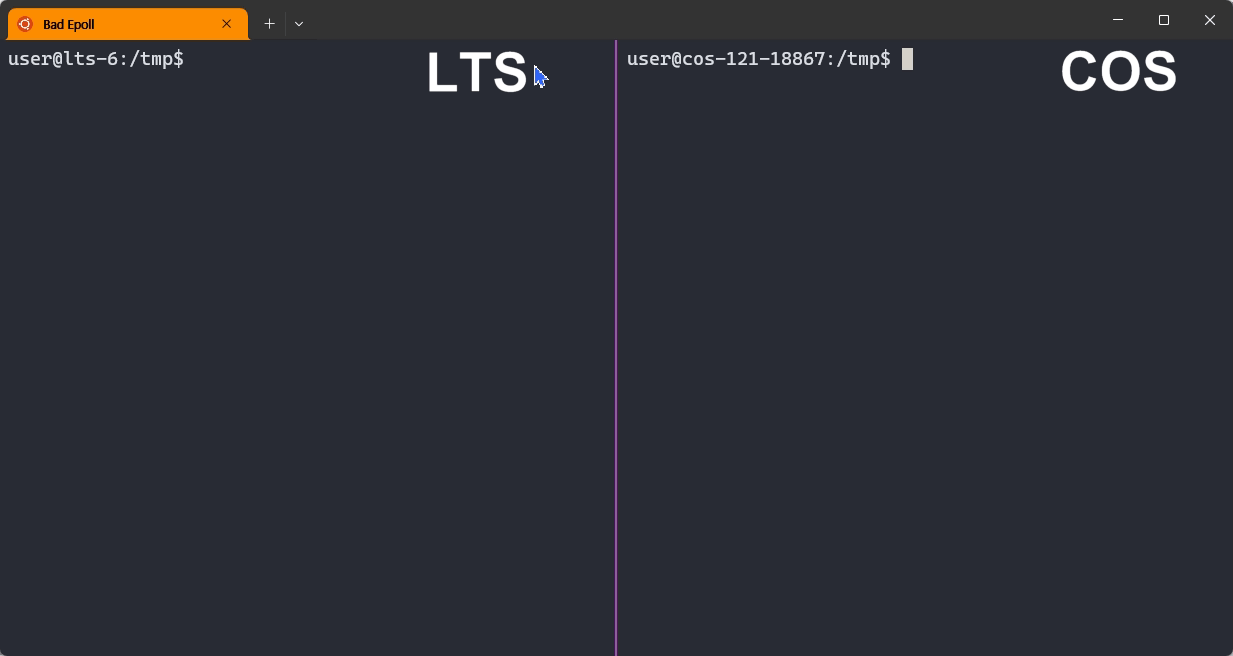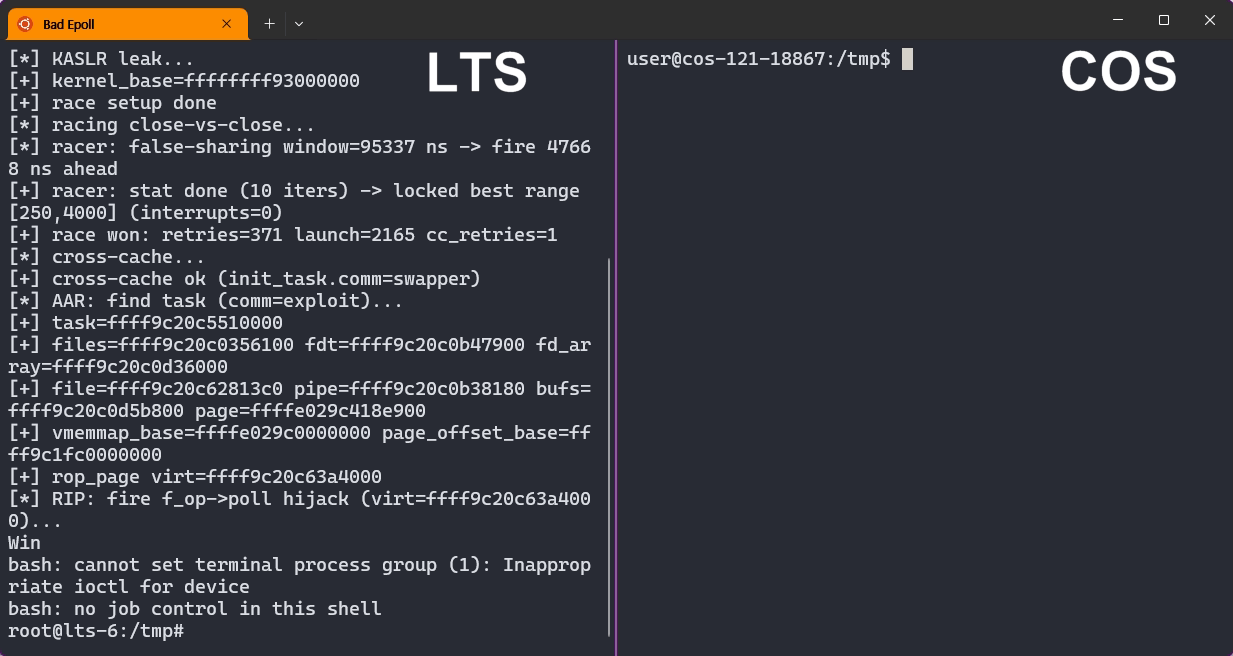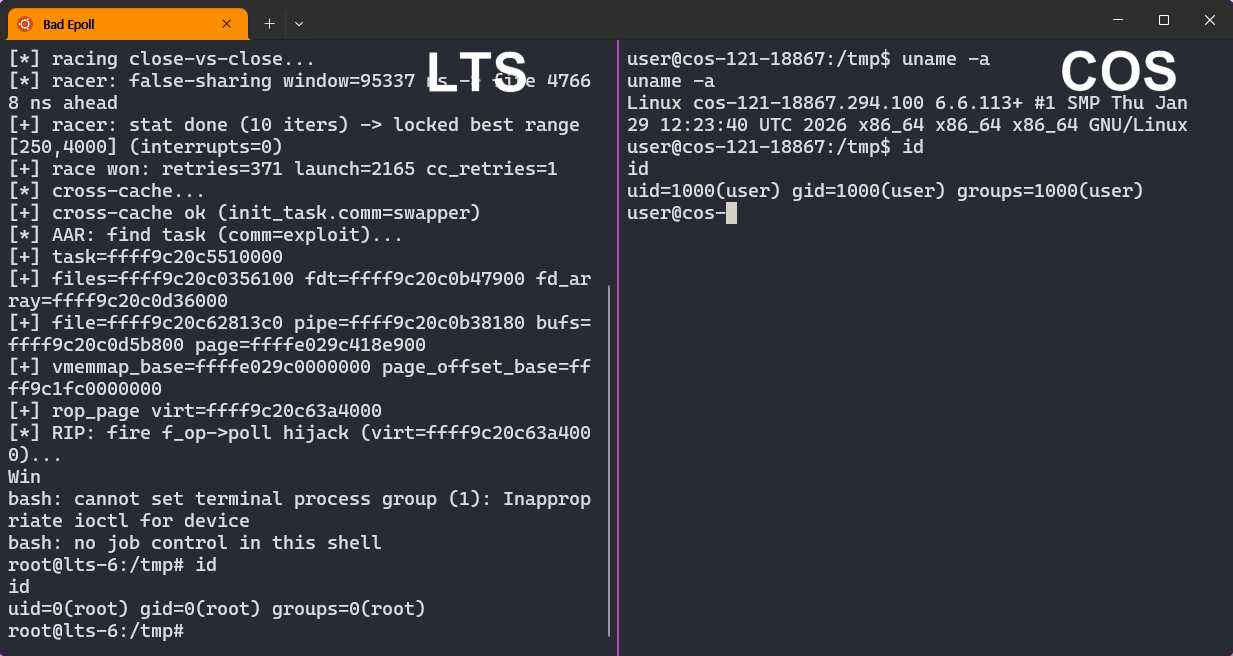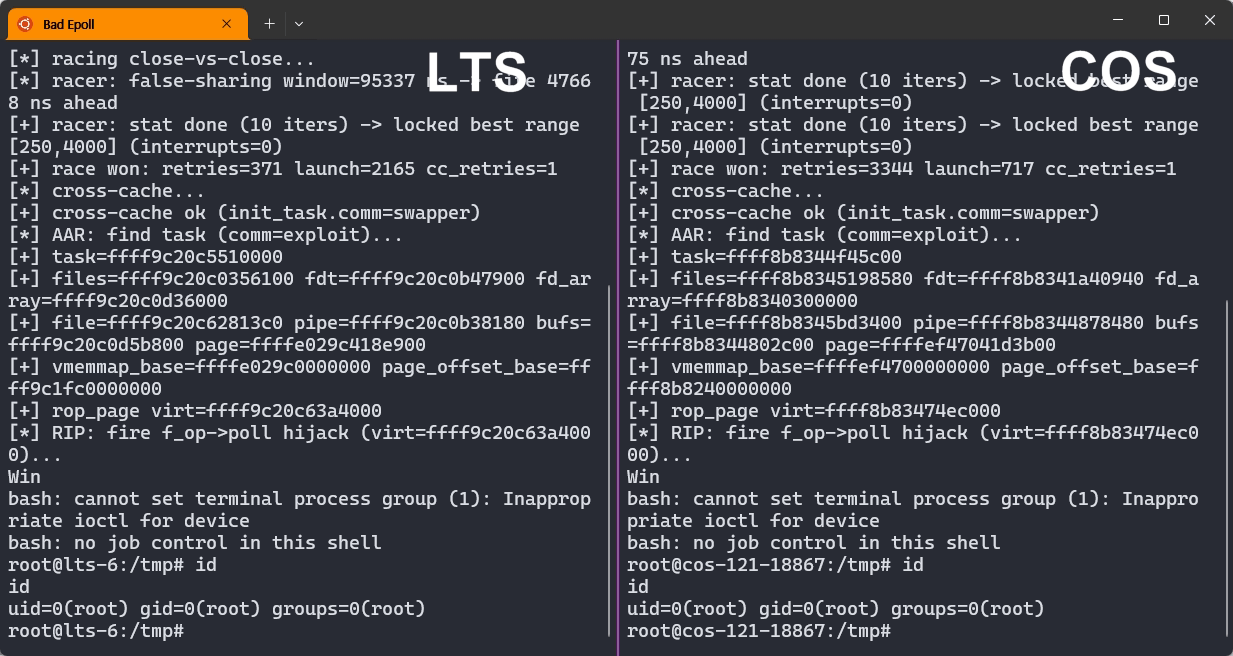 j-jaeyoung/bad-epoll
Linux kernel privilege-escalation exploit for CVE-2026-46242, a race-condition use-after-free in epoll, with 99% reliable root on desktops, servers,…
 x-spy/cve-2026-43499-popsicle
CVE-2026-43499 Implementation for 6.12.23-android16-5-g75e9b1c7ae7c-abogki463945075-4k
 laginimaineb/extractkeymaster
Exploit that extracts Qualcomm's KeyMaster keys using CVE-2015-6639 and CVE-2016-2431
 jduck/cve-2015-1538-1
Python exploit for CVE-2015-1538-1 targeting Stagefright's 'stsc' MP4 atom integer overflow to achieve remote code execution and a reverse shell on…
 northbit/metaphor
Metaphor - Stagefright with ASLR bypass
 michalbednarski/leakvalue
Exploit for CVE-2022-20452, privilege escalation on Android from installed app to system app (or another app) via LazyValue using Parcel after…
 flankerhqd/vendor-android-cves
Collections of my POCs for android vendor CVEs
 bluefrostsecurity/cve-2020-0041
Exploits for Android Binder bug CVE-2020-0041
 0xkol/badspin
Bad Spin: Android Binder Privilege Escalation Exploit (CVE-2022-20421)
 farazsth98/chronomaly
Android kernel exploit for CVE-2025-38352, previously exploited in-the-wild. Targets vulnerable x86_64 Linux kernels v5.10.x.