
CVE-2025-7771
 xm0kht4r/cve-2025-7771
A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…
binary-exploitationmalware-analysispost-exploitation+3
10
xm0kht4r/cve-2025-7771A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…
 highandhigh/cve-2015-0057
Detailed technical analysis and exploit implementation for CVE-2015-0057, a win32k.sys use-after-free vulnerability, covering 32-bit and 64-bit…
 aperikube/pwn-arm-nfc
ARM buffer overflow challenge exploiting NFC tag input on Raspberry Pi. Includes hardware assembly guide, server code, and flag retrieval for CTF and…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 rizinorg/cutter
Free and Open Source Reverse Engineering Platform powered by rizin
 gallopsled/pwntools
CTF framework and exploit development library
 pwndbg/pwndbg
Exploit Development and Reverse Engineering with GDB & LLDB Made Easy
 angr/angr
A powerful and user-friendly binary analysis platform!
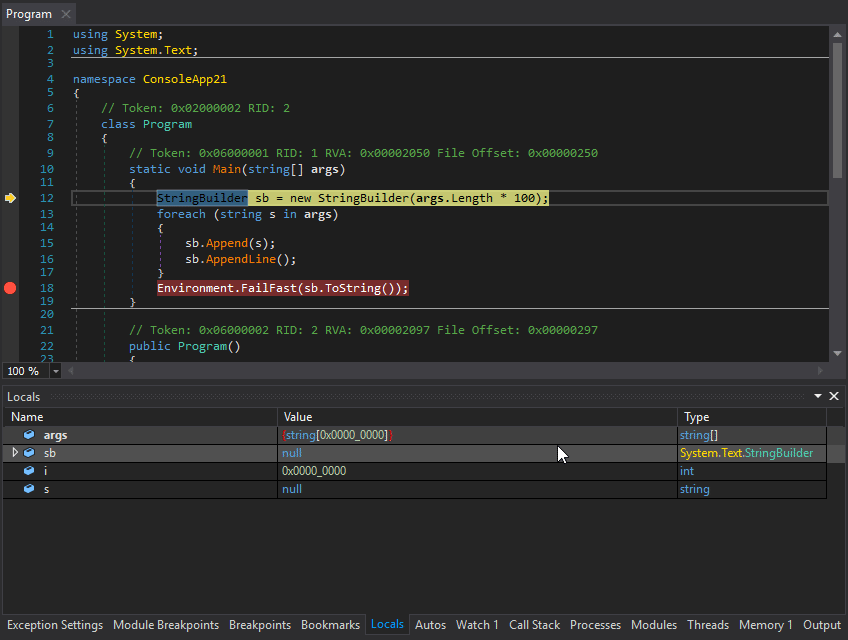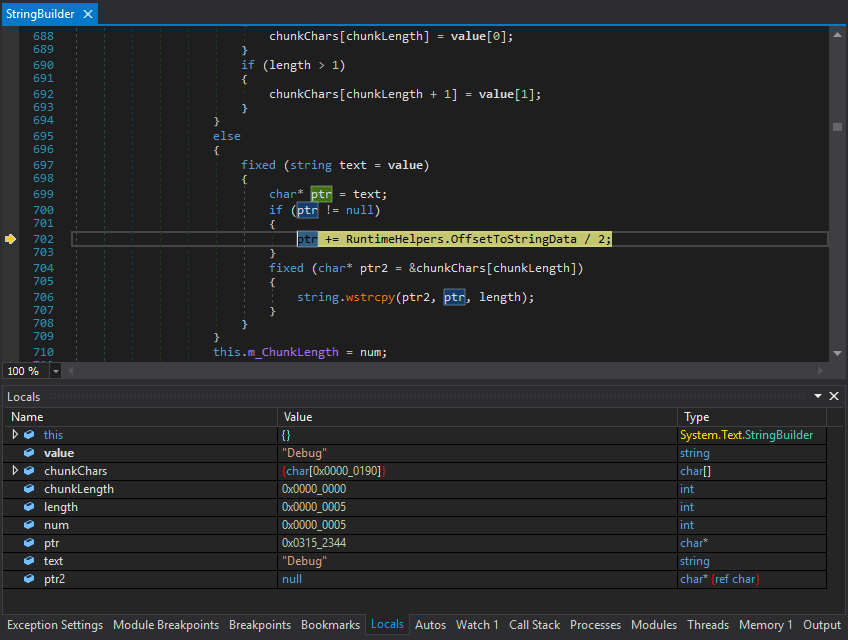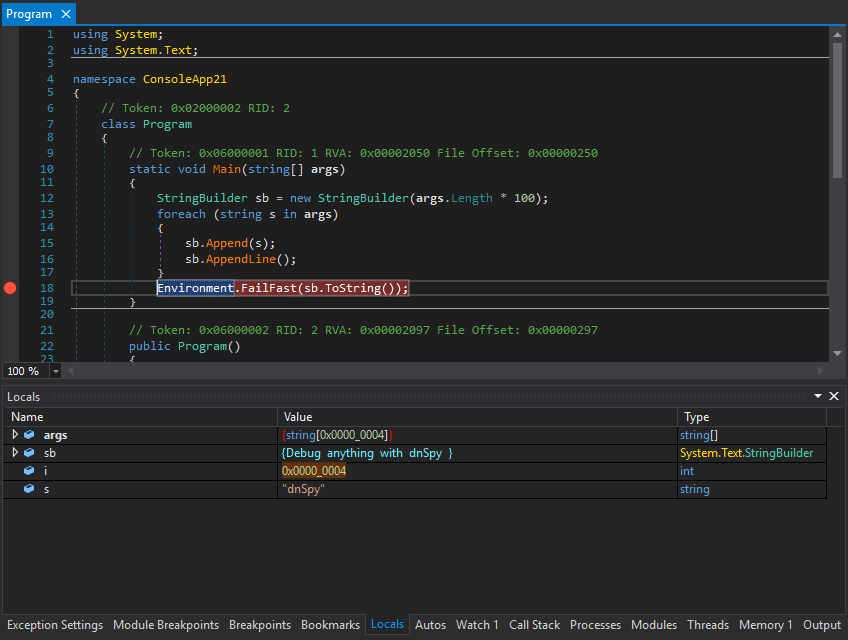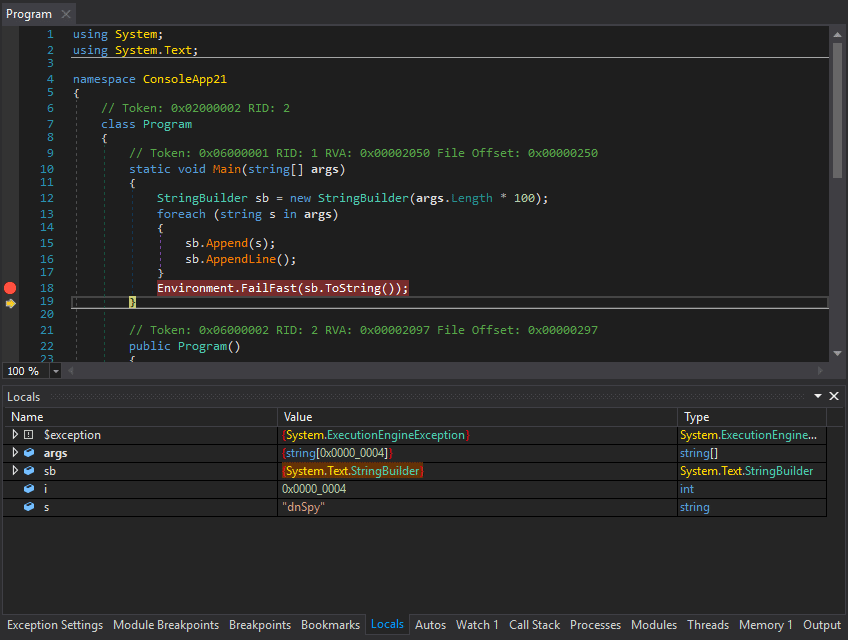 dnspyex/dnspy
Unofficial revival of the well known .NET debugger and assembly editor, dnSpy
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
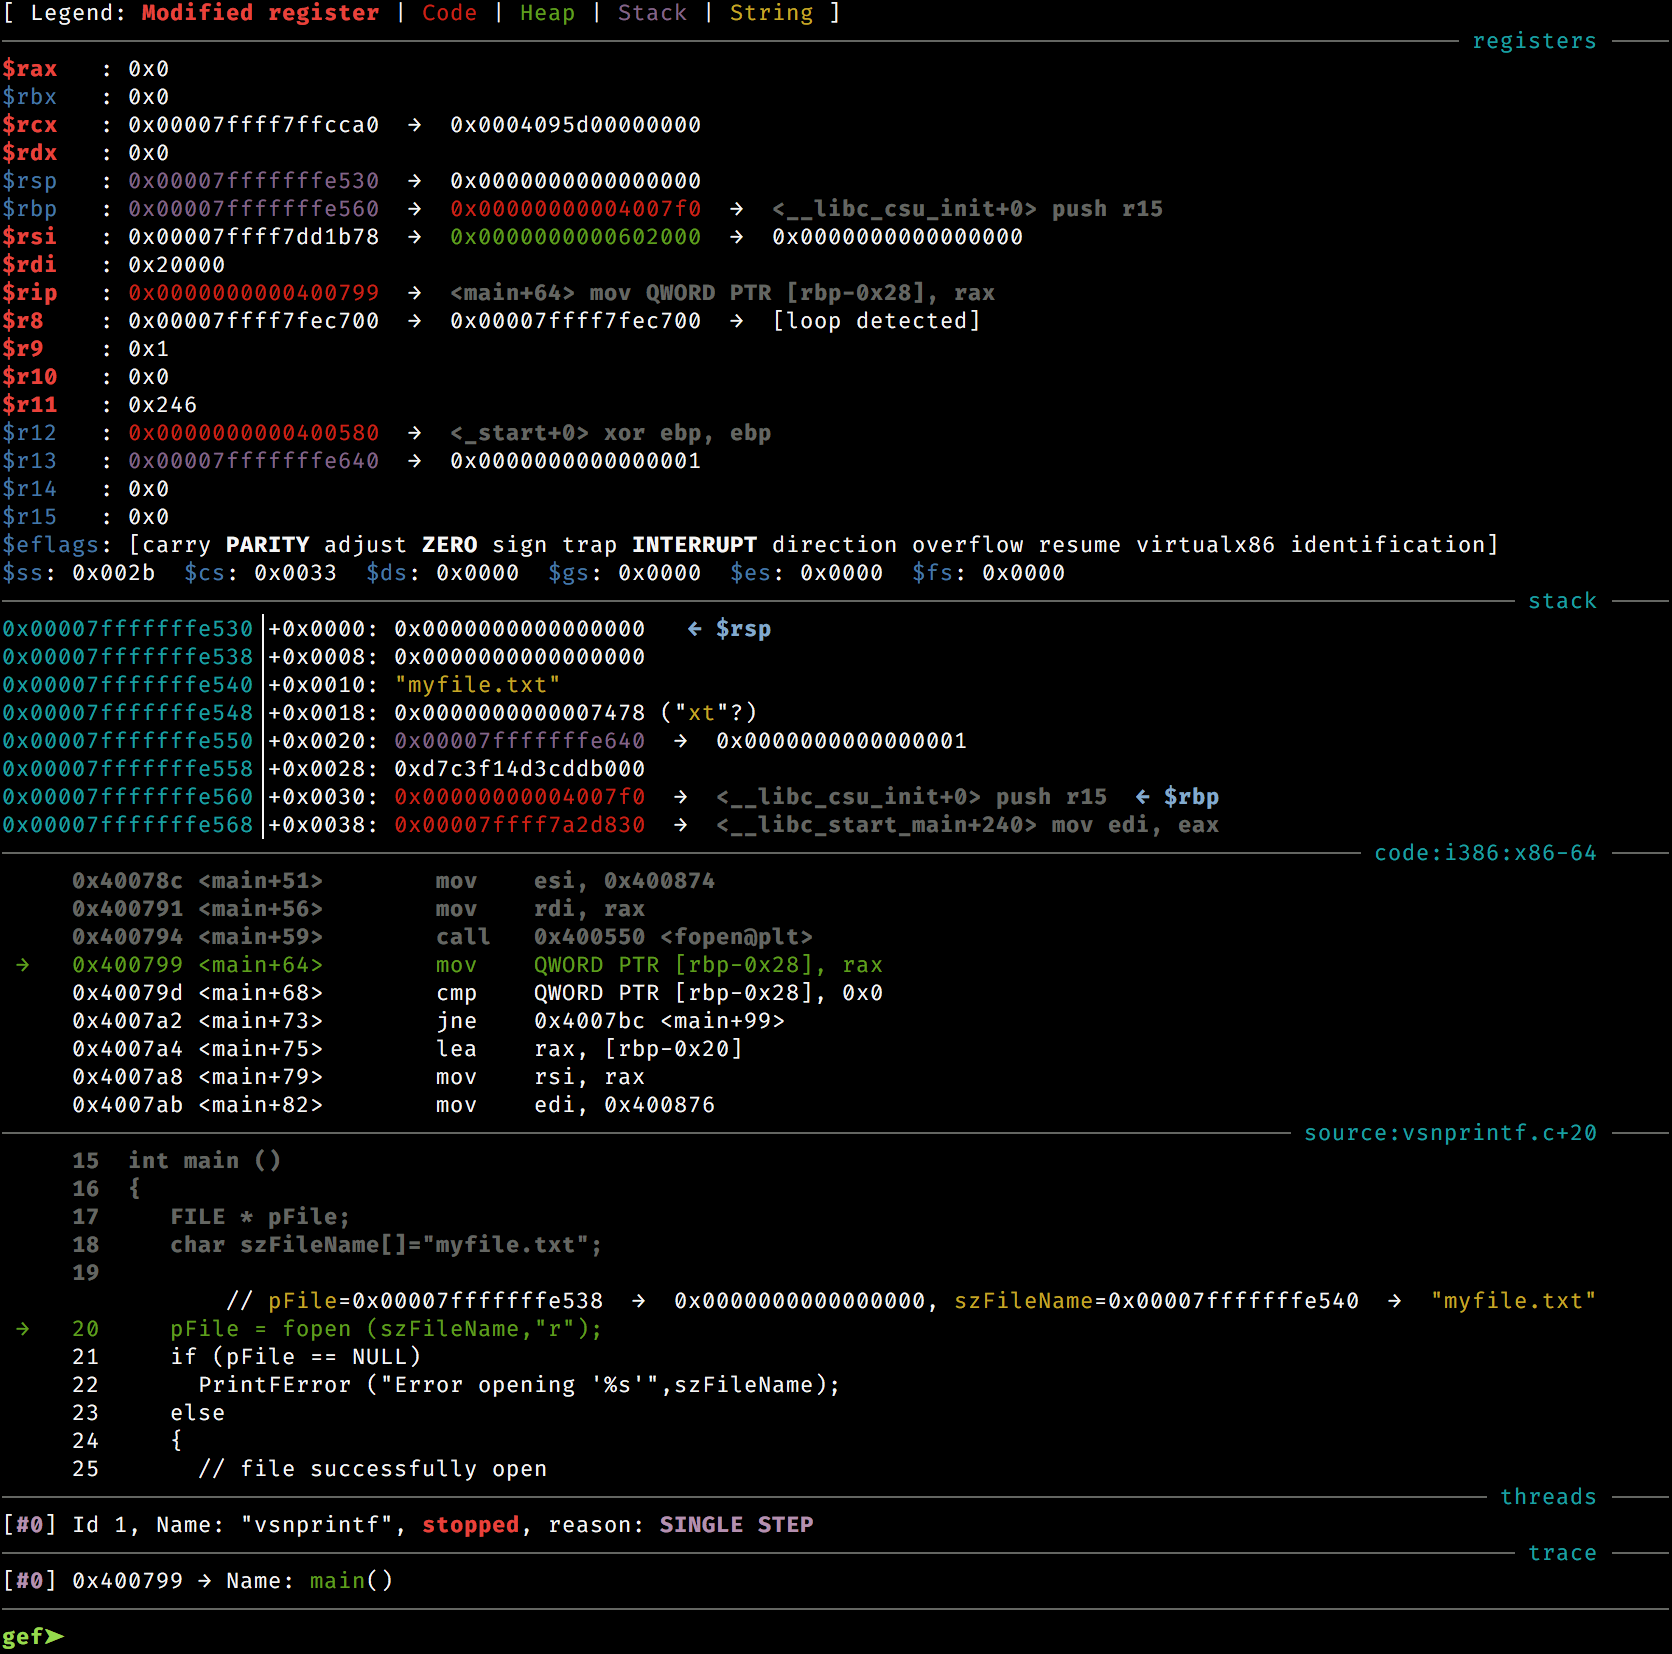 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 unicorn-engine/unicorn
Unicorn CPU emulator framework (ARM, AArch64, M68K, Mips, Sparc, PowerPC, RiscV, S390x, TriCore, X86)
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 ljagiello/ctf-skills
Agent skills for solving CTF challenges - web exploitation, binary pwn, crypto, reverse engineering, forensics, OSINT, and more
 longld/peda
PEDA - Python Exploit Development Assistance for GDB
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.