
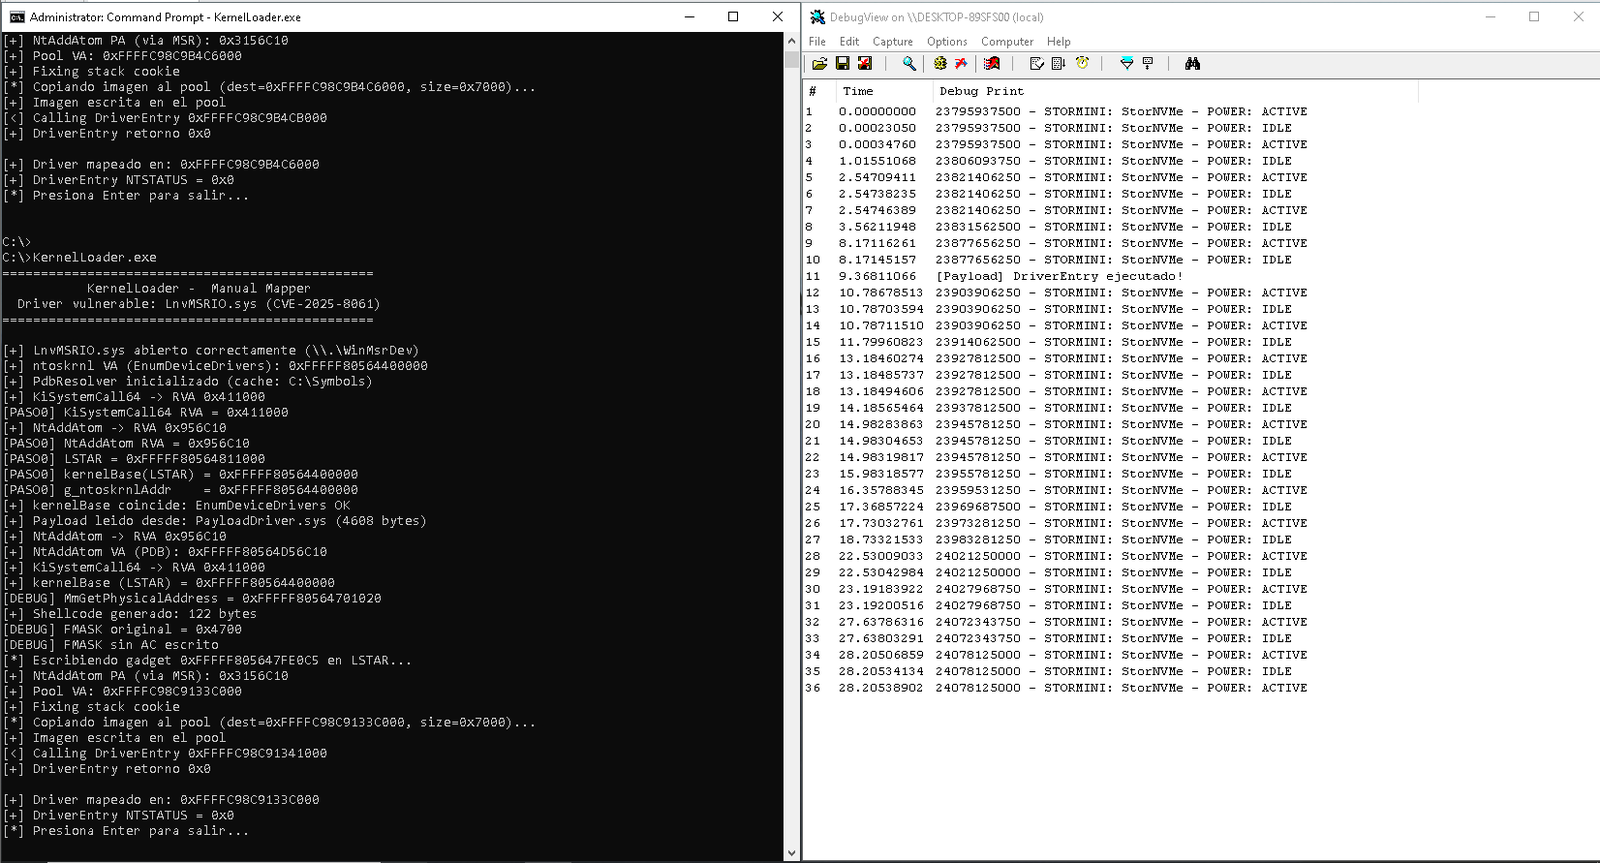
MSRMapper
 ull0a/msrmapper
Manual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
binary-exploitationexploitationmemory-forensics+6
1
ull0a/msrmapperManual kernel driver mapper for Windows x64 that abuses CVE-2025-8061 in Lenovo's LnvMSRIO.sys to perform a BYOVD attack, mapping PE64 drivers into…
 einstein2150/cve-2022-48565-poc
A proof-of-concept for CVE-2022-48565 - python plistlib XML deserialisation attack
 thomrgn/xzutils_backdoor_obfuscation
Script to obfuscate a payload the same way as it was done by the XZ utils attack (CVE-2024-3094)
 tare05/intel-cve-2015-2291
PoC exploit for CVE-2015-2291
 c0d331ng/blackash-cve-2025-48593
CVE-2025-48593
 davidbuchanan314/monomorph
MD5-Monomorphic Shellcode Packer - all payloads have the same MD5 hash
 spiralbl0ck/microc-u-os2-vuln-code-extracted-from-
Buffer Overflow Attack and Prevention for an FPGA Based Soft-Processor System - 7th International Conference on Innovation in Electronics and…
 0xc4r/cve-2026-21508_poc
Proof-of-concept for CVE-2026-21508, demonstrating a DLL hijacking attack on Windows 11 that escalates privileges by loading a crafted DLL into…
 brianwrf/cve-2017-4878-samples
CVE-2017-4878 Samples - http://blog.talosintelligence.com/2018/02/group-123-goes-wild.html
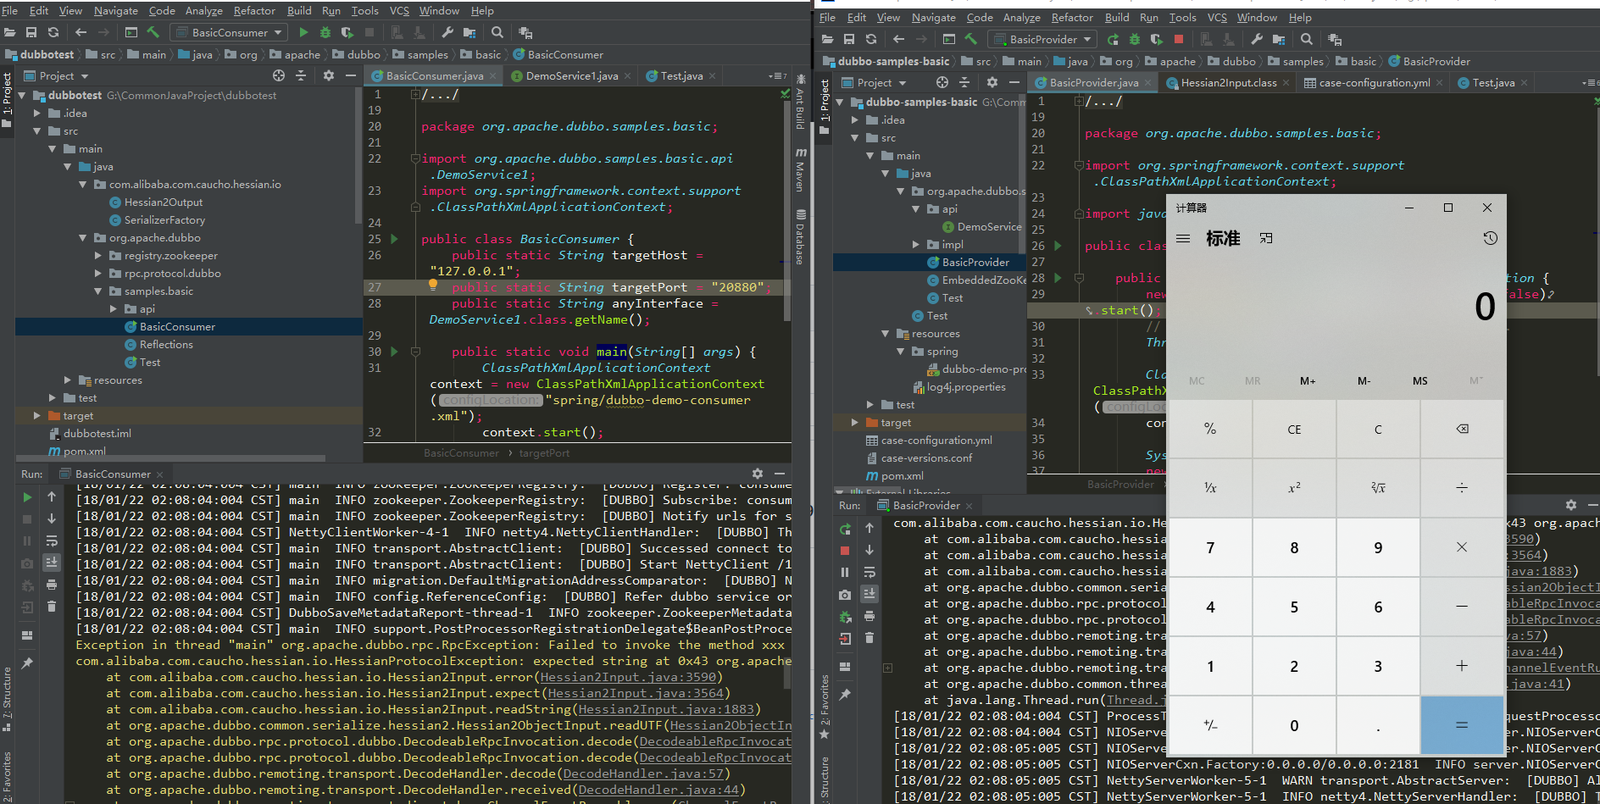 longofo/apache-dubbo-hessian2-cve-2021-43297
Demonstrates a proof-of-concept exploit for CVE-2021-43297, a deserialization vulnerability in Apache Dubbo's Hessian2 protocol, with provider and…
 afbase/cve-2017-10952
Demonstrates a local code execution exploit for Foxit PDF Reader via XFA-based PDFs, with step-by-step attack reproduction and extension to related…
 maxime288/cve-2026-8838-rce
Educational PoC for CVE-2026-8838, a critical RCE vulnerability in Amazon Redshift Python Driver via unsafe eval() in vector_in(). Includes technical…
 danieltangnes/cve-2026-3888
Proof-of-concept exploit for CVE-2026-3888, written in C. Demonstrates vulnerability exploitation and binary-level attack techniques for security…
 guard-wait/cve-2025-38248_exp
C exploit for CVE-2025-38248 supporting ROP and data-only attack techniques for binary exploitation research and vulnerability verification.
 stp1t/cve-2025-27591
Exploit for CVE-2025-27591, a local privilege escalation in the Below service, leveraging a world-writable directory and symlink attack to modify…
 rooobeam/pickle-deserialization-exploit-in-transformers
This study analyzes Python pickle deserialization vulnerabilities, focusing on CVE-2024-3568 in Hugging Face Transformers' TFAutoModel. We reproduce…
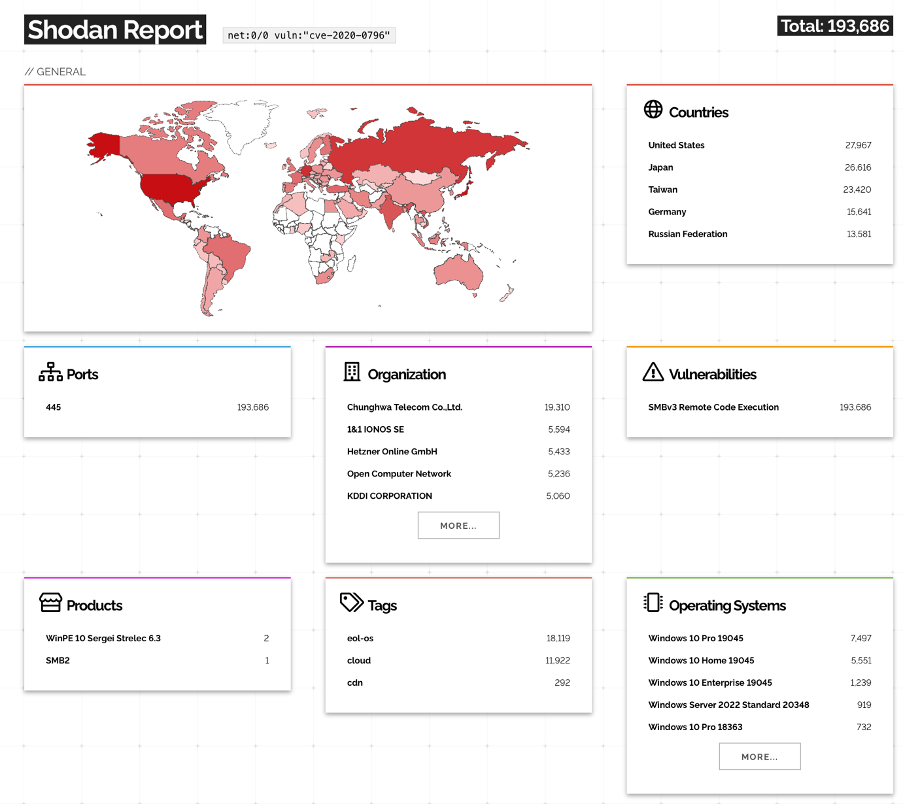 maqeel-git/cve-2020-0796
Analysis and ethical exploitation guide for CVE-2020-0796 (SMBGhost) SMBv3 vulnerability with technical details and practical attack plan.
 tiagob0b/cve-2021-40444
Malicious DOCX generator exploiting CVE-2021-40444 (Microsoft Office Word RCE) with CAB-based DLL side-loading and CAB-less RAR/WSF attack chains for…