
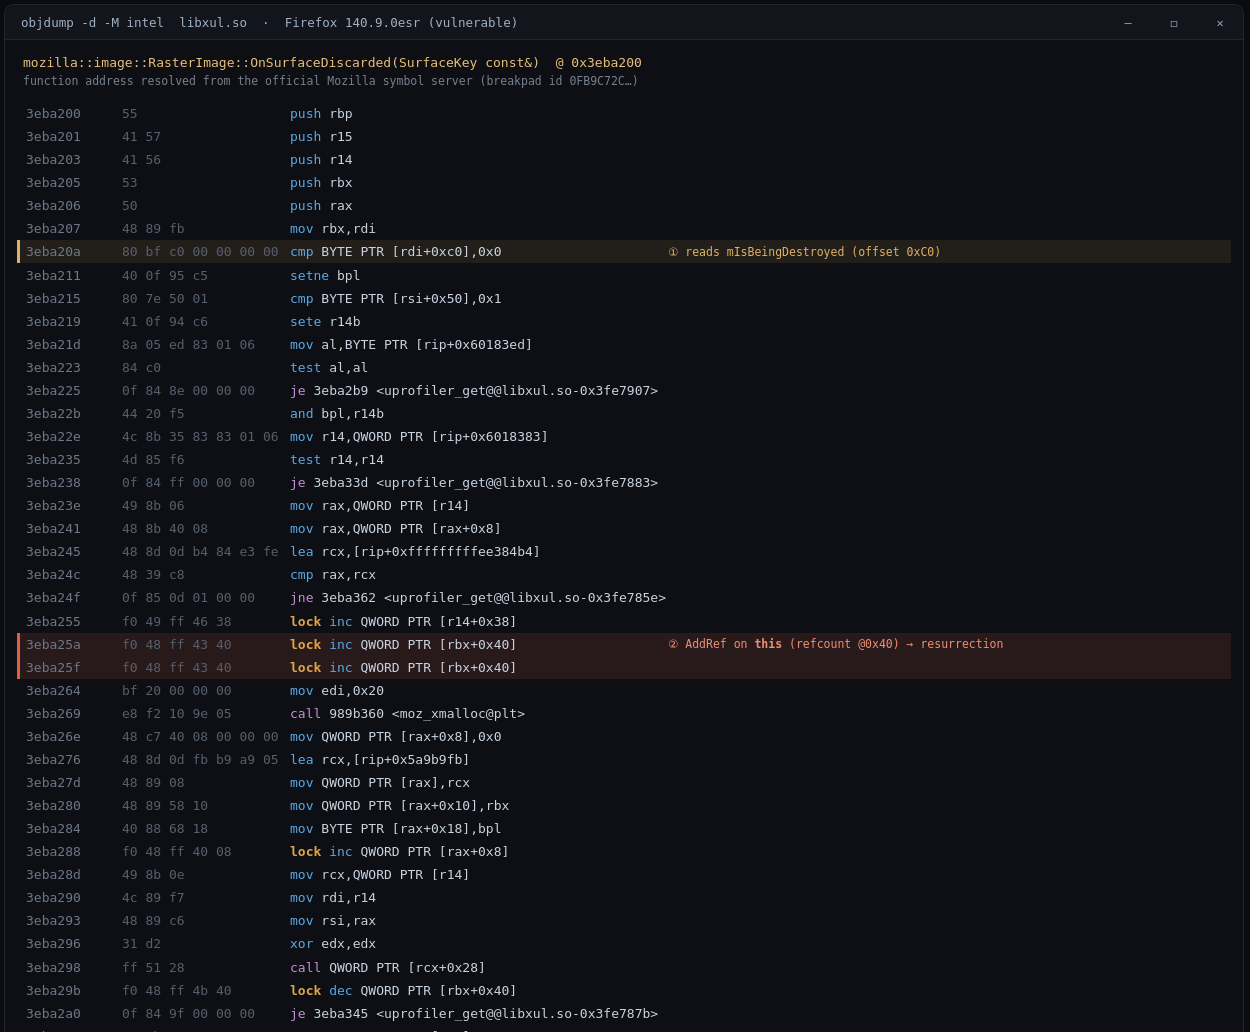
Revenant
 defineid/revenant
CVE-2026-74943, Use after free in Firefox RasterImage (sec-high)
binary-analysisbinary-exploitationcode-analysis+3
defineid/revenantCVE-2026-74943, Use after free in Firefox RasterImage (sec-high)
 ctn-qvo/cve-2026-0073-android-adbd-bypass-poc_zh_cn
CVE-2026-0073-Android-ADBD-bypass-POC汉化版
 zychen027/cve-2026-43499_hw-clt-al01
Generates per-device kernel offsets from boot.img and compiles a preload library to exploit CVE-2026-43499 Android arm64 local privilege escalation.
 x3ero0/android712-blueborne
Android Blueborne RCE CVE-2017-0781
 droidvoider/dirtycow-replacer
CVE-2016-5195 dirtycow by timwr automated multi file patch tool
 kagancapar/cve-2021-47881
PoC and analysis of a local stack-buffer-overflow in dataSIMS Avionics ARINC 664-1 v4.5.3, with payload breakdown, reproduction script, and CVE…
 vaginessa/cve-2020-0041-pixel-3a
Local privilege escalation exploit for Android Binder bug CVE-2020-0041 (Pixel 3a)
 pro-me3us/cve_2022_38181_gazelle
CVE-2022-38181 POC for FireTV 3rd gen Cube (gazelle)
 infiniteloopers/cve-2019-11932
Technical write-up and exploit code for CVE-2019-11932, a double-free vulnerability in WhatsApp for Android that leads to remote code execution via a…
 mutur4/cve-2019-2215
This is a critical UAF vulnerability exploit that affected the android binder IPC system used in the wild and discovered by P0
 boredpentester/abl_rop
Experimenting with CVE-2022-20120 (Pixel Bootloader / ABL) using Unicorn, derived from eShard's emulator at…
 fcy10012/cve-2024-31317-deployer
CVE-2024-31317 Android Zygote命令注入漏洞研究与部署工具 | Android 9-13 漏洞利用框架
 sparrow-labz/cve-2020-0423
Researching CVE published originally by longterm.io
 oguzhantopgul/cve-2015-1538-1
An exploit for CVE-2015-1538-1 - Google Stagefright ‘stsc’ MP4 Atom Integer Overflow Remote Code Execution
 szymonh/android-gadget
CVE-2022-20009 - Description and sample exploit for Android USB Gadgets
 xiaobailovesstirring/cve-2025-48595-exploit
CVE-2025-48595 Android Framework Integer Overflow PoC - 优化版
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…