
rmg-s9180-fzg1
 hackyangwen-lgtm/rmg-s9180-fzg1
Root My Galaxy SM-S9180 (dm3q) S9180ZHS8FZG1 payload port - CVE-2026-43499 + KernelSU LKM
android-securitybinary-exploitationexploitation+4
7
hackyangwen-lgtm/rmg-s9180-fzg1Root My Galaxy SM-S9180 (dm3q) S9180ZHS8FZG1 payload port - CVE-2026-43499 + KernelSU LKM
 walidpyh/cve-2025-8088
Proof-of-concept demonstrating Alternate Data Stream (ADS) payload delivery via crafted WinRAR archives for educational research and controlled lab…
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…
 lonelyor/cve-2026-31431-exp
C and Rust exploit for CVE-2026-31431 with payload encryption, cache writeback, adaptive chunking, and multi-architecture support (x86, ARM, i386).
 syrins/cve-2025-8088-winrar-tool-gui
A Windows GUI tool demonstrating a proof-of-concept archive traversal technique related to CVE-2025-8088 using WinRAR’s CLI. Allows building crafted…
 kongqbin/cve-2016-5195
Educational implementation of the Dirty COW (CVE-2016-5195) privilege escalation exploit, including race condition payload and SUID-based root shell…
 whatswrongandwhy/cve-2021-3156
Proof-of-concept exploit for CVE-2021-3156, a heap-based buffer overflow in sudo that allows local privilege escalation to root. Includes…
 imeiplus/galaxy-a37-root
CVE-2026-43499 exploit payload for Samsung Galaxy A37 (A376BXXS4AZG4, kernel 6.1.138-android14-11)
 bobikl/cve-2026-43499-t807d
Android kernel exploit research package for CVE-2026-43499, containing popsicle exploit source, embedded su payload, root bridge helper, and…
 oldthree3/cve-2019-12735-vim-neovim
Proof-of-concept exploit for CVE-2019-12735 demonstrating arbitrary command execution via Vim/Neovim modeline feature. Includes shellcode injection…
 vidura2/cve-2024-46451
Python exploit for TOTOLINK AC1200 T8 buffer overflow vulnerability (CVE-2024-46451) with customizable payload generation and response logging for…
 rosnlr5/modrosnlr5
Proof-of-concept exploit for Linux kernel CVE-2026-31431, leveraging AF_ALG sockets to escalate privileges to root via payload injection and shell…
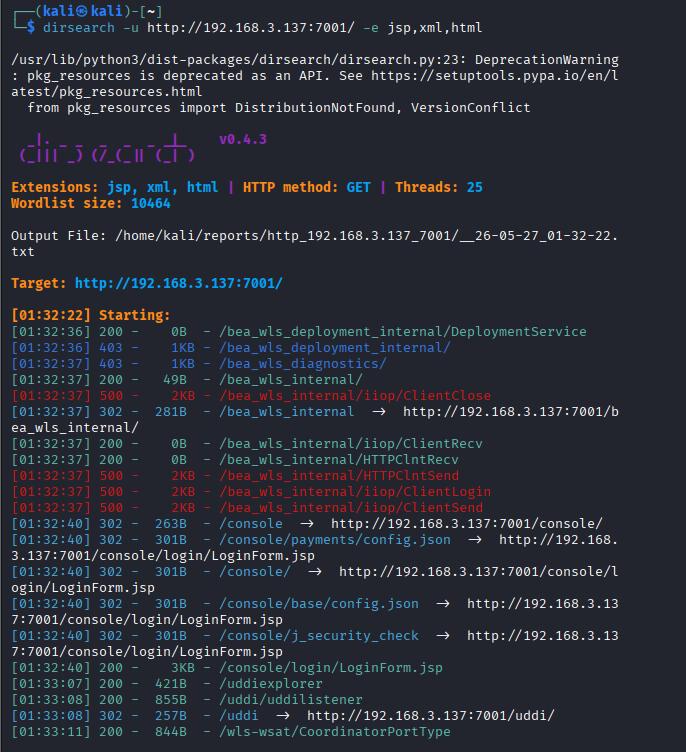 dungsocool/cve-2017-10271
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
 likekabin/cve-2019-5736
Destructive Docker container escape exploit for CVE-2019-5736, overwriting host /usr/bin/docker-runc with a payload triggered via docker exec.
 secvulnhub/cve-2025-32463-exploit
Proof-of-concept exploit for CVE-2023-42456, demonstrating privilege escalation via sudo NSS library hijacking through chroot injection. Includes…
 notthemystery/cve-2026-20700-poc-that-ll-never-work
Proof-of-concept exploit for CVE-2026-20700, demonstrating a specific vulnerability with a binary exploitation payload for security testing and…
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…