
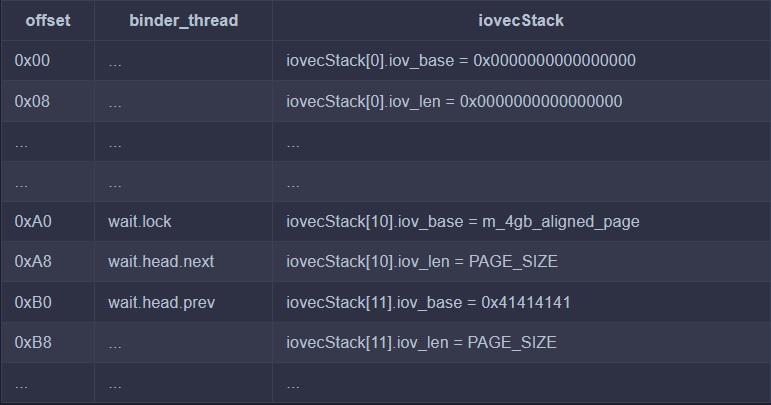
AndroidKernelVulnerability
 sharif-dev/androidkernelvulnerability
Triggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
android-securitybinary-exploitationdynamic-analysis-sandboxing+5
73
sharif-dev/androidkernelvulnerabilityTriggering and Analyzing Android Kernel Vulnerability CVE-2019-2215
 hd3s5aa/cve-2023-21674
Proof-of-concept exploit for CVE-2023-21674, a Windows ALPC vulnerability enabling browser sandbox escape and SYSTEM privilege escalation via kernel…
 zeze-zeze/hitcon-2023-demo-cve-2023-20562
Demonstrates exploitation of AMD μProf driver (CVE-2023-20562) for privilege escalation via EPROCESS token write and DSE bypass, enabling unsigned…
 maxpl0it/cve-2019-17026-exploit
An exploit for CVE-2019-17026. It pops xcalc and was tested on Ubuntu (x64).
 alfarom256/logmeinpochandledup
Exploit for a LogMeIn/GoTo Windows kernel driver race condition that duplicates SYSTEM handles, enabling thread-token impersonation and local…
 k3vinlusec/bluefrag_cve-2020-0022
This is a RCE bluetooth vulnerability on Android 8.0 and 9.0
 aramosf/cve-2026-64468
Unprivileged proof-of-concept and x86_64 local privilege escalation for a Linux kernel Binder use-after-free (CVE-2026-64468), with KASAN lab and…
 tandasat/cve-2024-21305
Report and exploit of CVE-2024-21305.
 sam-b/cve-2014-4113
Trigger and exploit code for CVE-2014-4113
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
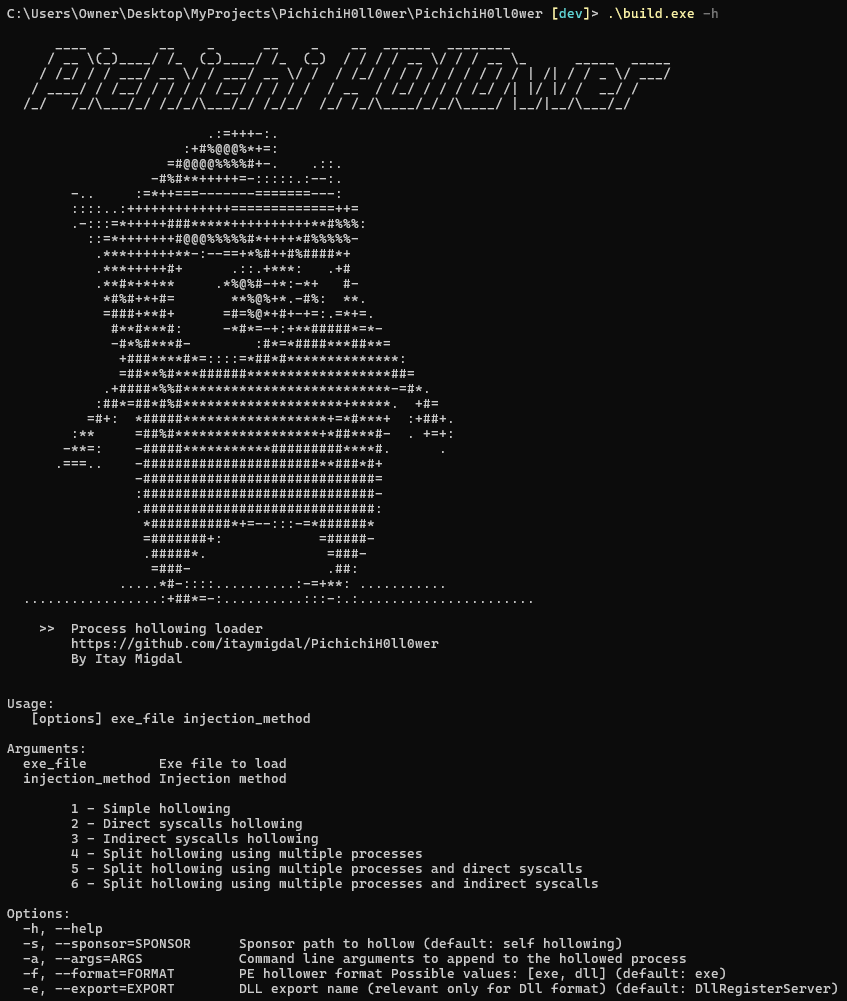 itaymigdal/pichichih0ll0wer
Nim-based process hollowing loader for PE executables with configurable injection methods, direct/indirect syscalls, anti-debug, payload encryption,…
 theofficialflow/presentations
Curated collection of security conference slides and talks on game console exploitation, kernel vulnerabilities, and sandbox escapes.
 valbrux/cve-2019-11932-supportapp
This native code file aims to be complementary to the published Whatsapp GIF RCE exploit by Awakened , by calculating the system() function address…
 xianwan1314/cve-2026-43499-poc-analysis
Vulnerability analysis and Proof of Concept (PoC) for CVE-2026-43499 affecting Xiaomi devices. For educational and research purposes only.
 sfewer-r7/cve-2025-0282
PoC for CVE-2025-0282: A remote unauthenticated stack based buffer overflow affecting Ivanti Connect Secure, Ivanti Policy Secure, and Ivanti Neurons…
 bitsbywill/ksmbd-n-day
Authenticated 0-click RCE against Linux 6.1.45 for CVE-2023-52440 and CVE-2023-4130
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 fi01/libput_user_exploit
CVE-2013-6282 kernel exploit that overwrites ptmx.fsync handler and uevent_helper string for local privilege escalation on vulnerable Linux systems.