
cve-2024-4406-xiaomi13pro-exploit-files
 yogehi/cve-2024-4406-xiaomi13pro-exploit-files
Files related to the Pwn2Own Toronto 2023 exploit against the Xiaomi 13 Pro.
android-securitybinary-exploitationexploitation+4
yogehi/cve-2024-4406-xiaomi13pro-exploit-filesFiles related to the Pwn2Own Toronto 2023 exploit against the Xiaomi 13 Pro.
 hiikezoe/libperf_event_exploit
C-based exploit for CVE-2013-2094 targeting Android kernel privilege escalation via perf_event_open syscall vulnerability.
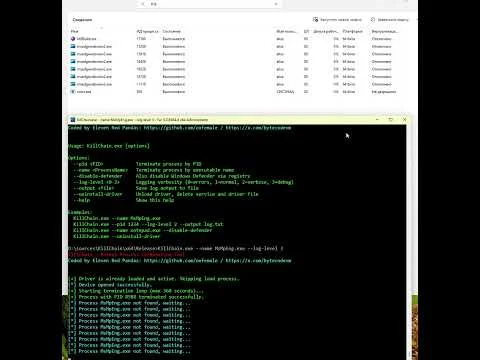 oxfemale/killchain
Kernel Process Termination Tool ( CVE-2026-0828 exploit)
 tamirzb/cve-2017-13253
PoC code for CVE-2017-13253
 quyicheng03-boop/xiaomi15-dada-cve-2026-64560
Device-bound CVE-2026-64560 adaptation for Xiaomi 15 dada OS4.0.0.8
 secmob/cve-2015-6612
Proof-of-concept exploit for Android CVE-2015-6612, demonstrating a privilege escalation vulnerability with a working PoC for security research and…
 laginimaineb/cve-2014-4322
C exploit for Android kernel vulnerability CVE-2014-4322, enabling privilege escalation on affected devices through a crafted application.
 ma4the/omae-wa-cheese-da
CVE-2025-21479 PoC for ZFlip5 with Knox in the way!(˶˃ ᵕ ˂˶)
 witaqua-tools/root-my-device
KSU installer for supported firmware with CVE-2026-43499
 cunninglogic/pixeldump_cve-2016-8462
Pixel bootlaoder exploit for reading flash storage
 michalbednarski/reparcelbug
CVE-2017-0806 PoC (Android GateKeeperResponse writeToParcel/createFromParcel mismatch)
 mdsecactivebreach/cve-2018-4878
Proof-of-concept exploit for CVE-2018-4878, a Use-After-Free vulnerability in Adobe Flash Player 32-bit, providing a ByteArray object for process…
 snothin/ghostlock-s26
GhostLock (CVE-2026-43499) for the Galaxy S26
 mobilehackinglab/ghostlock-a17
Kernel exploit for CVE-2026-43499 on Samsung Galaxy A17 achieving root via KDP bypass, KASLR recovery, and forged workqueue execution with persistent…
 flankerhqd/cve-2015-6612poc-form
Proof-of-concept exploit for CVE-2015-6612 targeting Android media decoder vulnerability. Demonstrates binary exploitation in the Android AV…
 yakidango-official/ghostlock-h80gt
Honor 80 GT privilege escalation PoC: GhostLock (CVE-2026-43499) + custom KernelSU module loading
 hyblove/iqoo-temp-root
vivo/iQOO 临时 root 工具箱 (免解锁临时root, CVE-2026-43499) - 源码与脚本
 jaf0rk/cve-2023-20938
Technical analysis and proof-of-concept exploit for CVE-2023-20938, a use-after-free vulnerability in the Android kernel's Binder driver, enabling…