
CVE-2024-7479
 fortra/cve-2024-7479
Python proof-of-concept exploit for CVE-2024-7479, demonstrating privilege escalation via BYOVDKit driver abuse against TeamViewer on Windows.
binary-exploitationexploitationexploit-frameworks+5
8
fortra/cve-2024-7479Python proof-of-concept exploit for CVE-2024-7479, demonstrating privilege escalation via BYOVDKit driver abuse against TeamViewer on Windows.
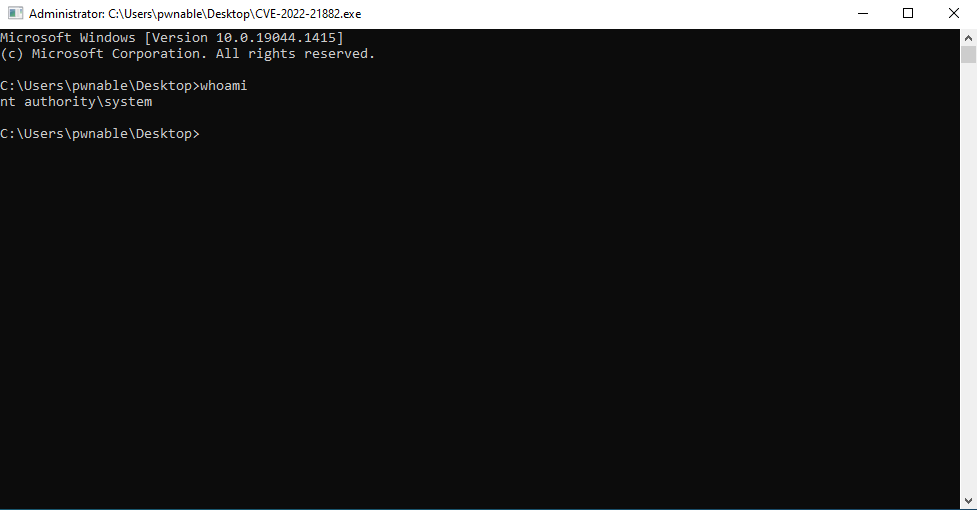 r1l4-i3pur1l4/cve-2022-21882
Win32k elevation of privilege exploit for CVE-2022-21882, providing a proof-of-concept implementation targeting Windows kernel vulnerabilities.
 hackspeak/cve-2026-62735
Local privilege escalation exploit for Windows HTTP.sys integer overflow (CVE-2026-62735), demonstrating crash and full SYSTEM shell via nonpaged…
 h4rk3nz0/cve-2023-20598-pdfwkrnl
CVE-2023-20598 Kernel Driver - Elevation of Privilege
 neo-neo6/cve-2025-65018-heap-buffer-overflow-in-libpng-ps4-ps5-
Proof-of-concept exploit for a heap buffer overflow in libpng on PS4/PS5. Generates a malicious PNG that triggers the vulnerability when opened in…
 malwarekid/cve-2026-31431
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel AF_ALG memory corruption vulnerability. Uses splice to patch /usr/bin/su in page cache,…
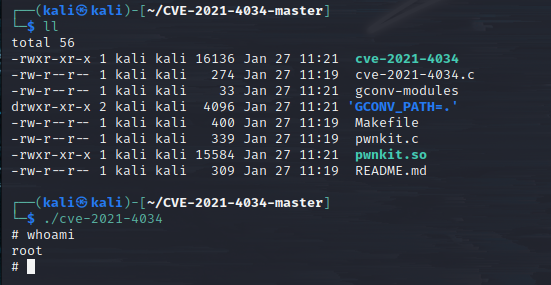 locksec/cve-2021-4034
Exploit PoC for the polkit pkexec (PWNKIT) vulnerability
 littlebin404/cve-2017-11882
CVE-2017-11882(通杀Office 2003到2016)
 juguitos/copy-fail
Python proof-of-concept for CVE-2026-31431, exploiting kernel AF_ALG to modify SUID binary page cache and spawn a root shell on Linux systems.
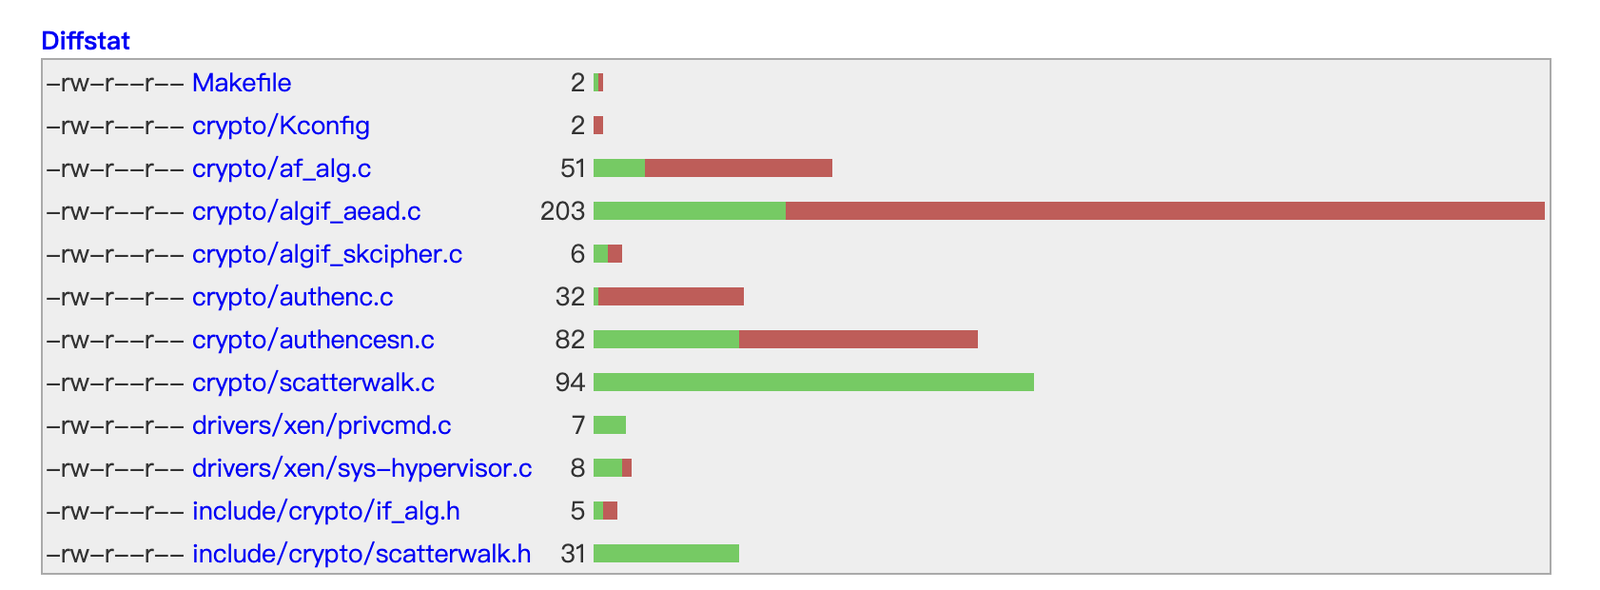 yuspring/cve-2026-31431-poc
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel privilege escalation via AF_ALG authenc length check bypass, achieving root by modifying…
 xerxes-2/cve-2026-31431-rs
Rust-based proof-of-concept for CVE-2026-31431, exploiting AF_ALG and splice to overwrite /bin/su and spawn a root shell. Self-contained no_std…
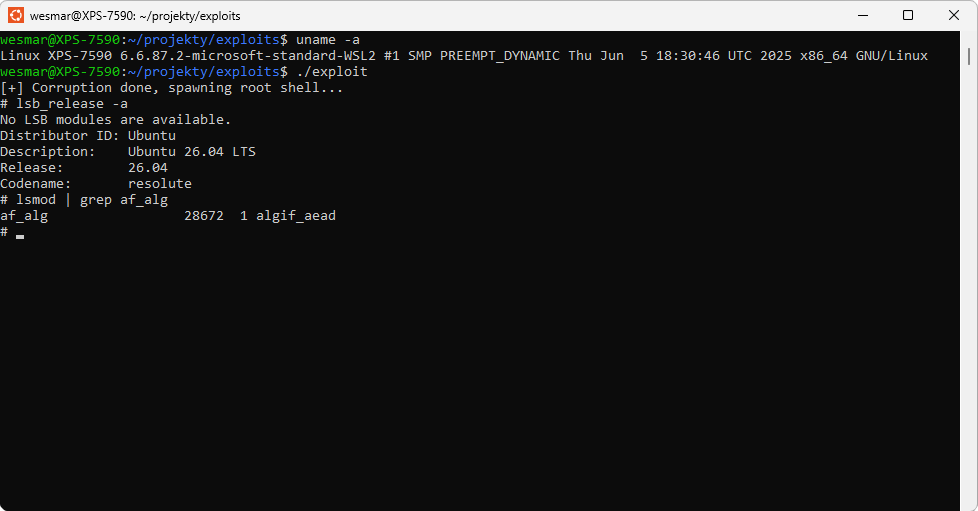 wesmar/cve-2026-31431
Working proof-of-concept exploit for CVE-2026-31431, a Linux kernel local privilege escalation via AF_ALG AEAD page cache corruption, granting root…
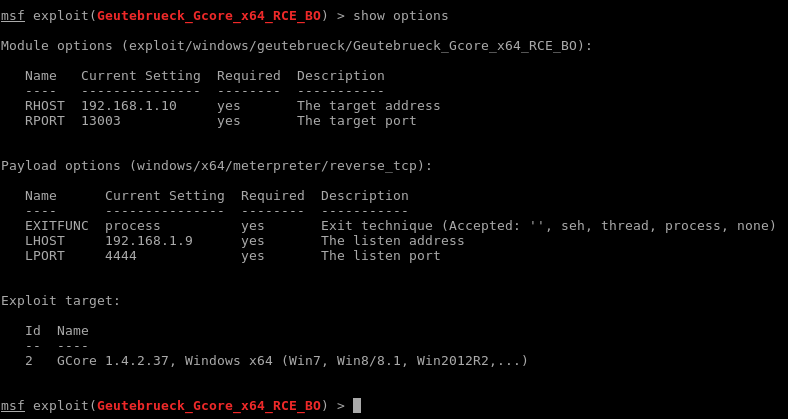 m4p0/geutebrueck_gcore_x64_rce_bo
Metasploit module for Geutebrueck GCore "video management" system. Tested with version 1.3.8.42 and 1.4.2.37
 ben-slates/cve-2026-31431-exploit
Proof-of-concept exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability enabling local privilege escalation via algif_aead.…
 spiralbl0ck/-cve-2018-0834-aab-aar
CVE-2018-0834 full code exec
 navisec/cve-2021-4034-pwnkit
Nim-based proof-of-concept for CVE-2021-4034 (PwnKit), a local privilege escalation in polkit's pkexec, with embedded payload library for standalone…
 eddinos2/cve-2026-64747
Root-cause analysis and reachability PoC for CVE-2026-64747, a buffer overflow in the AppleAVE2 kernel extension. Includes reversed IOKit wire…
 nova-master/cve-2022-21894-payload-new
C-based payload for CVE-2022-21894 that maps a second stage payload to call EFI services, extending the original PoC for Secure Boot bypass…