CVE-2017-16995-Linux-Kernel---BPF-Sign-Extension-Local-Privilege-Escalation-
 lumindu/cve-2017-16995-linux-kernel---bpf-sign-extension-local-privilege-escalation-
binary-exploitationexploitationprivilege-escalation+1
lumindu/cve-2017-16995-linux-kernel---bpf-sign-extension-local-privilege-escalation-
 oopnv70-lab/ghostlock-honor-aak-probe
该仓库已经确认此漏洞利用不可能实现、已判死刑,永久性停止更新。基于 CVE-2026-43499 (rtmutex remove_waiter UAF) 的 GhostLock exploit 半成品工程,KASLR 绕过 / 提权 / su 植入等环节均无法稳定利用,本项目永久终止。
 xlucas/dirtycow.cr
CVE-2016-5195 exploit written in Crystal
 mathisvickie/cve-2021-21551
arbitrary kernel read/write in dbutil_2_3.sys, Proof of Concept Local Privilege Escalation to nt authority/system
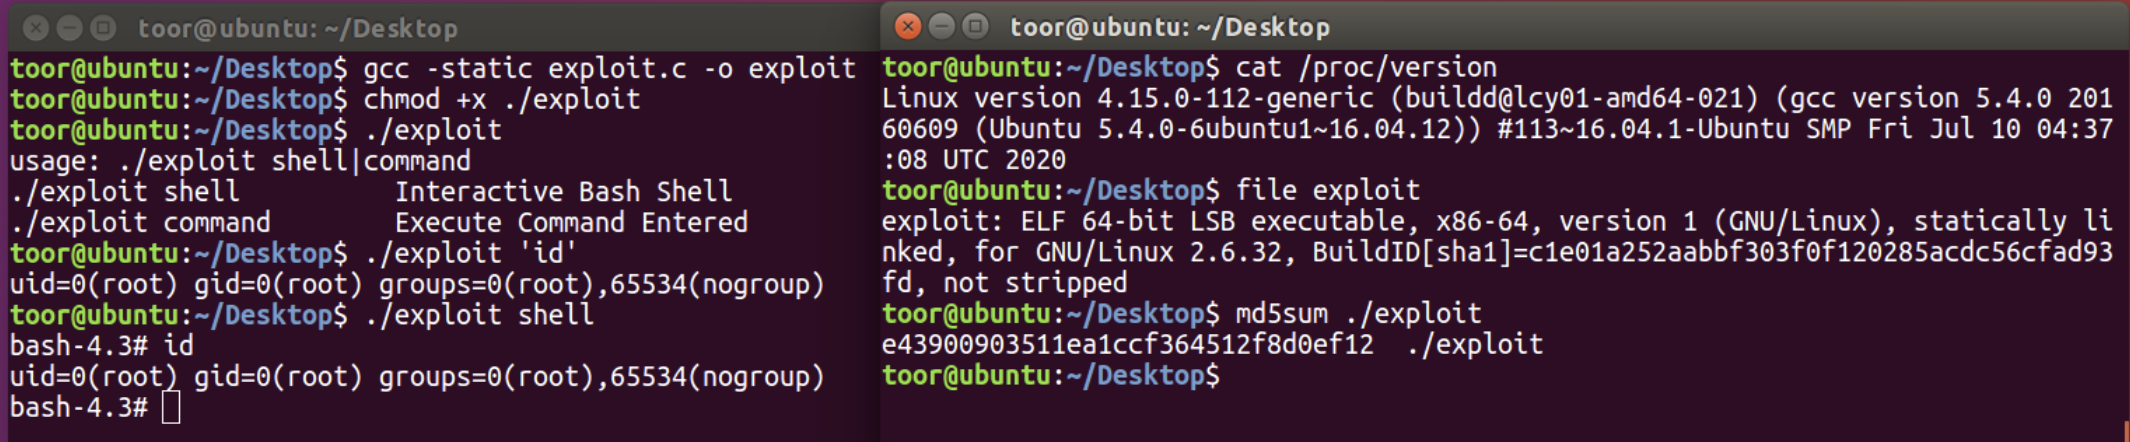 inspiringz/cve-2021-3493
CVE-2021-3493 Ubuntu OverlayFS Local Privesc (Interactive Bash Shell & Execute Command Entered)
 magisterquis/cve-2010-3847
Script to take advantage of CVE-2010-3847