
RegPwn
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
binary-exploitationexploitationpenetration-testing+4
4
tracyliving606/regpwnExploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 wangs-official/opace6-cve-2026-64560
Temporary root tool for OnePlus Ace 6 that exploits the CVE-2026-64560 Linux kernel POSIX CPU timer use-after-free to gain root until reboot, without…
 ramenfast/zenfone9-root
Temporary root (uid 0) on a bootloader-locked ASUS Zenfone 9 via CVE-2025-21479 + a perf-based physical-address leak. GPLv3.
 razureink/cve-2024-38077-madlicense_reproduction
CVE Reproduction: cve-2024-38077-madlicense_reproduction
 toxy4ny/copy-fail
Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
 redcrazyghost/cve-2026-42945
Go-based exploit tool for CVE-2026-42945 (nginx HTTP/2) with detection, crash probing, command execution, and reverse shell capabilities for…
 doaso/cve-2023-42115
Remote code execution exploit for Exim AUTH out-of-bounds write vulnerability (CVE-2023-42115). No authentication required; includes build and usage…
 kalibb/cve-2024-31317-deployer
Automated deployment tool for CVE-2024-31317, a command injection vulnerability in Android 9-13. Includes reverse shell payload, compile script, and…
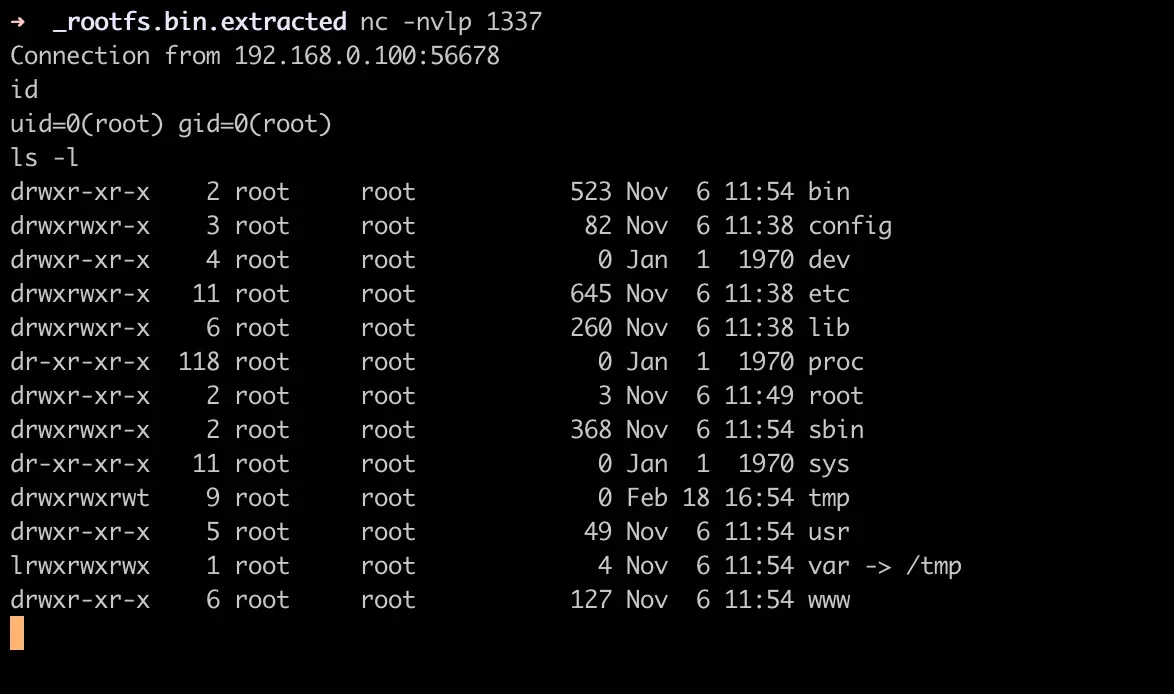 ii4gsp/cve-2026-1457
Provides a detailed analysis and proof-of-concept for CVE-2026-1457, an authenticated buffer overflow in TP-Link VIGI C385 web API leading to remote…
 thannikudam/topazterminator
C-based tool exploiting the vulnerable wsftprm.sys kernel driver to terminate protected EDR/AV processes on Windows, including PPL processes, via…
 cythonic1/cve-2025-27591
a C exploit for CVE-2025-27591, which allow an attacker to escalate privilege to root.
 obamalaolu/cve-2025-27591
CVE-2025-27591
 webldix/cve-2024-31317-poc-deployer
Automated deployment tool for CVE-2024-31317 PoC on Android 9-13, enabling privilege escalation via Zygote injection and reverse shell execution.
 teamtopkarl/cve-2025-32433
Erlang/OTP SSH 远程代码执行漏洞
 cybermads/cve-2011-2523
Python exploit for vsftpd 2.3.4 backdoor vulnerability (CVE-2011-2523) that opens a shell on port 6200 when a smiley is sent in the USER parameter.
 accord96/cve-2024-38077-poc
CVE-2024-38077-POC
 kn32/cve-2024-46483
Pre-Authentication Heap Overflow in Xlight SFTP server <= 3.9.4.2
 thanawee321/cve-2024-38063
Vulnerability CVE-2024-38063