
PHP2shell
 0xgh057r3c0n/php2shell
One-click exploit PoC for CVE-2026-109618 and CVE-2026-109619 against vulnerable PHP + Apache mod_php (prefork) targets.
binary-exploitationexploitationpayload-development+4
0xgh057r3c0n/php2shellOne-click exploit PoC for CVE-2026-109618 and CVE-2026-109619 against vulnerable PHP + Apache mod_php (prefork) targets.
 lion9453/cve-2026-96889-nextjs-rce
Lab PoC for CVE-2026-96889: Next.js Image Optimization SVG typed as AVIF reaches librsvg UAF (RUSTSEC-2026-0305). Unauthenticated RCE on glibc Linux.
 sm1ee/cve-2026-91737
Proof-of-concept for CVE-2026-91737, a PDFium use-after-free in Chrome's PDF renderer enabling ASLR bypass and ARM64 payload execution inside the…
 mrdark-ops/cve-2026-94545-
Python PoC for CVE-2026-94545: exploits unescaped SVG input in Next.js next/og to trigger libxml2 corruption and a ROP chain for unauthenticated RCE.
 hypnguyen1209/log4j2-rce
Pre-auth RCE via FilteredObjectInputStream MarshalledObject bypass in Apache Log4j 2
 r2qa/cve-2026-17544
Exploit for CVE-2026-17544: PHP bcmath OOB write converted into memory-only RCE, bypassing disable_functions and open_basedir with a runtime…
 sam00/poc-cve-2026-0300-exploit
Palo Alto - CVE-2026-0300 exploit
 debajyoti0-0/cve-2026-27654-poc
Proof-of-Concept and technical analysis for CVE-2026-27654, a heap-based buffer overflow vulnerability in the NGINX HTTP WebDAV module, including…
 depthfirstdisclosures/nginx-rift
NGINX RCE exploits
 alexandergumeniuk/cve-2025-32434
Proof-of-concept exploit for CVE-2025-32434, a critical RCE in PyTorch's torch.load() that bypasses weights_only=True via memory-mapped file writing.
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
 eliangonzi00/cve-2025-2783
Full-chain RCE exploit for CVE-2025-2783, a Chromium Ipcz sandbox escape vulnerability. Implements thread hijacking, V8 hooks, and shellcode…
 adamshaikhma/cve-2026-11645
Exploit for CVE-2026-11645, a V8 out-of-bounds read/write in Google Chrome allowing remote code execution via crafted HTML pages.
 reggyraider/cve-2023-21716
CVE-2023-21716 - Microsoft Word RTF fonttbl Heap Corruption RCE exploit with reverse shell payload
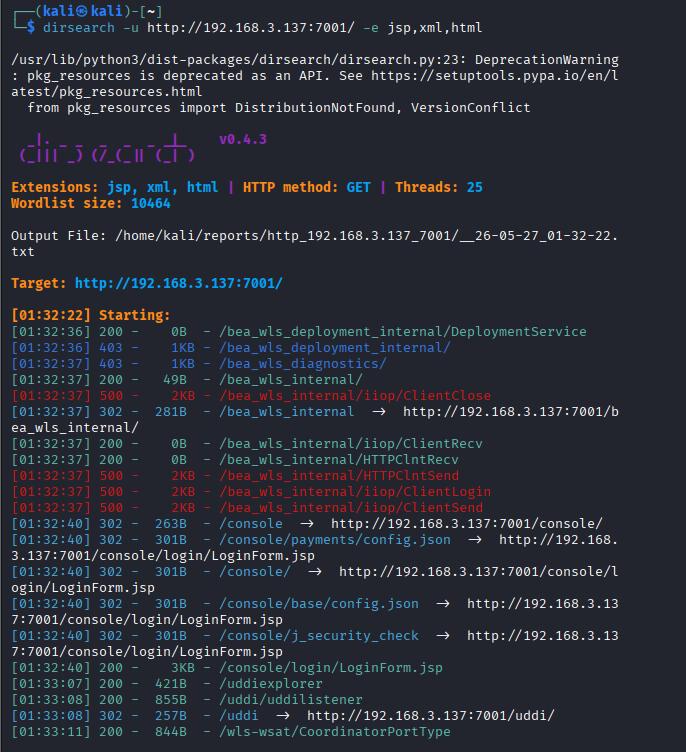 dungsocool/cve-2017-10271
Step-by-step lab guide for exploiting CVE-2017-10271 (WebLogic XMLDecoder deserialization RCE) with manual payload construction, blind RCE bypass,…
 n1et/cve-2026-46529
Evince/xreader/Atril RCE exploit to CVE-2026-46529
 webdev75950-ux/nginx-rce-cve-2026-42945
Proof-of-concept exploit for CVE-2026-42945, a critical heap buffer overflow in NGINX rewrite module enabling remote code execution via crafted URI…
 p3nt3st3r-star/cve-2026-42945-poc
Proof-of-concept exploit for CVE-2026-42945, a critical heap buffer overflow in NGINX's rewrite module enabling unauthenticated remote code…