
CVE-2024-4947-PoC
 l1m3syc/cve-2024-4947-poc
Educational proof-of-concept for CVE-2024-4947, a V8 Maglev type confusion, demonstrating a full chain from trigger to arbitrary code execution on a…
binary-exploitationeducationexploitation+3
l1m3syc/cve-2024-4947-pocEducational proof-of-concept for CVE-2024-4947, a V8 Maglev type confusion, demonstrating a full chain from trigger to arbitrary code execution on a…
 theopaid/cve-2026-66729-out-of-bounds-read-in-facil.io-mime-parser-leads-to-server-crash
Security Advisory: Out-of-Bounds Read in facil.io MIME Parser leads to Server crash
 hycqaq/logitech-g-cloud-ghostlock-cve-2026-43499
罗技云掌机 · GhostLock CVE-2026-43499 root 尝试
 ronf98/cve-2023-38831-poc
CVE-2023-38831 is a Zero-day WinRAR vulnerability that lets attackers disguise malicious files in archives, tricking users into executing harmful…
 shreyas-penkar/cve-2025-39965
Proof-of-concept exploit for CVE-2025-39965, a Linux XFRM subsystem vulnerability, demonstrating exploitation in an isolated emulator environment for…
 shreyas-penkar/cve-2024-38399
PoC for CVE-2024-38399
 chinmay1743/ptrace-vuln
To check for vulnerability CVE-2019-13272
 crackercat/cve-2024-44083
Makes IDA (all versions) to crash upon opening it.
 lucaspdiniz/cve-2021-4034
Local Privilege Escalation (LPE) vulnerability in Polkit - Pwnkit
 d0rb/cve-2023-49606
Critical use-after-free vulnerability discovered in Tinyproxy
 d0rb/logofail-poc
This is a hypothetical demonstration of the process involved in exploiting LogoFail, it theoretically includes the necessary steps.
 d0rb/cve-2023-42931
The exploit targets a critical privilege escalation vulnerability in macOS versions Monterey, Ventura, and Sonoma.
 d0rb/cve-2023-36874
This repository contains a proof-of-concept exploit written in C++ that demonstrates the exploitation of a vulnerability affecting the Windows Error…
 kswzzl/cve-2016-3861
my extended take on Mark Brand's CVE 2016-3861 libutils bug
 ecu-10525611-xander/cve-2022-37706
All Credit to MaherAzzouzi (https://github.com/MaherAzzouzi/CVE-2022-37706-LPE-exploit). This is a copy of the exploit for CTFs
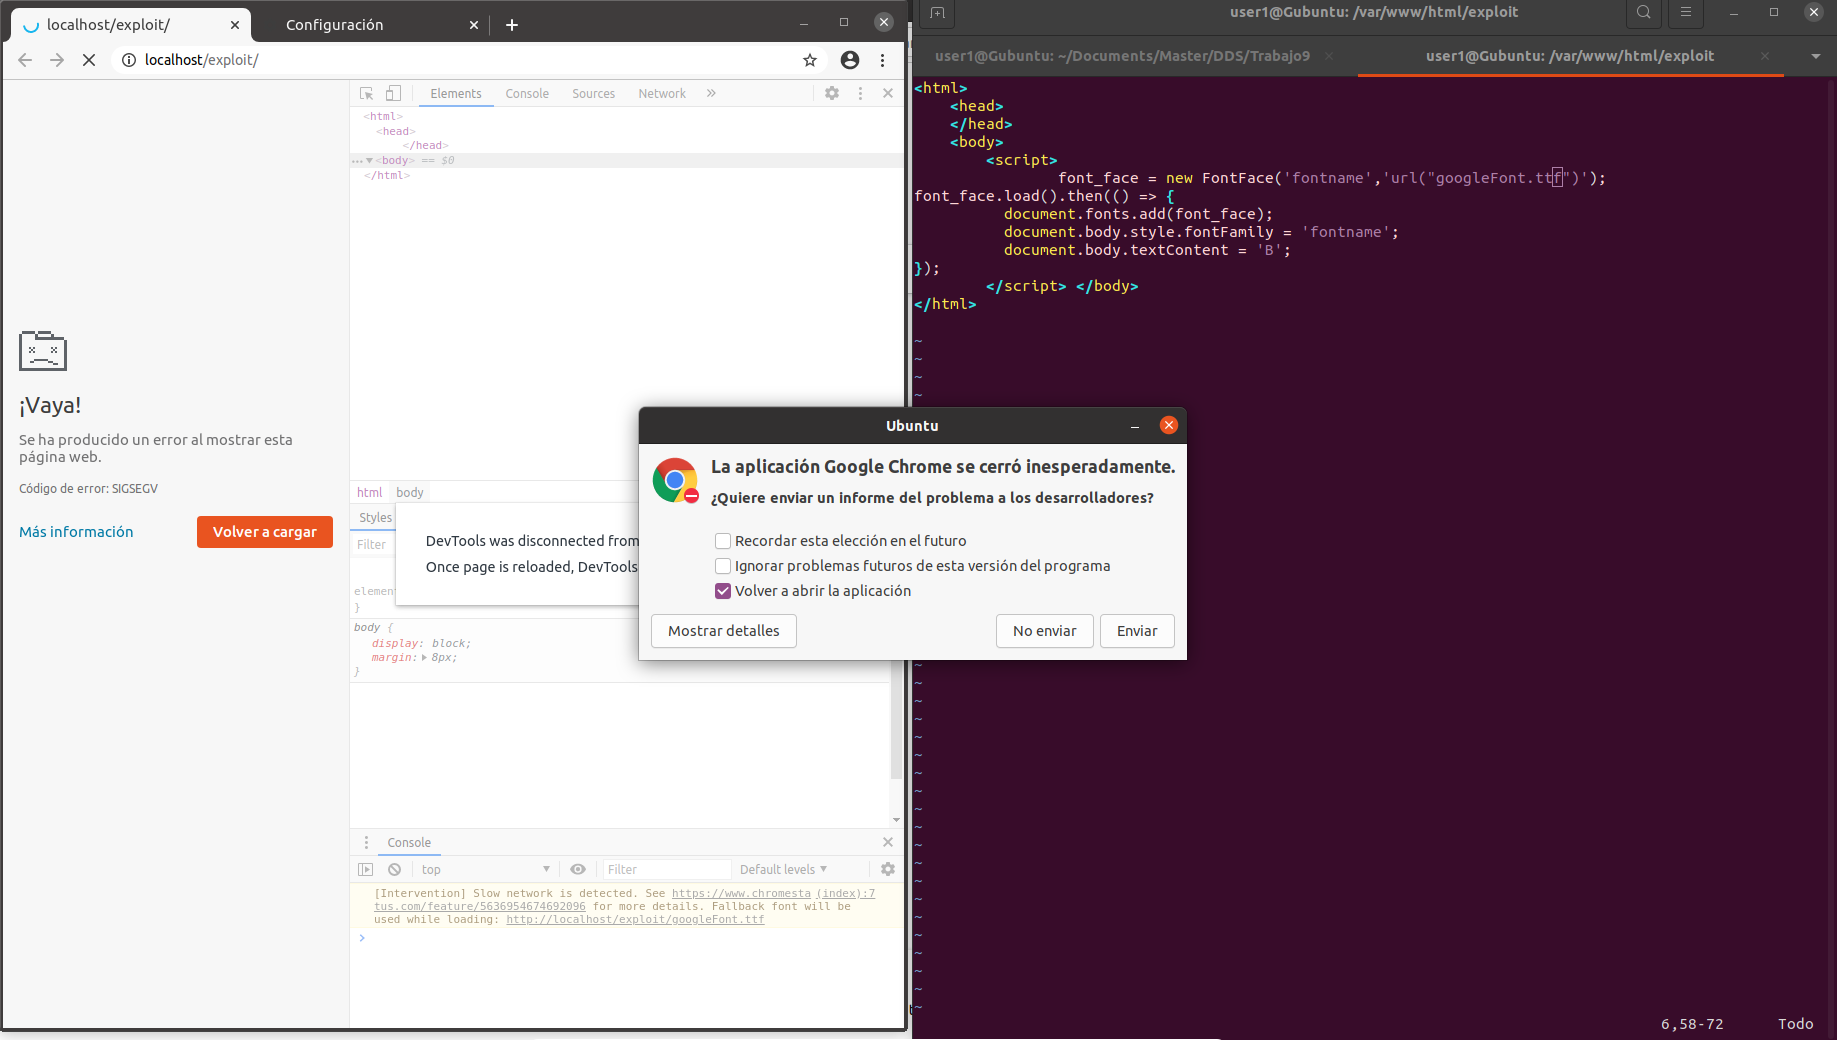 marmeus/cve-2020-15999
Todos los materiales necesarios para la PoC en Chrome y ftview