

ImHex
 werwolv/imhex
🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
ai-assisted-reversingbinary-analysisbinary-exploitation+10
55.0k6h 55m ago
werwolv/imhex🔍 A Hex Editor for Reverse Engineers, Programmers and people who value their retinas when working at 3 AM.
 hackerschoice/team-teso
Historical archive of exploit code and tools from TESO, including remote exploits, DDoS agents, and development utilities for educational security…
 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 264312431/picohaxx
A kernel exploit for Pico 4 devices based on cve-2023-33107.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 veridiff/veridiff
Dynamic branch-divergence finder for native code -- traces two Frida executions and finds the exact instruction where they diverge.
 ntfargo/relapse-exploit
PS5 exploit chain for firmware 7.00-13.60 combining a WebKit JSC info leak and typedarray corruption with an aio_multi_wait UAF race for kernel…
 wuyou6956-glitch/cve-2026-1668-poc
Proof-of-concept exploit for CVE-2026-1668 in TP-Link switch firmware, delivering a MIPS payload that yields a root shell on vulnerable devices.
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 g4sp4rcs/cve-2019-11707-from-an-ionmonkey-type-confusion-to-system-
Windows proof-of-concept exploit chain for CVE-2019-11707, a Firefox IonMonkey type confusion, combining browser RCE with sandbox escape to achieve…
 fortbridge-uk/libheif-grid-nextjs-rce
Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain
 k4ntux/cowslip
xfs kernel LPE (CVE-2026-64600), disclosed by Qualys on 22 July 2026
 mfthomps/labtainers
Labtainers: A Docker-based cyber lab framework
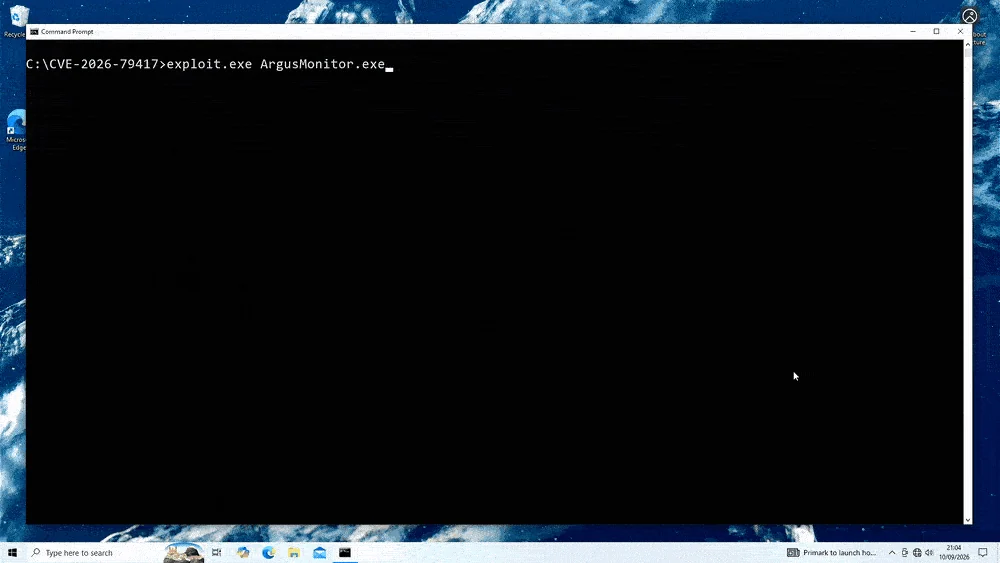 connorjaydunn/cve-2026-79417
Proof-of-concept exploit for CVE-2026-79417, a local denial-of-service vulnerability in Argus Monitor <= 7.4.02, triggered via a signed binary path.