

LIEF
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
ai-assisted-reversingandroid-securitybinary-analysis+12
5.6k
lief-project/liefCross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
 aniketlab/poco-m7-plus-jailbreak
Temporary Root Research on Poco M7 Plus (SM6375) via Qualcomm GBL Exploit (CVE-2026-24088) + GhostLock Kernel Analysis (CVE-2026-43499)
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 sgswzglwlx/vivo-root-build
Builds a root exploit for vivo/iQOO devices targeting CVE-2026-43499, leveraging kernel techniques like KASLR bypass and CFI manipulation to achieve…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 slapah/ghostlock-h8q
GhostLock CVE-2026-43499 port for Galaxy Z Fold 8 (h8q)
 linux-tools/vivo_iqoo_neo_9_root_research_on_cve-2025-21479
 diyiqiuye/cve-2025-21479-fx5p
Temporary root for OPPO Find X5 Pro (PFEM00) via CVE-2025-21479 + KernelSU LKM late-load (cloud-buildable)
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
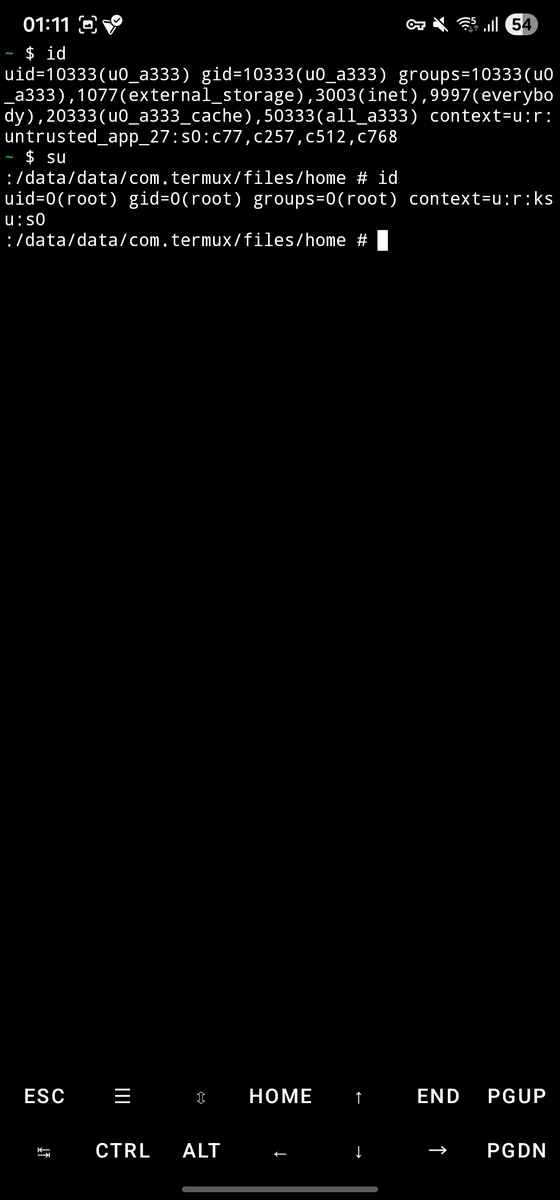 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
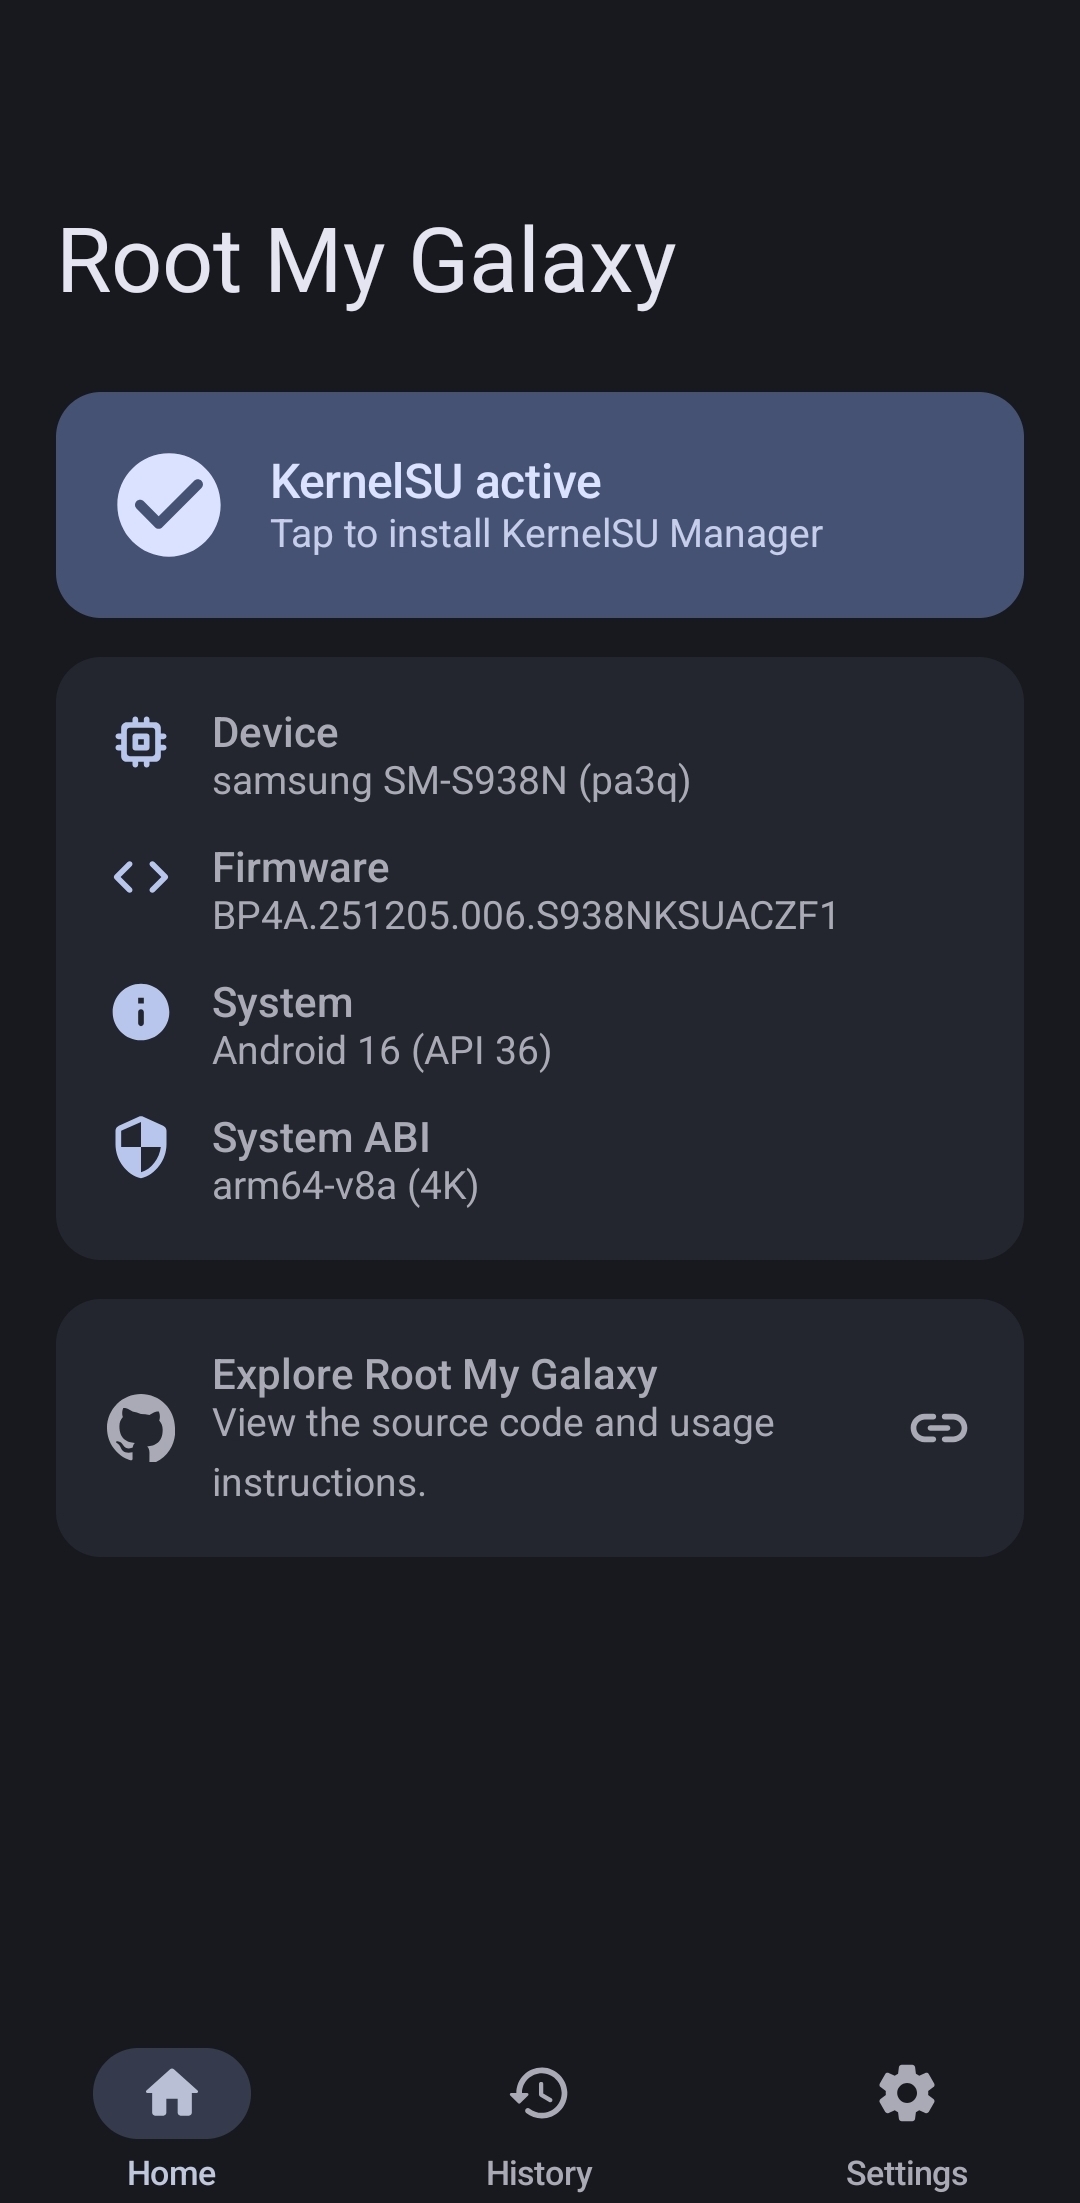 witaqua-tools/root-my-device
KSU installer for supported firmware with CVE-2026-43499
 become-illusory/cve-2026-64560-a16
CVE-2026-64560 toolkit: Go single-binary toolchain + realme RMX5010 (A16, SM8750) target port