
kasld
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
binary-exploitationctfexploitation+3
5536h 51m ago
bcoles/kasldKASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
 rizinorg/rizin
UNIX-like reverse engineering framework and command-line toolset.
 lief-project/lief
Cross-platform library to parse, modify, and abstract ELF, PE, and MachO executable formats. Supports C++, Python, and Rust APIs with disassembler,…
 404godd/cve-2026-20841-poc
🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
 capstone-engine/capstone
Multi-architecture disassembly framework providing a lightweight, thread-safe API for binary analysis, reverse engineering, and malware research…
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
 linux-tools/vivo_iqoo_neo_9_root_research_on_cve-2025-21479
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 lutfifakee-project/cve-2026-31431
CVE-2026-31431 - Linux Kernel Page Cache Vulnerability
 x64dbg/x64dbg
An open-source user mode debugger for Windows. Optimized for reverse engineering and malware analysis.
 a23bc/op13-cve-2026-64560
Device-specific Android kernel exploit for CVE-2026-64560 on OnePlus 13 builds, providing temporary root via ADB shell with verified payloads and…
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
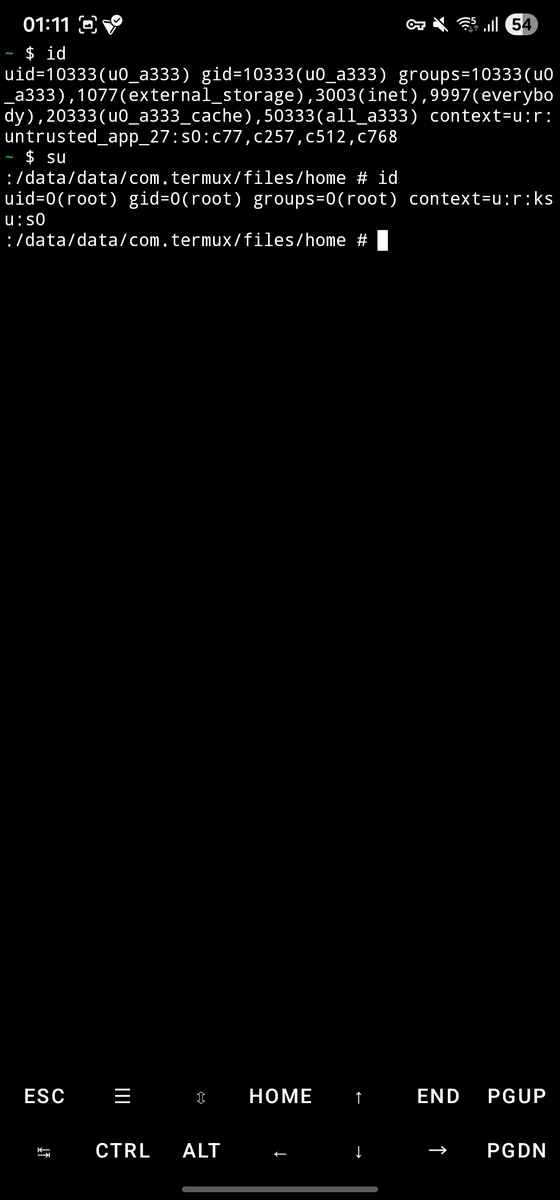 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 qingle009/opace6-cve-2026-64560
OnePlus Ace 6 temporary root tool (CVE-2026-64560) - device-verified port with corrected bootidParent address
 bmax121/kernelpatch
Patching and hooking the Linux kernel with only a stripped Linux kernel image.
 petermalone/cve-2026-43682
Proof-of-concept disk-image generator that crafts a malformed HFS+ attributes B-tree key to trigger the CVE-2026-43682 kernel heap overflow on macOS.