

cve-2018-8611
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
binary-exploitationexploitationpost-exploitation+1
1
ahm3dgg/cve-2018-8611Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
 karkas66/lacuna-rs
Rust crate for ghost-frame call-stack spoofing, runtime indirect syscalls, and APC injection on Windows x64. Provides SSN resolution, JIT stub…
 n0isegat3/regpwnbrc4bof
Brute Ratel C4 BOF that exploits a registry symlink race condition in Windows Accessibility ATConfig to escalate privileges to SYSTEM by writing…
 xm0kht4r/cve-2025-7771
A simple PoC demonstrating the vulnerability in the ThrottleStop.sys driver, showcasing arbitrary physical memory read and write capabilities, as…
 d4m0n/cve-2025-50168-pwn2own-berlin-2025
CVE-2025-50168 Exploit PoC — Pwn2Own Berlin 2025 - LPE(Windows 11) winning bug.
 talsim/printdemon2system
PrintDemon (CVE-2020-1048) Privilege Escalation
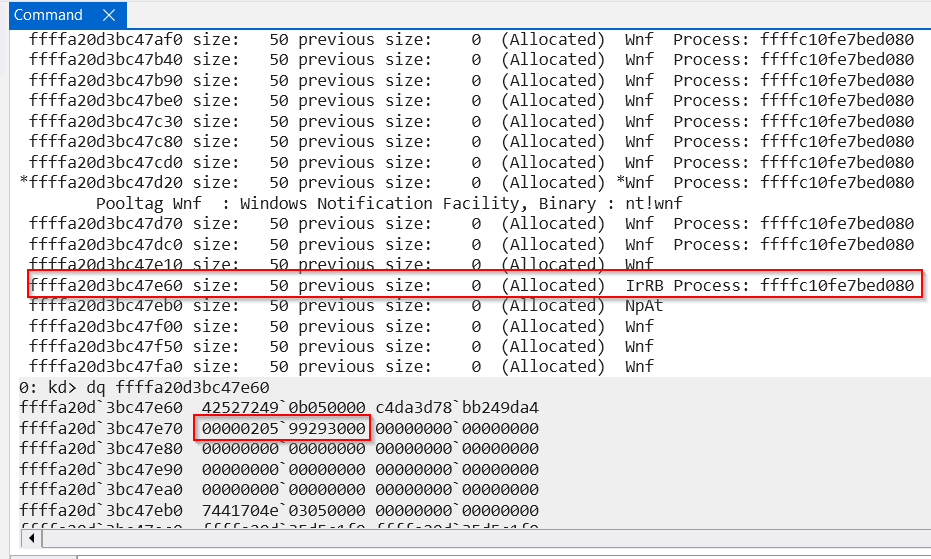 mrale98/cve-2025-21333-poc
POC exploit for CVE-2025-21333 heap-based buffer overflow. It leverages WNF state data and I/O ring IOP_MC_BUFFER_ENTRY
 zeromemoryex/cve-2025-26125
( 0day ) Local Privilege Escalation in IObit Malware Fighter
 ps5dev/ps5-umtx-jailbreak
A webkit-based kernel exploit and jailbreak for PS5
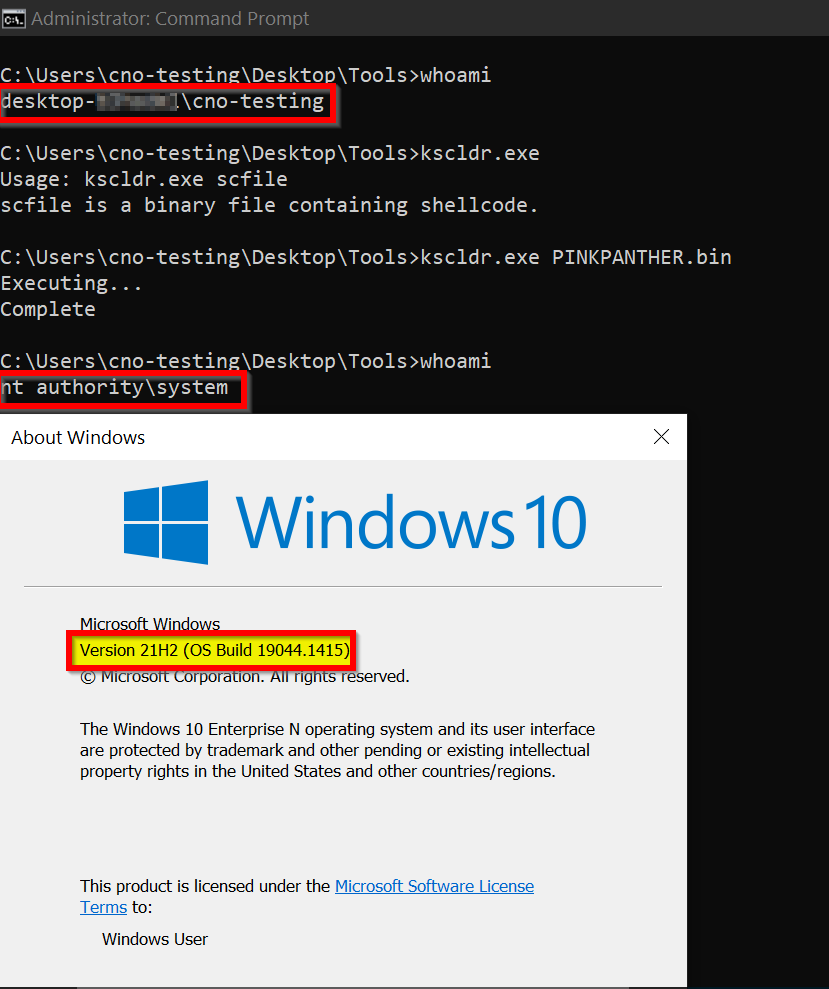 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 wh04m1001/cve-2023-29343
Proof-of-concept exploit for arbitrary file write in Sysmon 14.14, abusing Windows service tracing to achieve privilege escalation.
 heegong/cve-2022-24924
An improper access control in LiveWallpaperService prior to versions 3.0.9.0 allows to create a specific named system directory without a proper…
 irsl/cve-2020-0728
Proof-of-concept exploit for CVE-2020-0728 demonstrating local privilege escalation via Windows TrustedInstaller COM service abuse to bypass file…
 irsl/php-bypass-disable-functions
Demo project how to bypass the disable_functions security control of PHP on Linux
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )