
CVE-2026-68121
 0xblackash/cve-2026-68121
Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
binary-exploitationeducationexploitation+6
0xblackash/cve-2026-68121Research repository for CVE-2026-68121, a Linux kernel PPPoE use-after-free in pppoe_sendmsg() enabling local privilege escalation, with PoC,…
 0xblackash/cve-2026-81000
Research repository for CVE-2026-81000 (TUNderflow), a Linux kernel TUN/TAP receive headroom integer underflow enabling local privilege escalation,…
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 hackspeak/cve-2026-82592
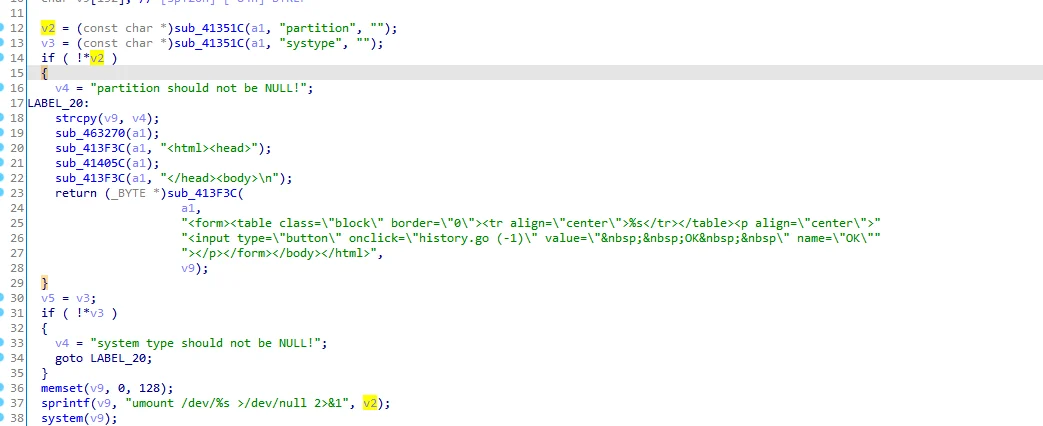
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 open-flaw/cve-2026-2005
PostgreSQL pgcrypto heap buffer overflow PoC demonstrating CVE-2026-2005: low-privileged RCE and privilege escalation to superuser via crafted…
 george0papasotiriou/cve-2026-23002-5g-nas-message-buffer-overflow-in-gnodeb
Simulated 5G gNodeB NAS parser with stack buffer overflow PoC for CVE-2026-23002; a crafted NAS message triggers remote code execution.
 george0papasotiriou/cve-2026-2222-mqtt-broker-connect-packet-heap-overflow
Demonstrates CVE-2026-2222 heap overflow in MQTT CONNECT packet handling with a simulated vulnerable broker and proof-of-concept exploit code for…
 razureink/cve-2024-49113-ldap_nightmare_reproduction
Reproduction of cve-2024-49113-ldap_nightmare_reproduction
 dinosn/cve-2026-25243
CVE-2026-25243 — Redis RESTORE zipmap double-free → remote code execution (ASLR on).
 34zy/cve-2025-14177
PHP getimagesize() CVE-2025-14177 - Heap Memory Leak Exploit Generator Fully functional exploit chain in Python
 erikdervishi03/cve-2026-31024
Proof of Concept (PoC) for a stack-based buffer overflow in Steghide 0.5.1. Demonstrates how long file paths trigger a crash (DoS) and leak sensitive…
 xd20111/cve-2026-43284
Deterministic Linux kernel local privilege escalation exploit chaining two page-cache write primitives (xfrm/ESP and RxRPC) for reliable root access…
 masjadaan/cve-2025-29338
Technical advisory and proof-of-concept for a stack-based buffer overflow (CWE-121) in the NXP moal.ko Wi-Fi kernel driver, enabling local kernel…
 mlgzackfly/cve-2026-6643
ASUSTOR ADM 5.1.2 vpnupload.cgi Format String & Stack Buffer Overflow RCE (CVE-2026-6643)
 rippsec/cve-2025-27591-meta-below-lpe
CVE-2025-27591 – Meta below symlink following local privilege escalation (HackTheBox CTF)
 cybermads/cve-2020-0796
Python exploit for CVE-2020-0796 (SMBGhost) targeting integer overflow in SMBv3 compressed segment size field for remote code execution on Windows.
 eerykitty/cve-2020-0796-poc
PoC for triggering buffer overflow via CVE-2020-0796
 rami08448/cve-2021-3656-demo
Demonstration of CVE-2021-3656, a KVM nested virtualization vulnerability allowing L2 guest to bypass VMLOAD/VMSAVE intercepts and read/write host…