
copyfail-rs
 liverwortenuresis371/copyfail-rs
Exploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
authenticationbinary-exploitationexploitation+7
liverwortenuresis371/copyfail-rsExploit and detect CVE-2026-31431 vulnerabilities using a static binary that monitors system integrity and bypasses PAM authentication.
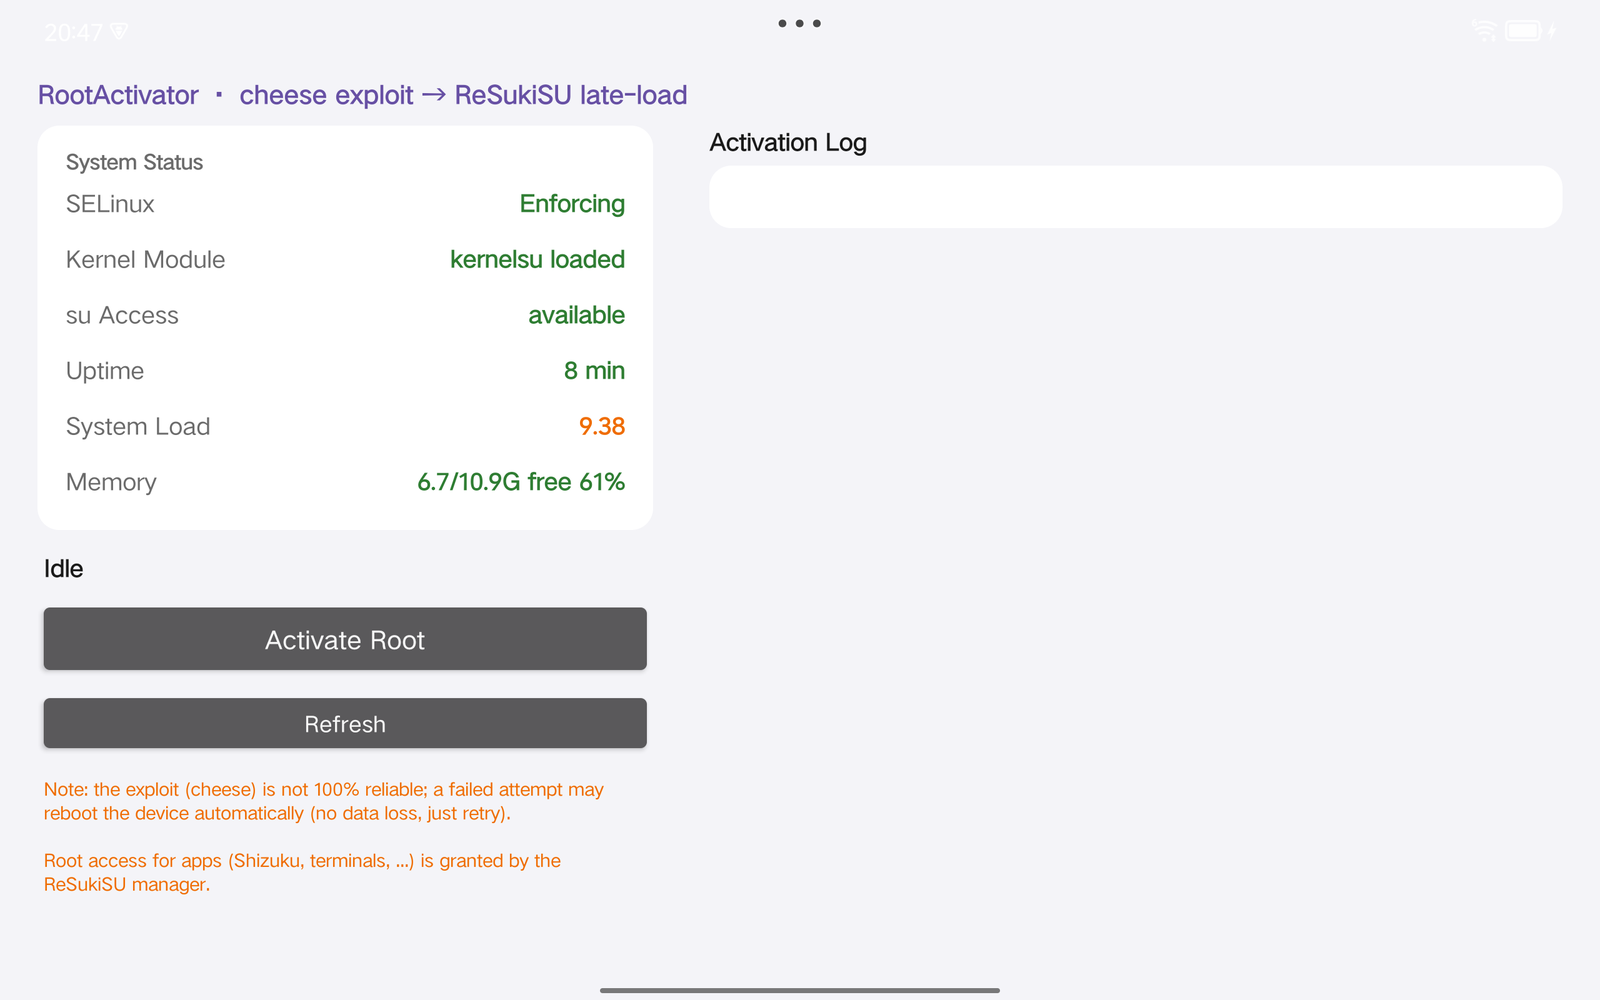 xjoker/lenovo_y700_tb320fc_on_cve-2025-21479
In-memory kernel privilege escalation for Lenovo Legion Y700 2023 (TB320FC) exploiting CVE-2025-21479, a Qualcomm Adreno GPU SMMU flaw, with ReSukiSU…
 canyie/transitionplayer
CVE-2026-0091, play with an issue in android window management to perform arbitrary code execution in Launcher process from adb
 miapatsune/cve-2026-43499
Kernel exploit for Redmi Pad Pro (dizi) / POCO Pad 5G with browser-based upload and execution interface, admin panel for log management, and…
 hunt-benito/mediatek-wlan-heap-overflow-cve-2026-20452-filogic-router-rce
Proof-of-concept exploit for CVE-2026-20452, a heap-based buffer overflow in MediaTek WLAN AP drivers. Uses scapy to send crafted Wi-Fi management…
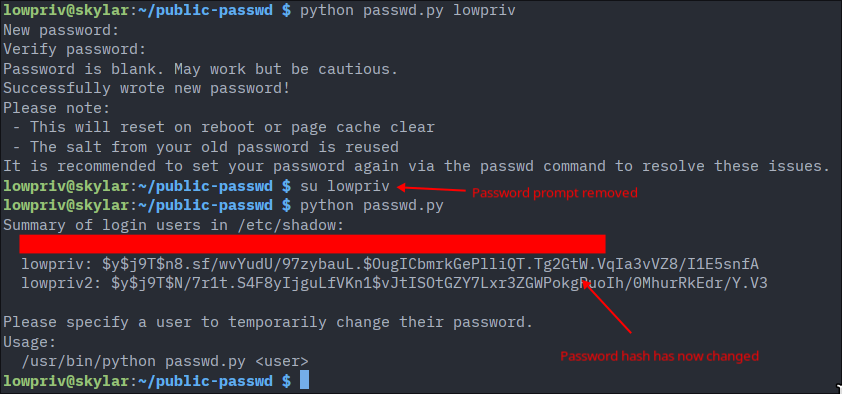 st4rburn/public-passwd
Use CVE-2026-46333 and CVE-2026-31431 to change any user's password.
 simoesctt/cve-2024-0070-nvidia-gpu-driver--resonance-vulnerability
NVIDIA's GPU drivers have a temporal coherence flaw in their memory management. At 587 kHz resonance, the driver's memory pages experience α-decay…
 lzty/cve-2025-7771
Rust-based PoC exploit for CVE-2025-7771 providing arbitrary read/write primitives via a vulnerable driver, with virtual-to-physical address…
 demining/scalar-venom-attack
Exploit and research repository analyzing CVE-2025-60013, a critical HSM initialization vulnerability enabling Bitcoin private key recovery via…
 amrhuss/throttlestop-exploit-rw
Arbitrary physical memory read/write exploitation using ThrottleStop.sys (CVE-2025-7771) with superfetch address translation - Windows kernel…
 wowfunhappy/fix-apple-mail-cve-2020-9922
Patches the zero-click Apple Mail vulnerability (CVE-2020-9922) on macOS, preventing remote code execution without user interaction.
 amalpvatayam67/day08-cisco-fmc-sim
This is a minimal, educational simulation that demonstrates the _impact_ class of a management-plane parsing RCE (inspired by CVE-2025-20265). It…
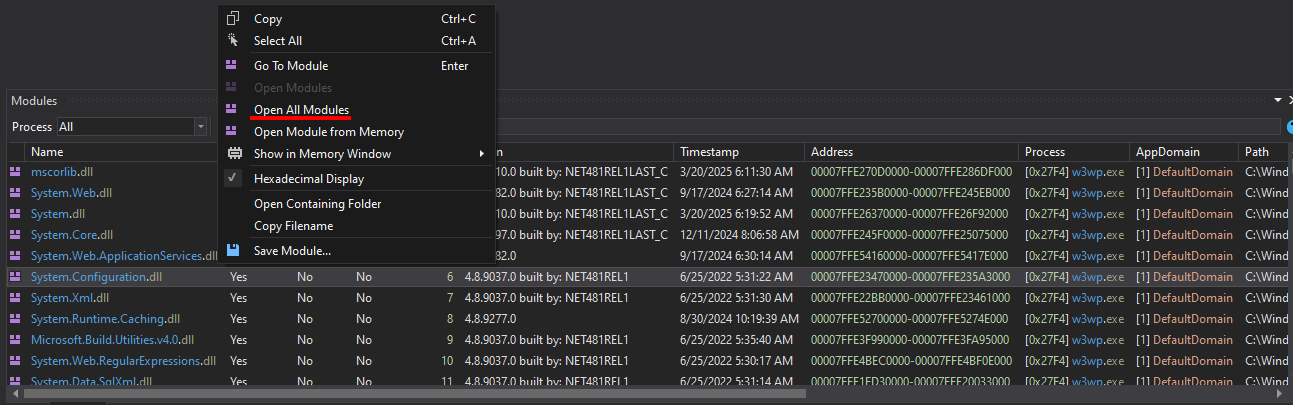 tranphuc2005/cve-2017-9822
Detailed analysis and proof-of-concept exploit for CVE-2017-9822, an XXE/insecure deserialization vulnerability in DotNetNuke CMS leading to remote…
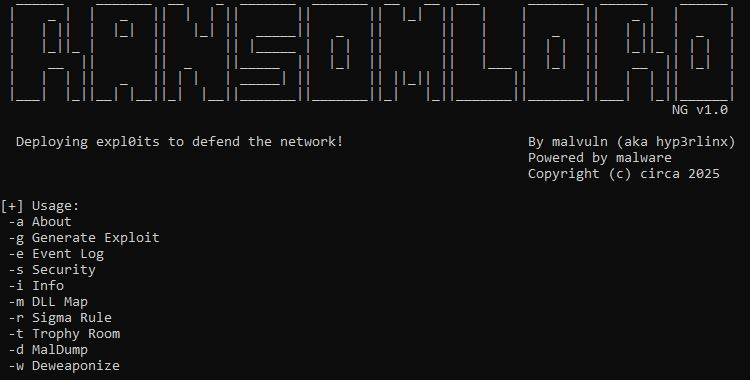 malvuln/ransomlord
RansomLord is a proof-of-concept Anti-Ransomware exploitation tool that automates the creation of PE files, used to compromise ransomware…
 encrypter15/cve-2025-30400
Educational Python model demonstrating a Use-After-Free (UAF) privilege escalation vulnerability inspired by CVE-2025-30400 in Windows DWM. Simulates…
 cwjchoi01/cve-2024-57394
Proof-of-concept exploit for CVE-2024-57394: low-privilege file restoration to System32 enabling DLL hijacking and local privilege escalation to…
 wolffcorentin/cve-2019-1663-binary-analysis
Binary analysis and exploitation of CVE-2019-1663, a buffer overflow in Cisco router web management, including root cause, exploit steps, and ROP…
 x-projetion/cve-2024-26304-rce-exploit
CVE-2024-26304 is a critical vulnerability (CVSS score of 9.8) affecting ArubaOS