
cve-2026-42945
 franklinf25/cve-2026-42945
Analyzes CVE-2026-42945, an NGINX rewrite heap overrun, providing a differential detector, deterministic DoS PoC, and a credited RCE port with…
binary-exploitationeducationexploitation+3
franklinf25/cve-2026-42945Analyzes CVE-2026-42945, an NGINX rewrite heap overrun, providing a differential detector, deterministic DoS PoC, and a credited RCE port with…
 franklinf25/cve-2026-31431
Analyzes CVE-2026-31431, a Linux kernel AF_ALG AEAD vulnerability, providing a safe detector, in-lab LPE exploit, and QEMU-based A/B kernel lab for…
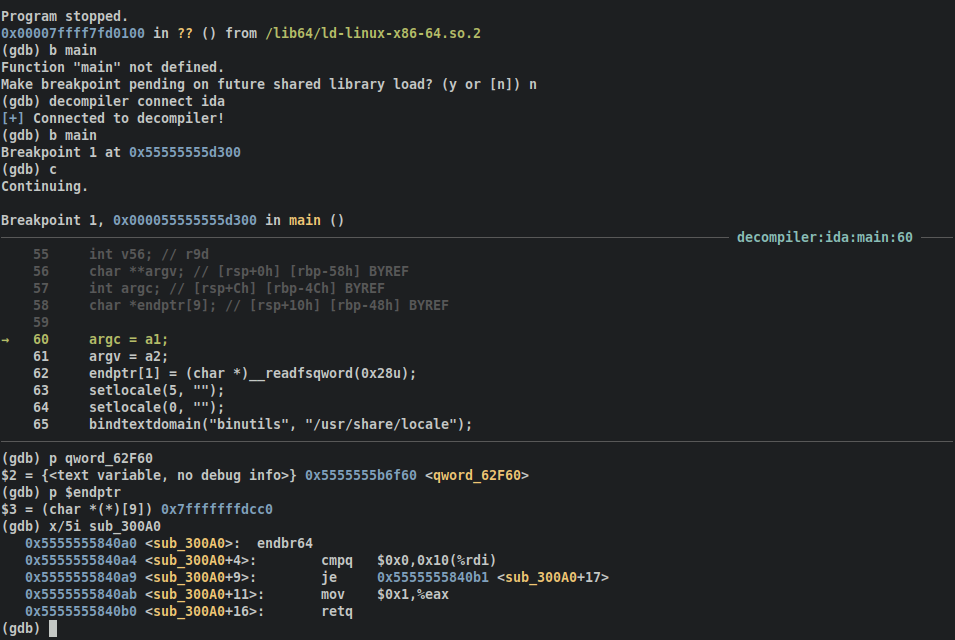 mahaloz/decomp2dbg
A plugin to introduce interactive symbols into your debugger from your decompiler
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 xteardx/diaphora-mcp
MCP server for automated binary diffing.
 bcoles/kasld
KASLD derandomizes the Linux kernel's virtual and physical memory layout from a local process, using whatever its vantage — privilege, configuration,…
 hackerschoice/team-teso
Historical archive of exploit code and tools from TESO, including remote exploits, DDoS agents, and development utilities for educational security…
 sunblaze-ucb/exploitgym
ExploitGym is a large-scale, realistic benchmark built from real-world vulnerabilities designed to evaluate AI agents' ability to develop exploits.
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
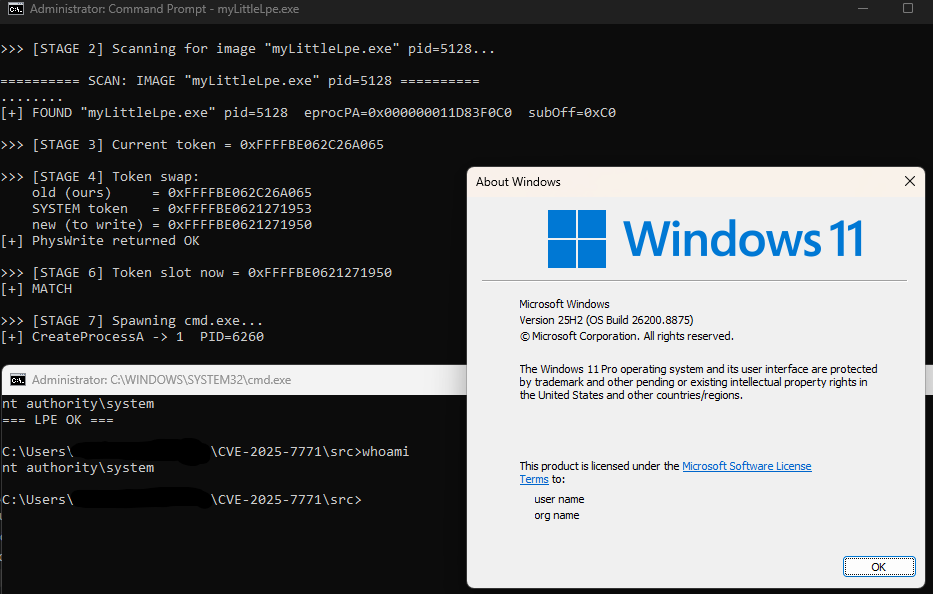 yulisec/cve-2025-7771
Full exploit chain for CVE-2025-7771 in ThrottleStop.sys, abusing unvalidated physical memory R/W IOCTLs to escalate from administrator to SYSTEM on…
 elttam/publications
Offensive security research hub aggregating original vulnerability advisories, CVE proof-of-concept exploits, conference talks, and internal tooling…
 minime794/dirtyfrag
Linux kernel exploit chain (CVE-2026-43284 and CVE-2026-43500) that achieves root via xfrm-ESP and RxRPC page-cache write vulnerabilities.
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 0xcyberstan/cve-2026-59346-poc
PoC for CVE-2026-59346 - 32-bit integer overflow in VMware's VMXNET3 TSO segmentation path, guest-to-host crash.
 edwardzpeng/presentations
Slides and conference talks from security research covering Windows, virtualization, web, and blockchain exploit techniques, presented at Black Hat,…
 sneakynachos/cve-2026-87491-and-cve-2026-85046-the-bagel-fell-off-the-counter
Chrome 152 V8 exploit chaining CVE-2026-85046 and CVE-2026-87491 to corrupt the heap, forge Wasm metadata, and execute native code from the renderer.
 dryxio/auto-re-agent
Reconstruct and validate C/C++ code from compiled programs with AI.