
cve-writeups-and-pocs
 suruurism/cve-writeups-and-pocs
CVE-2026-80724 PoC + full write-up — Linux kernel ptp/vmclock read-only mapping becomes writable (VM_MAYWRITE). Discovered, reported & fixed by…
binary-exploitationeducationexploitation+2
1
suruurism/cve-writeups-and-pocsCVE-2026-80724 PoC + full write-up — Linux kernel ptp/vmclock read-only mapping becomes writable (VM_MAYWRITE). Discovered, reported & fixed by…
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 john-popovici/cve-2026-31431-copyfail-linux-privesc
A demo and explanation of CVE-2026-31431
 karollooool/cve-2026-83991-writeup-and-poc
Proof-of-concept demonstrating a Windows Cloud Files access-check bypass (CVE-2026-83991) that converts a read-only file into a cloud placeholder via…
 sandraschi/copy-fail-mcp
CVE-2026-31431 Copy Fail — Linux kernel LPE tester via MCP
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 rizlmaulanaa/cve-2026-23479-redis-uaf-proof-of-concept
Proof of concept with GDB‑assisted exploitation (educational / lab use only)
 creeeeger/cve-2024-56426
A PoC of the CVE-2024-56426 vulnerability.
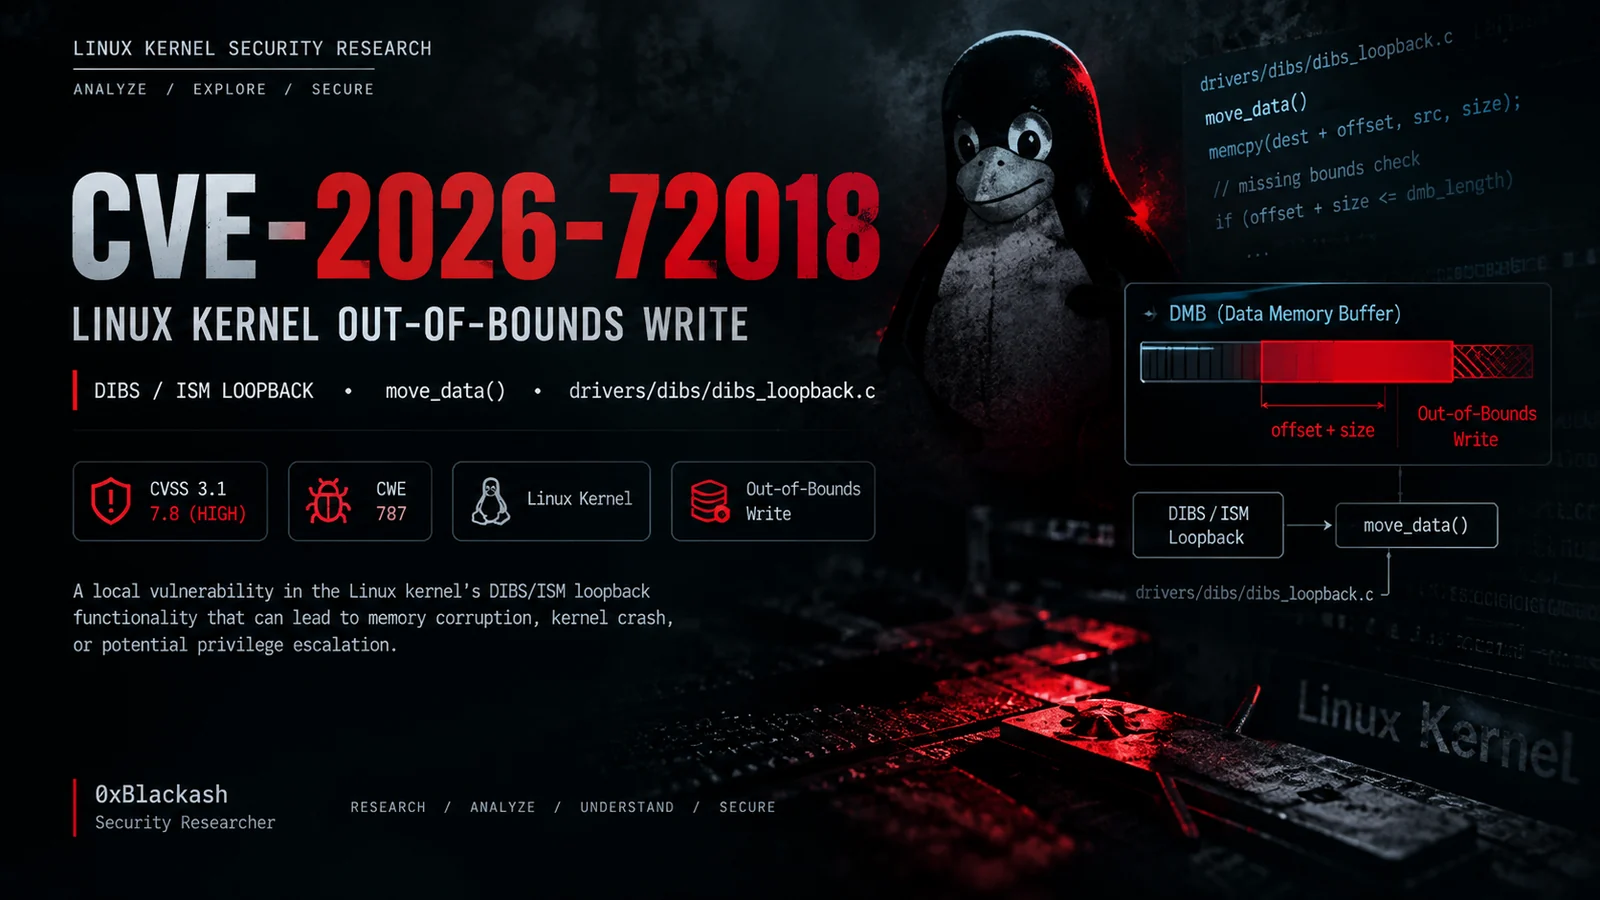 0xblackash/cve-2026-72018
Technical analysis of CVE-2026-72018, a Linux kernel out-of-bounds write in DIBS/ISM loopback, covering root cause, affected versions, detection, and…
 0xblackash/cve-2026-74469
Research repository for CVE-2026-74469 (DiagSpill), a Linux kernel SCTP peer transport counter overflow causing an out-of-bounds write, with PoC,…
 0xblackash/cve-2026-80844
Research repository for CVE-2026-80844 (DirtyAH6), a Linux kernel IPv6 AH6/XFRM local privilege escalation, with PoC, root-cause and patch analysis.
 petermalone/cve-2026-43682
Proof-of-concept disk-image generator that crafts a malformed HFS+ attributes B-tree key to trigger the CVE-2026-43682 kernel heap overflow on macOS.
 connorjaydunn/cve-2026-79417
Proof-of-concept exploit for CVE-2026-79417, a local denial-of-service vulnerability in Argus Monitor <= 7.4.02, triggered via a signed binary path.
 petermalone/cve-2026-84543
Proof-of-concept and technical disclosure for CVE-2026-84543, a macOS SMB kernel vulnerability that triggers kernel panic via crafted SMB1 responses.
 tihanyin/rex-skill
REx@Skill - Agentic Reverse Engineering eXecution Skill for binary vulnerability discovery
 elttam/publications
Offensive security research hub aggregating original vulnerability advisories, CVE proof-of-concept exploits, conference talks, and internal tooling…
 gitchw/ghostlock-cve-2026-43499
CVE-2026-43499 (GhostLock) — Linux kernel futex PI rt_mutex UAF ARM32 privilege escalation research targeting Huawei Watch 4 Pro (kernel 5.4.210)
 minime794/dirtyfrag
Linux kernel exploit chain (CVE-2026-43284 and CVE-2026-43500) that achieves root via xfrm-ESP and RxRPC page-cache write vulnerabilities.