

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
80.8k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 hackerschoice/team-teso
Historical archive of exploit code and tools from TESO, including remote exploits, DDoS agents, and development utilities for educational security…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
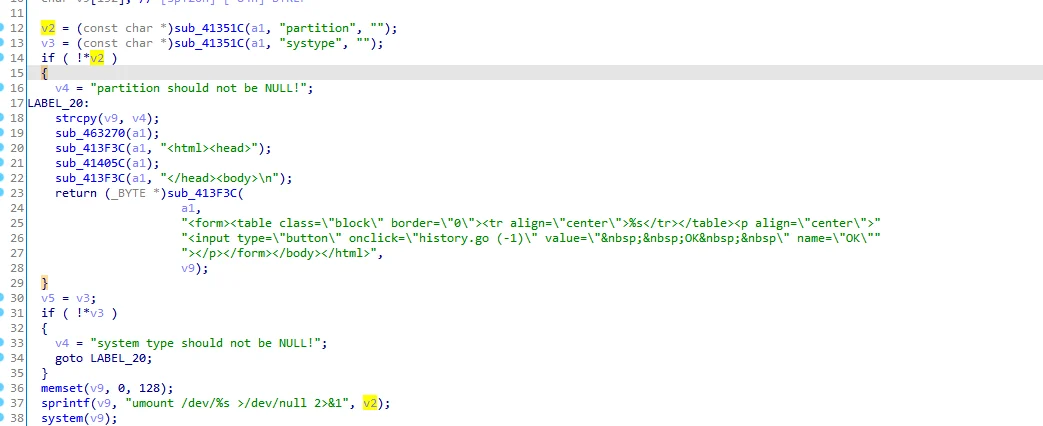 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 hugsy/gef
GEF (GDB Enhanced Features) - a modern experience for GDB with advanced debugging capabilities for exploit devs & reverse engineers on Linux
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 bansalkrish007-arch/cve-2015-1328
Linux Kernel 3.13.0 < 3.19 (Ubuntu 12.04/14.04/14.10/15.04) - 'overlayfs' Local Privilege Escalation
 jm00nj/phantom-evasion-loader
x64 Assembly injection engine using SROP and Zero-Copy Injection to bypass EDR/XDR and kernel monitors. Delivers XOR-encrypted payloads with minimal…
 davidcarliez/cve-2026-58635-poc
PoC for CVE-2026-58635: Windows Narrator Braille Local Privilege Escalation
 s3n4t0r-0x0/rustywater-shellcode-dropper
RustyWater represents the main payload and the backbone of the entire adversarial operation in Static Kitten group attacks.
 kushiro45/shellshock-poc-cve-2014-7169
This contains the Dockerfile for building and reproduing shellshock
 hunt-benito/samsung-bixby-command-execution-cve-2026-21055-improper-component-export
Proof-of-concept exploit for CVE-2026-21055 demonstrating arbitrary command execution via improperly exported Android components in Samsung Bixby.…
 toxy4ny/copy-fail
Copy Fail - CVE-2026-31431 - Hardened C implementation for redteam and authorized penetration testing operations. ⚠️ Legal Notice: This tool is…
 minsmiths/cve-2023-34446
Proof-of-concept exploit for CVE-2023-36664, a Ghostscript command injection vulnerability. Includes Docker lab environment, detailed analysis of…
 tomadimitrie/cve-2026-54424
Exploiting Parsec for Windows to gain SYSTEM privileges