
Zapscape
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
binary-exploitationdefensive-toolsexploitation+2
1
aarif450/zapscapeGuest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 learningdisordercapital35/cve_2025_24257----not-mine
Demonstrate CVE-2025-24257 with a public PoC for IOGPUFamily kernel heap OOB read/write and panic analysis
 sneakynachos/cve-2026-15718-who-put-ptrs-in-my-wasm
PoC exploit chain for CVE-2026-15718: SpiderMonkey wasm baseline compiler array.fill missing-sync -> invalid pointer -> addrOf/fakeobj -> arbitrary…
 sneakynachos/cve-2026-2796-escape-wasm-by-using-wasm
PoC exploit chain for CVE-2026-2796: SpiderMonkey WebAssembly sandbox escape (signature type confusion -> arbitrary R/W -> RCE)
 sneakynachos/cve-2026-2764-but-with-wasm
Proof-of-concept exploit chain for Firefox JIT CVE-2026-2764, chaining JIT miscompilation and use-after-free into arbitrary read/write and WASM…
 jaf0rk/cve-2026-14431
Exploit for CVE-2026-14431 providing V8 sandbox read/write primitives via a crafted JavaScript file, targeting Chromium's V8 engine on Linux x64.
 dexsemon/cve-2026-27495
Proof-of-concept exploit and lab environment for CVE-2026-27495
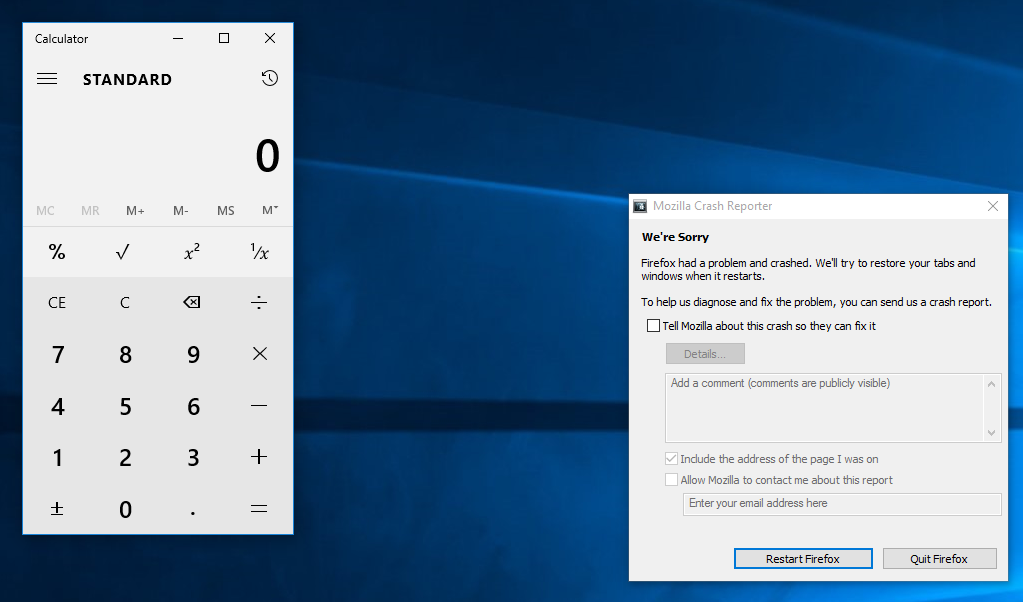 soham23/firefox-rce-nssmil
Educational standalone JavaScript implementation of the public exploit for CVE-2016-9079 (Firefox Use-After-Free), adapted from the original…
 azefzafyoussef/cve-2026-34621
Research PoC demonstrating a prototype pollution and JavaScript injection chain in Adobe Acrobat Reader, enabling privileged JavaScript execution and…
 crihexe/v8-poc-cve-2026-5865
Minimal JavaScript proof-of-concept for V8 engine vulnerability CVE-2026-5865, with scripts to patch and calibrate the exploit for d8.
 borahll/cve-2021-21220
Educational presentation detailing the exploitation of CVE-2021-21220, a V8 JIT type confusion leading to OOB access and RCE via WebAssembly, with…
 ppwwiinn/cve-2026-2763-poc
Proof-of-concept exploit for CVE-2026-2763, a use-after-free in Mozilla's JavaScript engine, demonstrating a constrained 1-bit write primitive…
 simoesctt/ctt-apple-silicon-refraction
webkit_refraction.js (The 33-Layer WebGL Payload) This JavaScript payload uses the \alpha constant to create a high-frequency "Memory Shiver." It…
 moscovium-mc/tor-0day-javascript-exploit
Firefox/Tor Browser 0day exploit analysis (CVE-2024-9680) A UAF in animation timelines leading to RCE. Patched.
 pwntoday/cve-2025-6554
Proof-of-concept exploit for a V8 JavaScript engine vulnerability (CVE-2025-6554) demonstrating a TDZ bypass that leaks 'The Hole' sentinel, enabling…
 ghostn4444/poc-cve-2025-6554
Proof-of-concept exploit for CVE-2025-6554, a V8 JavaScript engine vulnerability allowing unauthorized access to uninitialized 'Hole' values via…
 hacksysteam/cve-2022-28672
Foxit PDF Reader Remote Code Execution Exploit
 satheesh575555/external_v8_aosp10_r33_cve-2021-0396
Repository containing V8 JavaScript engine source code with a specific commit for CVE-2021-0396, likely for vulnerability research and exploitation.