

ghidra
 nationalsecurityagency/ghidra
Ghidra is a software reverse engineering (SRE) framework
ai-assisted-reversingandroid-securitybinary-analysis+17
76.1k
nationalsecurityagency/ghidraGhidra is a software reverse engineering (SRE) framework
 newazbenalam/root-my-galaxy-payloads
Device-specific CVE-2026-43499 root payloads and KernelSU artifacts for Samsung Galaxy models, with firmware profiles, exploit source, and a support…
 genksome/ghost-hoock
GhostLock stripped to one primitive: SELinux off on Galaxy A17 (BZA5) via futex PI UAF (CVE-2026-43499). No root, no cred patch, no rwforge.
 ccp-p/ghostlock-cve-2026-43499-4.19-k40
Android kernel LPE PoC for CVE-2026-43499, an rtmutex use-after-free in 4.19 Qualcomm kernels, adapted for Redmi K40 with LD_PRELOAD root payload.
 linux-tools/vivo_iqoo_neo_9_root_research_on_cve-2025-21479
 radareorg/radare2
UNIX-like reverse engineering framework and command-line toolset
 zhubaohe123/ghostlock-kit
One-click root kit for vivo iQOO Neo9S Pro (MT6989) exploiting CVE-2026-43499 futex PI UAF via MCAST transport, with scripts and analysis docs.
 tracyliving606/regpwn
Exploit Windows local privilege escalation on clients and servers using tested code for CVE-2026-24291 across multiple Windows versions
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 huaguiqi/asus_i005-cve-2026-43499
Android local privilege escalation exploit for CVE-2026-43499 that patches kernel creds and launches embedded KernelSU in late-load mode via…
 skorpion96/unisoc-su
A method for CVE-2025-31710 and to connect to cmd_skt to obtain a root shell on unisoc unpatched models
 woaphone/cve-2021-28664-poc
PoC skeleton for CVE-2021-28664, a Mali kbase GPU driver use-after-free, demonstrating a kernel arbitrary physical memory read/write primitive on…
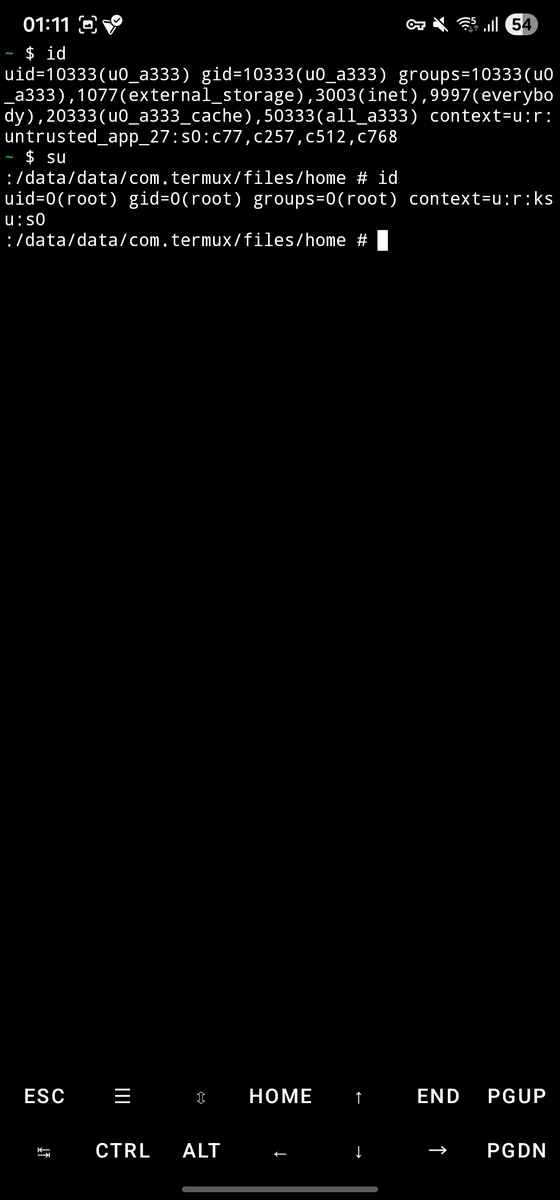 sarabpal-dev/ionstack-s22u
CVE-2026-43499 full exploit chain for Samsung Galaxy S22 Ultra (Android 5.10 kernel)
 artur9010/amazon-mustang-hack
Kernel exploit research achieving temporary root on Amazon Fire 7 (Fire OS 7.3.3.1) via the Mali kbase JIT use-after-free CVE-2022-38181, with a…
 hmascs/ksuroot
One-click Android kernel rooting tool exploiting CVE-2026-43499 to install KernelSU, with official, bundled, and custom .so payload sources.
 zenyxx-xd/rootmyvivo-exploit
GhostLock (CVE-2026-43499) exploit fork for RootMyVivo Neo — iQOO Neo 11 (PD2520, SM8750, 6.6.89). For authorized research on own devices only.
 abdgalaxy36-code/galaxy-a37-root
CVE-2026-43499 exploit payload for Samsung Galaxy A37 (A376BXXS4AZG4, kernel 6.1.138-android14-11)
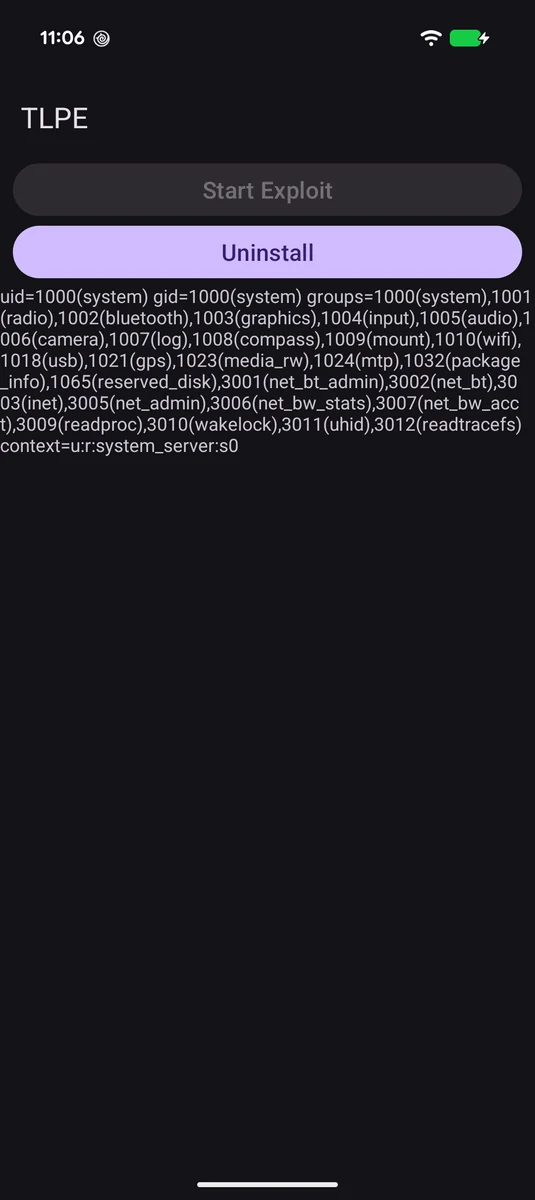 supersonic/tlpe
CVE-2026-49881, a logic issue in the InCallController class in Android 17's Telecom service that allows an unprivileged app to gain arbitrary code…