
CVE-2022-22715
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
binary-exploitationexploitationpapers-research+2
vportal/cve-2022-22715Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 dbgbgtf1/cve-2026-40369-exploit
Exploit for CVE-2026-40369 that leverages kernel address leak and token forging to achieve privilege escalation in a browser sandbox environment.
 threedr3am/learnjavabug
Java安全相关的漏洞和技术demo,原生Java、Fastjson、Jackson、Hessian2、XML反序列化漏洞利用和Spring、Dubbo、Shiro、CAS、Tomcat、RMI、Nexus等框架\中间件\功能的exploits以及Java Security…
 davidcarliez/cve-2026-66804-crossdevice-lpe
Local privilege escalation PoC for Windows CVE-2026-66804 using CrossDevice DLL planting and SigmaPotato token impersonation to spawn a SYSTEM…
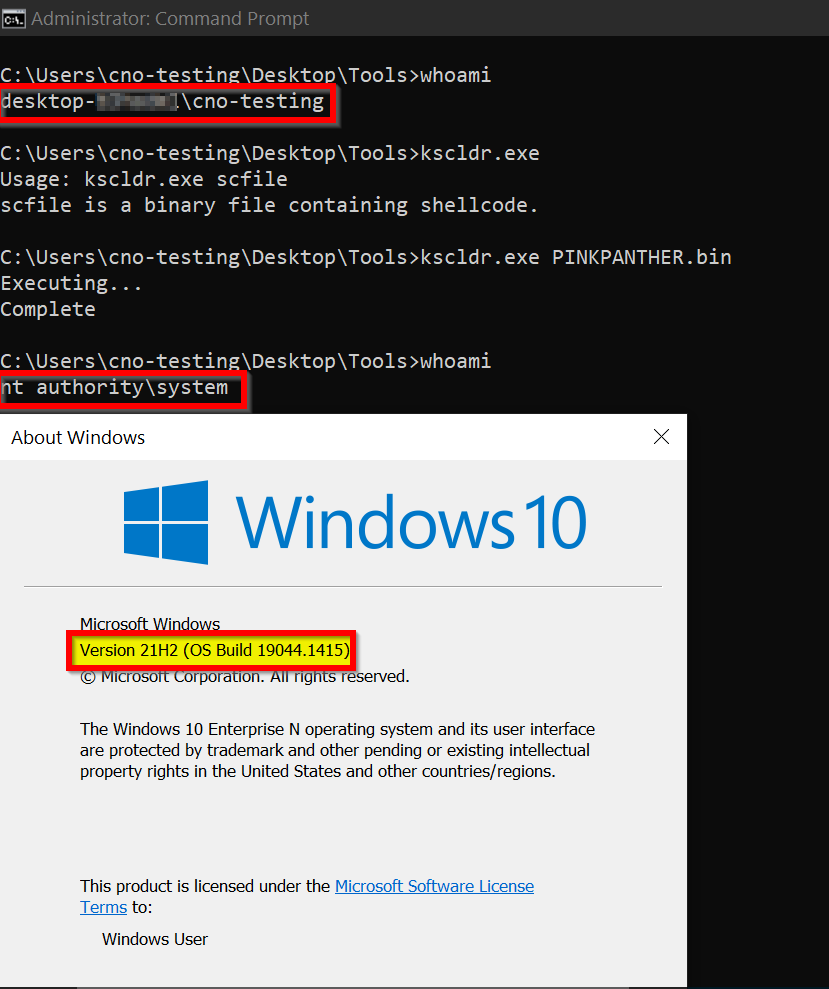 winterknife/pinkpanther
Windows x64 handcrafted token stealing kernel-mode shellcode
 rootkitsmm-zz/win10pcap-exploit
Exploit Win10Pcap Driver to enable some Privilege in our process token ( local Privilege escalation )
 hzphreak/vminjector
DLL Injection tool to unlock guest VMs
 explife0011/cve-2019-0803
Win32k Elevation of Privilege Poc
 iamgublin/cve-2019-0803
Win32k Elevation of Privilege Poc
 iamgublin/cve-2020-1054
Educational proof-of-concept exploit for CVE-2020-1054, a Windows kernel privilege escalation vulnerability, with analysis references and…
 uname1able/cve-2025-21333
Proof-of-concept exploit for CVE-2025-21333, a heap-based buffer overflow in Hyper-V's vkrnlintvsp.sys leading to local privilege escalation via I/O…
 jgoyd/ios-attack-chain-cve-2025-31200-cve-2025-31201
CVE-2025-31200 is a zero-day, zero-click RCE in iOS CoreAudio’s AudioConverterService, triggered by a malicious audio file via iMessage/SMS.…
 xvalegendary/hvcipwned
CVE-2024-35250 demonstrates that HVCI is not a defense against data-only kernel exploits. As long as a driver bug provides an arbitrary R/W…
 zeze-zeze/hitcon-2023-demo-cve-2023-20562
Demonstrates exploitation of AMD μProf driver (CVE-2023-20562) for privilege escalation via EPROCESS token write and DSE bypass, enabling unsigned…
 passwa11/hitcon-2023-demo-cve-2023-20562
Exploit for CVE-2023-20562 targeting AMD μProf driver to achieve SYSTEM privilege escalation via EPROCESS token arbitrary write, with DSE bypass and…
 mein-0/cve-2026-0828
Proof-of-concept exploit for CVE-2026-0828, a BYOVD vulnerability in Safetica ProcessMonitorDriver.sys allowing unprivileged termination of…
 rsmudge/cve-2020-0796-bof
Cobalt Strike Beacon Object File implementing CVE-2020-0796 SMBGhost local privilege escalation with dual weaponization paths for token theft and…
 hoangprod/cve-2021-31956-poc
Proof-of-concept exploit for CVE-2021-31956, a Windows kernel NTFS elevation-of-privilege vulnerability. Demonstrates exploitation techniques…