
cheat-engine-undetectable
 gmh5225/cheat-engine-undetectable
Academic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
binary-exploitationeducationexploitation+3
gmh5225/cheat-engine-undetectableAcademic Research Edition - T1: User-mode evasion (obfuscation + syscall gateway), T2: BYOVD kernel bridge, T3: DMA hardware (future work).
 openpixelsystems/c-copy-fail
C-based exploit for CVE-2026-31431 in the Linux Kernel Crypto API, targeting aarch64 and amd64 architectures with shellcode generation and ancillary…
 bugel/cve-2026-43499-m3q-azf1
This package is not a complete root. It flips SELinux to Permissive and holds reclaim long enough for follow-on work. Host `uid=0` is not achieved…
 hunt-benito/go-without-bounds-cve-2026-67822-stack-overflow-in-tenda-w6-s-wifissidset
PoC for CVE-2026-67822 stack overflow in Tenda W6-S /goform/wifiSSIDset: DoS reproducer, QEMU MIPS shim, and conceptual RCE payload skeleton.
 spiralbl0ck/rowhammer-exploit
RowHammer Based-Exploit
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 kpwn/yalu102
incomplete iOS 10.2 jailbreak for 64 bit devices by qwertyoruiopz and marcograssi
 spiralbl0ck/ai_hacking
Collection of CVE(work) on tenserflow binary pwning it
 rohilchaudhry/cve-2024-48208
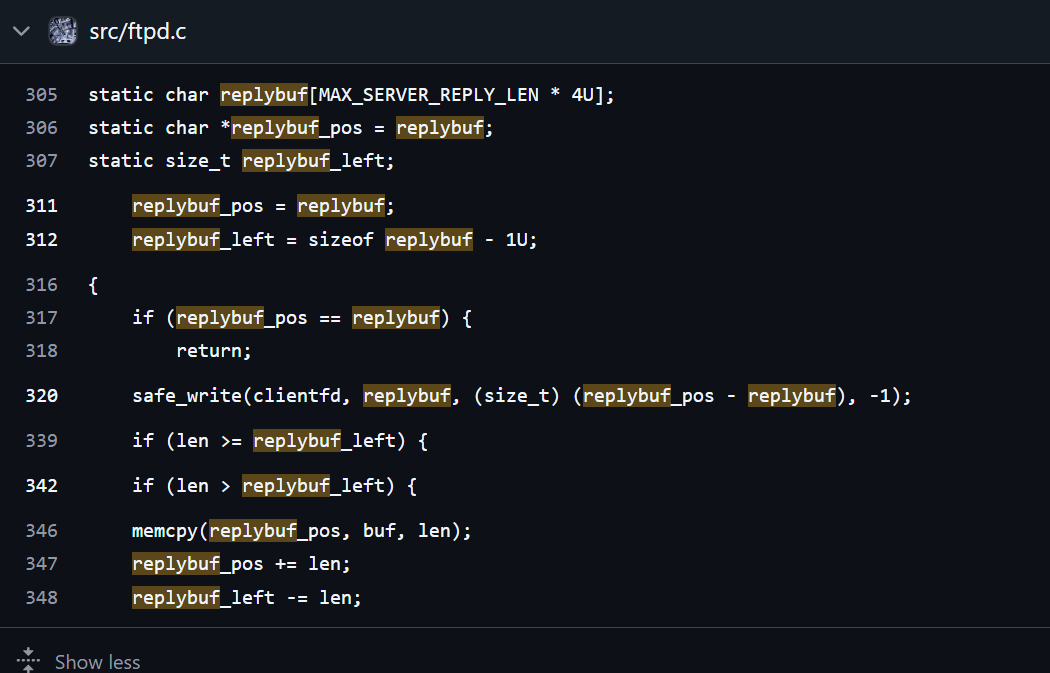
This repo contains all the work surrounding the development of the PoC for CVE-2024-48208, and how a simple OOB(Out-of-bound) read can result in jail…
 skyshell20082008/cve-2019-0708-poc-hitting-path
It's only hitting vulnerable path in termdd.sys!!! NOT DOS
 ycdxsb/cve-2020-0668
Make CVE-2020-0668 exploit work for version < win10 v1903 and version >= win10 v1903
 it19083124/snp-assignment
Exploit work Privilege Escalation CVE-2017-1000112

 ldebug/extra_recipe
Ian Beer's exploit for CVE-2017-2370 (kernel memory r/w on iOS 10.2)
 liuk3r/cve-2023-32233
CVE-2023-32233: Linux内核中的安全漏洞
 p4x1s/cve-2023-21716-poc
Microsoft Word 远程代码执行漏洞