
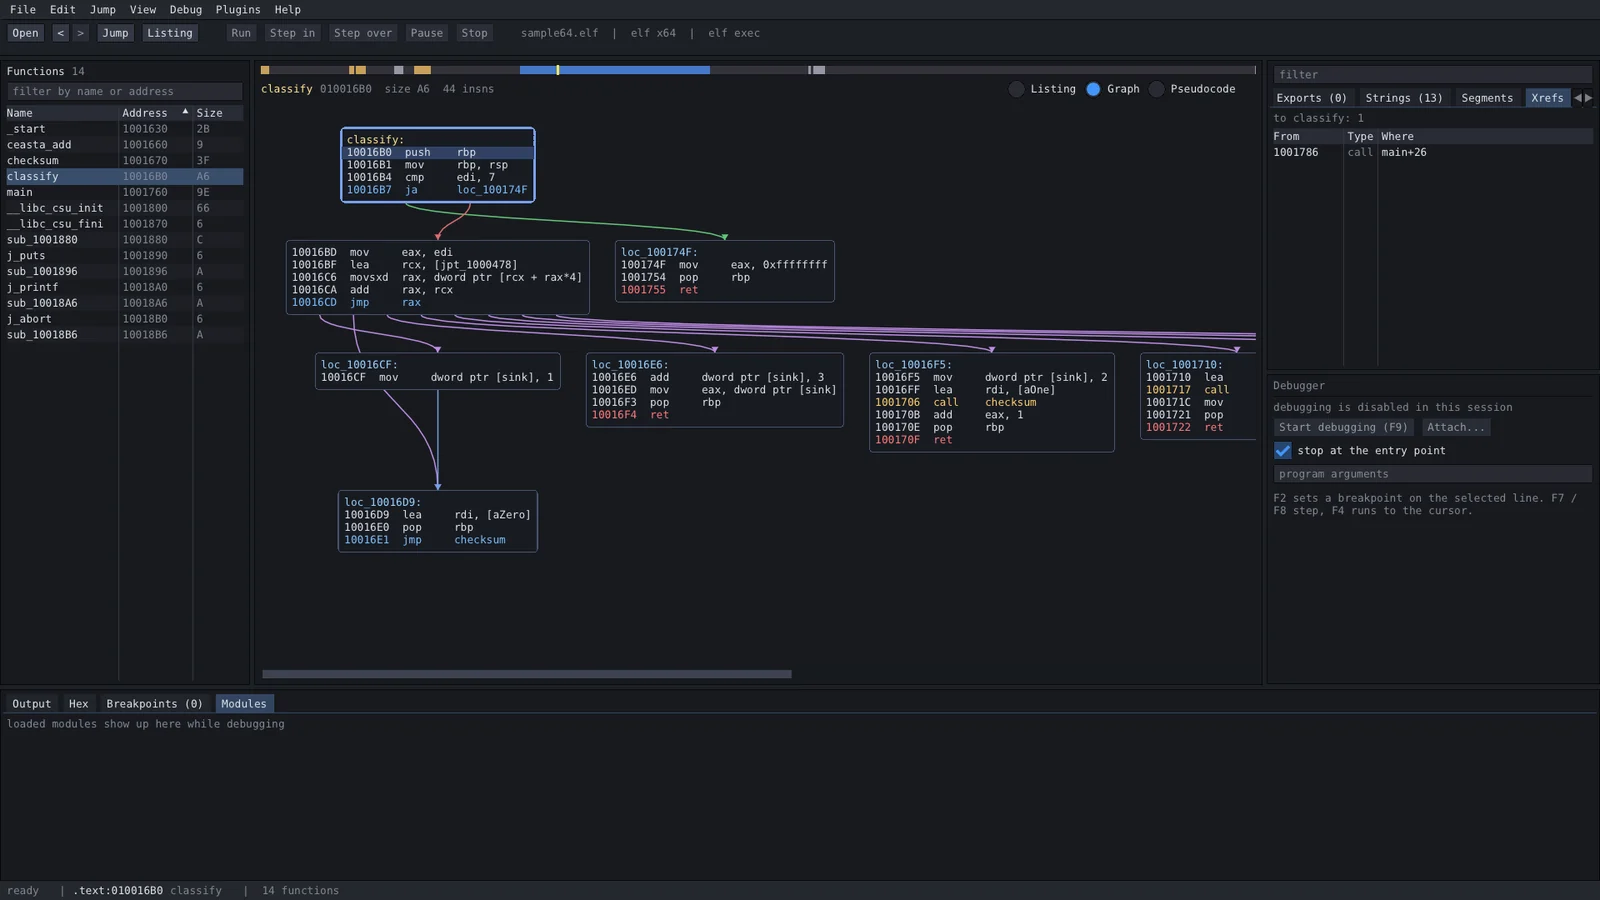
ceasta
 ngwg/ceasta
reverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
ai-assisted-reversingbinary-analysisbinary-exploitation+6
25
ngwg/ceastareverse engineering tool with a built-in MCP server: an AI can debug your binary, not just read it — breakpoints, stepping, memory, calling…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 vilasboasph/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV path manipulation.
 phvilasboas/cve-2021-4034
Exploit for CVE-2021-4034, a local privilege escalation in polkit's pkexec, providing a root shell via a shared library and GCONV_PATH manipulation.
 pengalaman-1t/cve-2021-4034
Exploit for CVE-2021-4034 (PwnKit) that provides a root shell via polkit pkexec vulnerability. Includes source code and build instructions.
 an0n7os/cve-2021-4034
Exploit for CVE-2021-4034, a polkit pkexec privilege escalation vulnerability, providing a root shell on vulnerable Linux systems.
 tanmay-n/cve-2021-4034
Exploit for CVE-2021-4034 in polkit pkexec, providing a root shell via a SUID privilege escalation. Includes source code and build instructions.
 rakhithjk/cve-2021-4034-new
Exploit for CVE-2021-4034 (polkit pkexec) that provides a root shell. Includes build instructions and references the original advisory.
 begitdj/cve-2019-2215-markw
Exploit for CVE-2019-2215 to gain temporary root on Xiaomi MIUI devices, enabling bootloader unlock and system modifications.
 nanoturtle1145/root-my-s24
Using CVE-2026-43499 to root your Galaxy S24 Series(SM-S92X0 ,(China / Hong Kong SAR / Taiwan))
 bsauce/kernel-exploit-factory
Linux kernel CVE exploit analysis report and relative debug environment. You don't need to compile Linux kernel and configure your environment…
 aarif450/zapscape
Guest-to-host KVM/x86 escape exploiting CVE-2026-64561, delivering a full PoC chain and analysis for security researchers.
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 shellphish/how2heap
A repository for learning various heap exploitation techniques.
 spiralbl0ck/hackerlife.exe
Write up exploit failed chain and experience tryin to sell your first nday
 jakeblair420/totally-not-spyware
webkit; but pwned