
Skip to content
KitploitKITPLOIT
ToolsExploitsBlog
Log in
Submit
ToolsExploitsBlog
Submit

Hacking, PenTest, and Cybersecurity Tools for Your Security Arsenal!

Kitploit is a directory of hacking, cybersecurity, and pentesting tools. Discover the latest project updates to find vulnerabilities, analyze systems, automate testing, and strengthen your security.

FeedsContactPrivacy© 2026 Kitploit

Tool Directory

Categories

View all categories
Loading categories

Tools

AllAndroid SecurityAuthentication & AuthorizationCloud Infrastructure SecurityDefensive ToolsDisk ForensicsEmbedded Systems SecurityGeneral Purpose UtilitiesIndicator of Compromise (IOC) ManagementOSINT (Open Source Intelligence)Packet Sniffing & AnalysisPassword CrackingPenetration Testing FrameworksPhishing ToolsPrivilege EscalationReconnaissanceStatic AnalysisVulnerability ScannersWeb Vulnerability ScannersWi-Fi AuditingBluetooth SecurityContainer SecurityDynamic Analysis (Sandboxing)Encryption/Decryption ToolsExploit FrameworksIdentity ManagementiOS SecurityIoT SecurityMemory ForensicsNetwork MappingOSINT for Social EngineeringPassword AttacksPayload GenerationPersistence MechanismsPort ScanningStatic Code Analysis (SAST)Threat Feeds & AggregatorsVulnerability AnalysisWeb Proxies & InterceptionCode AnalysisDNS & Subdomain EnumerationDynamic Code Analysis (DAST)ExploitationHash AnalysisIDS/IPS EvasionImpersonation ToolsLateral MovementMobile App PentestingNetwork ForensicsReverse EngineeringRFID/NFC ToolsSCADA/ICS SecurityScripting & AutomationServerless SecurityShellcodeWeb Application ExploitationAPI Security TestingConfiguration AuditingData ExfiltrationDebuggersForensicsInformation GatheringMobile ForensicsNetwork Access ControlPost-ExploitationSecurity VirtualizationPhishingWAF BypassWeb SecurityFuzzingNetwork SecuritySteganographyWireless SecurityData RecoveryMalware AnalysisDigital ForensicsHardware HackingCryptographyCTFPenetration TestingCloud SecurityDevSecOpsMobile SecurityPrivacyCommand and ControlSocial EngineeringHardware SecurityUtilities & FrameworksHardware & IoT SecuritySecret DetectionBinary AnalysisThreat IntelligenceIdentity & Access Management (IAM)Supply Chain SecurityAuthenticationMachine LearningIntrusion DetectionPapers & ResearchMisconfigurationSubdomain EnumerationEmail HarvestingLearning & EducationAI-Assisted ReversingDNS FuzzingRed TeamingIncident ResponseCrawlerCurated ResourcesRemote Access ToolShellcode GenerationPayload DevelopmentRemote Access TrojanAPI SecurityAnti-BotFingerprint SpoofingCAPTCHA BypassEmail SecurityDNS AnalysisChaos EngineeringLearning Paths & CoursesContainer EscapeAI SecurityDatabase SecurityFirmware AnalysisAnomaly DetectionLog AnalysisAdversarial AttackBinary ExploitationLabs & Practice
NewestRelevanceMost popularRecently updated
94 results
KnockGiga preview

KnockGiga

GitHubmein-0/knockgiga

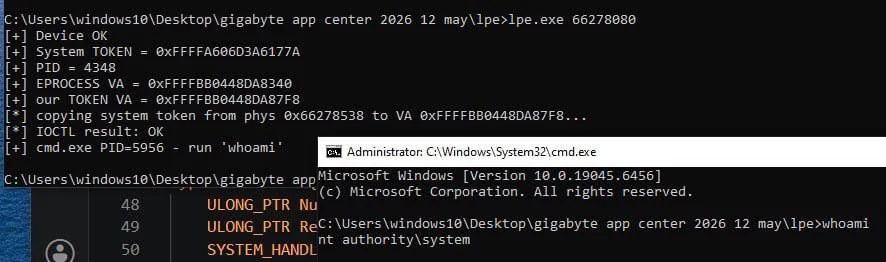
Proof-of-concept local privilege escalation exploiting Gigabyte gdrv3.sys IOCTLs to write the SYSTEM token into a user process via an unchecked…

binary-exploitationexploitationhardware-security+3
11
11 days ago
memory-relocalloc preview

memory-relocalloc

GitHubgmh5225/memory-relocalloc

C proof-of-concept that locates code caves in the .reloc section of mapped DLLs to allocate and execute small shellcode, replacing typical memory…

binary-exploitationexploitationmalware-analysis+6
24 years ago
KDU preview

KDU

GitHubhfiref0x/kdu

Windows kernel driver utility that abuses vulnerable signed drivers (BYOVD) to bypass DSE, load unsigned drivers, hijack protected processes, and…
binary-exploitationdefensive-toolsexploitation+8
2.8k29 days ago
NativePe preview

NativePe

GitHubhabanada/nativepe

Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
binary-analysisbinary-exploitationdynamic-analysis-sandboxing+5
1927 days ago
ps-ppl-bypass preview

ps-ppl-bypass

GitHubr41n3rzuf477/ps-ppl-bypass

Process Explorer vulnerable driver PPL Bypass
binary-exploitationdefensive-toolsexploitation+5
2727 days ago
IAT-Hook preview

IAT-Hook

GitHubgmh5225/iat-hook

C++ DLL that performs Import Address Table hooking by parsing PE headers and redirecting imported function addresses to a custom hook inside a target…
binary-exploitationcode-analysismalware-analysis+4
4 years ago
linux-env-vars-shellshock-lab preview

linux-env-vars-shellshock-lab

GitHubmgiftson0/linux-env-vars-shellshock-lab

technical research & analysis on linux process execution, SUID privilege escalation, LD_PRELOAD hooking, and CVE-2014-6271 (shellshock).
binary-exploitationeducationexploitation+3
1 month ago
CVE-2026-85048-the-gpu-died preview

CVE-2026-85048-the-gpu-died

GitHubsneakynachos/cve-2026-85048-the-gpu-died

Reproducer and technical analysis for CVE-2026-85048, a Chrome viz surface use-after-free in the GPU process, with ASAN unit tests and browser…
binary-exploitationdebuggersexploitation+4
11 month ago
DsArk64 preview

DsArk64

GitHubgmh5225/dsark64

BYOVD proof-of-concept abusing the WHQL-signed DsArk64.sys driver for ring-0 process termination and kernel read/write via encrypted IOCTLs and…

binary-exploitationdefensive-toolsexploitation+6
136 months ago
CVE-2026-74586 preview

CVE-2026-74586

GitHubtarpeg007/cve-2026-74586

Unprivileged proof-of-concept for CVE-2026-74586, a Linux kernel SCTP ASCONF use-after-free. Provides a raw-packet trigger, reliability metrics, and…
binary-exploitationexploitationexploit-frameworks+1
11 month ago
evil-mhyprot-cli preview

evil-mhyprot-cli

GitHubkkent030315/evil-mhyprot-cli

A PoC for Mhyprot2.sys vulnerable driver that allowing read/write memory in kernel/user via unprivileged user process.
binary-exploitationexploitationprivilege-escalation+2
3575 years ago
CVE-2026-31431-live-process-code-injection preview

CVE-2026-31431-live-process-code-injection

GitHubkvakirsanov/cve-2026-31431-live-process-code-injection

Proof-of-concept for CVE-2026-31431 demonstrating live process code injection via page cache, achieving arbitrary code execution in a running process…
binary-exploitationexploitationexploit-frameworks+1
25 months ago
CVE-2026-1880 preview

CVE-2026-1880

GitHubseokjohn/cve-2026-1880

ASUS DriverHub Driver Update Process TOCTOU Vulnerability Leading to LPE
binary-exploitationexploitationprivilege-escalation+1
56 months ago
KillChain preview

KillChain

GitHuboxfemale/killchain

Kernel Process Termination Tool ( CVE-2026-0828 exploit)
binary-exploitationexploitationmalware-analysis+3
386 months ago
CVE-2026-3796 preview

CVE-2026-3796

GitHubcwjchoi01/cve-2026-3796

Proof-of-concept exploit for CVE-2026-3796, demonstrating arbitrary process termination via a vulnerable QAX driver. Includes usage instructions and…
binary-exploitationeducationexploitation+1
47 months ago
CVE-2026-74939-escape-the-mac-n-cheese-box preview

CVE-2026-74939-escape-the-mac-n-cheese-box

GitHubsneakynachos/cve-2026-74939-escape-the-mac-n-cheese-box

Firefox content-to-parent IPDL privilege escalation (N-day, bug 2054416): forged PDocumentChannel with RemoteTypeOverride -> privilegedabout process…
binary-exploitationexploitationexploit-frameworks+3
12 months ago
CVE-2026-2796-and-CVE-2026-2768-escape-the-wasm-box preview

CVE-2026-2796-and-CVE-2026-2768-escape-the-wasm-box

GitHubsneakynachos/cve-2026-2796-and-cve-2026-2768-escape-the-wasm-box

Full Firefox chain: CVE-2026-2796 wasm type confusion -> content-process RCE, plus CVE-2026-2768 parent-process escape analysis (both fixed in…
binary-exploitationexploitationvulnerability-analysis+1
12 months ago
cve-2026-62737-lab preview

cve-2026-62737-lab

GitHubdavidcarliez/cve-2026-62737-lab

Elevates a low-privilege Windows process to SYSTEM via a gdb-assisted ROP token-swap chain, demonstrating CVE-2026-62737 in a lab-only QEMU…

binary-exploitationdebuggersexploitation+2
22 months ago
Previous123456Next