
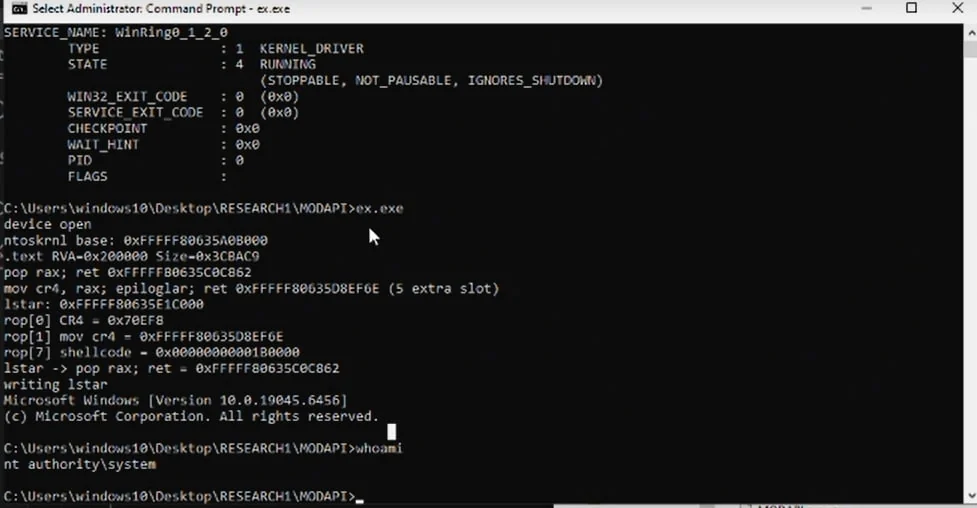
LolModapi
 mein-0/lolmodapi
Local privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
binary-exploitationexploitationprivilege-escalation+2
4
mein-0/lolmodapiLocal privilege escalation exploit for MSI Dragon Center's MODAPI.sys driver, abusing unauthenticated MSR writes to bypass SMEP and gain SYSTEM.
 rwfpl/rewolf-msi-exploit
MSI NTIOLib/WinIO Local Privilege Escalation exploit
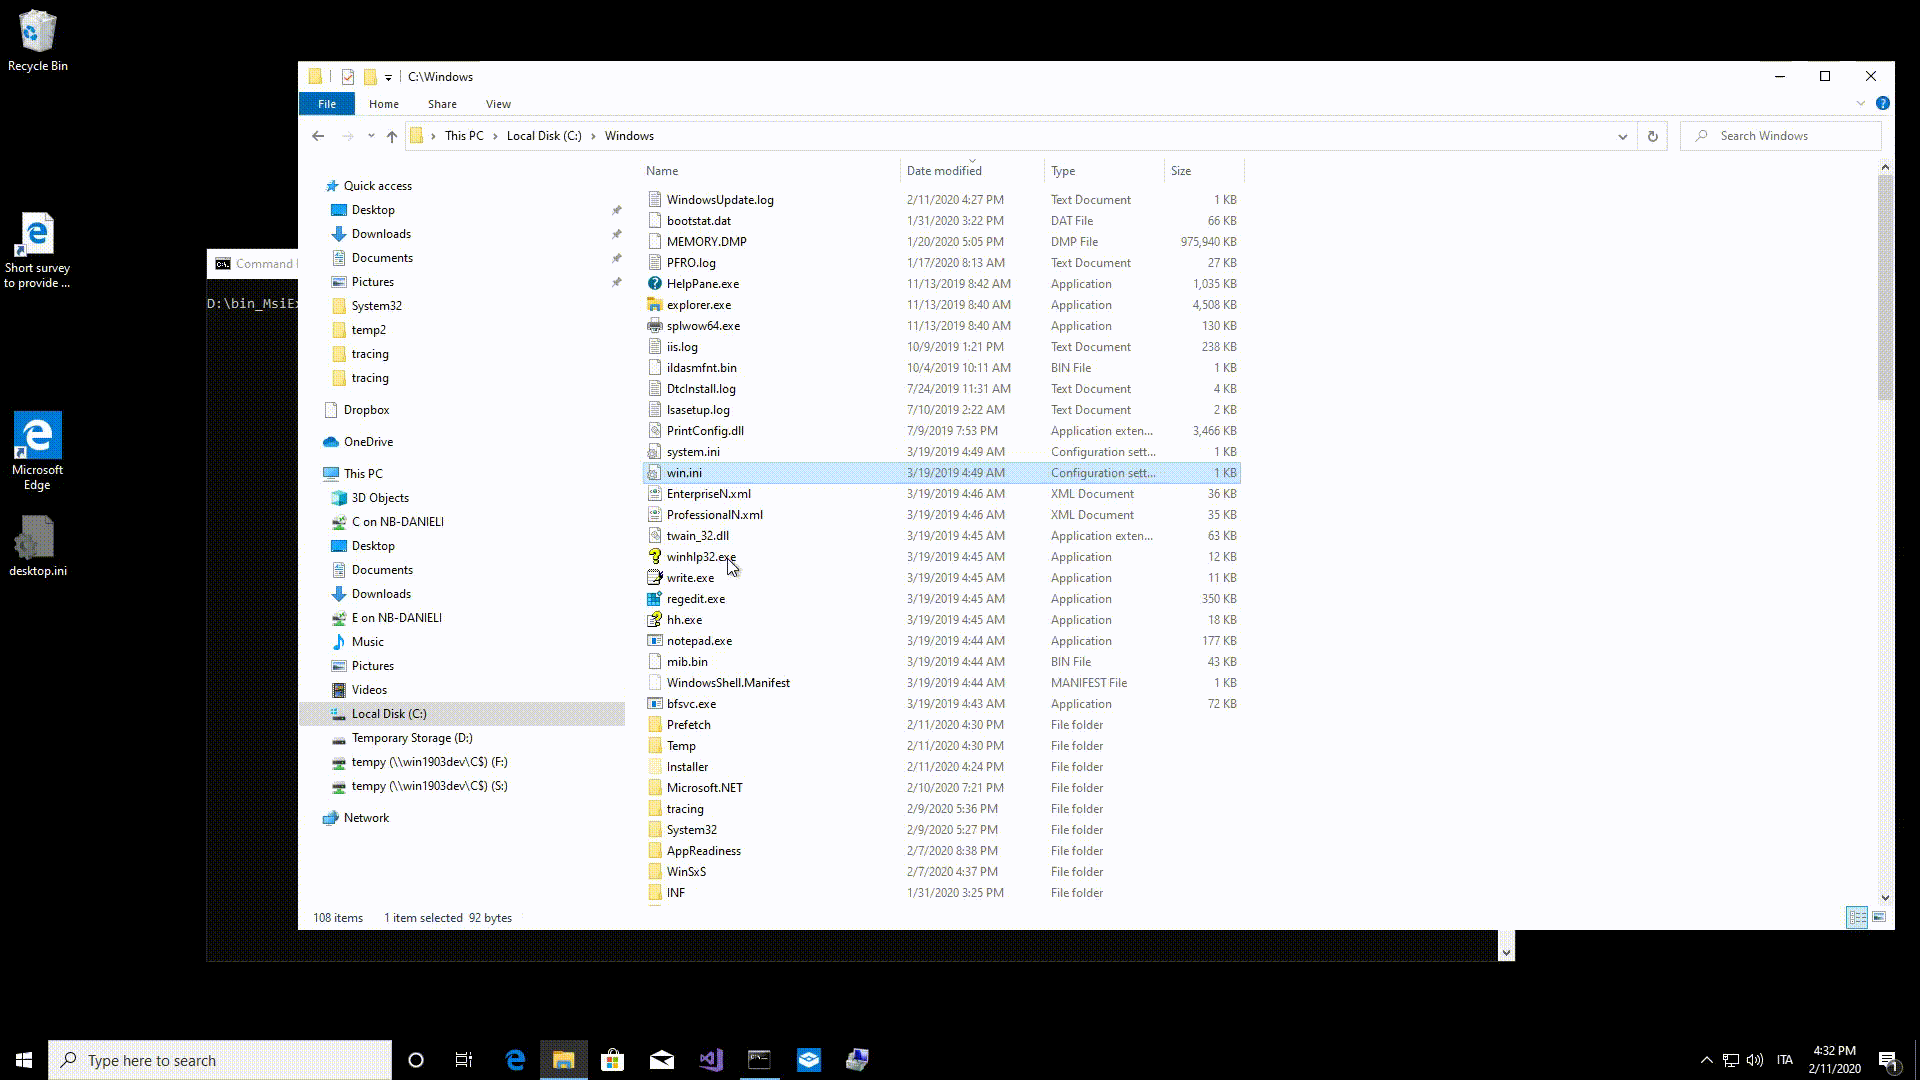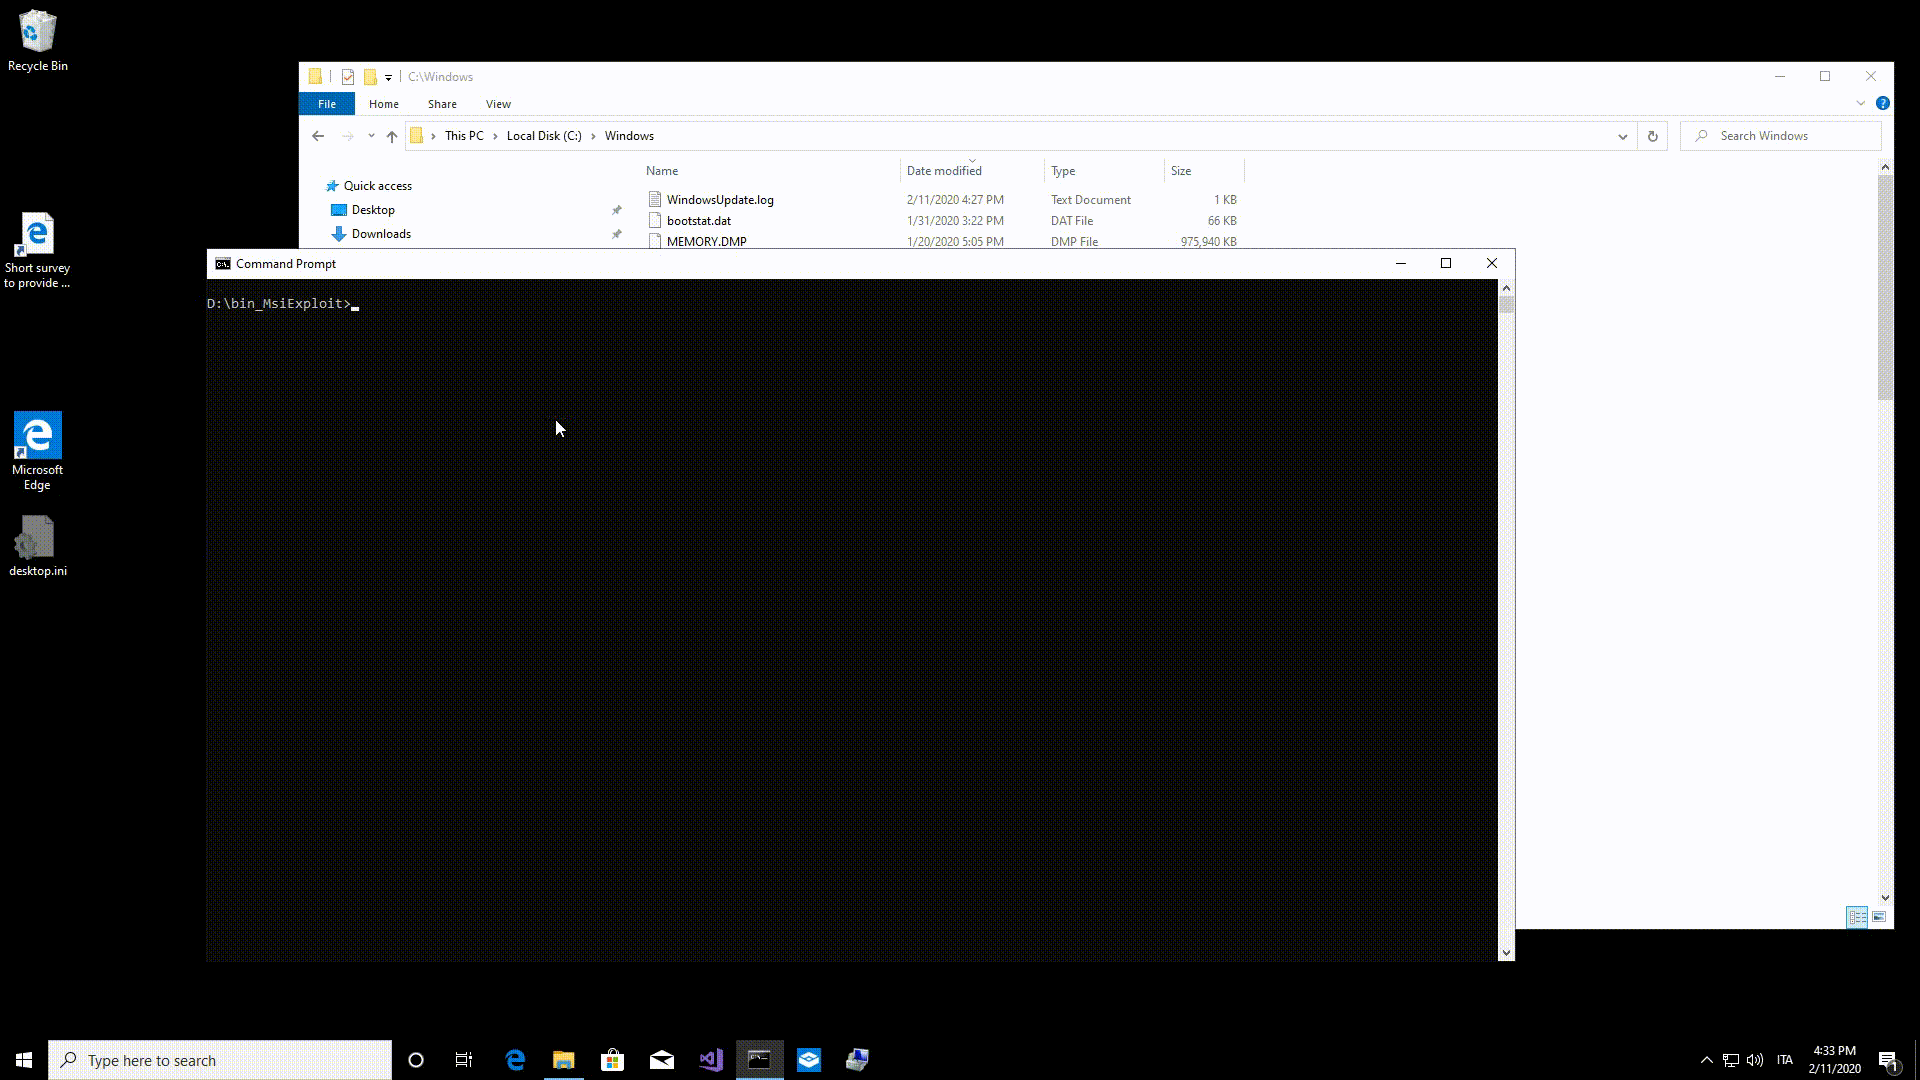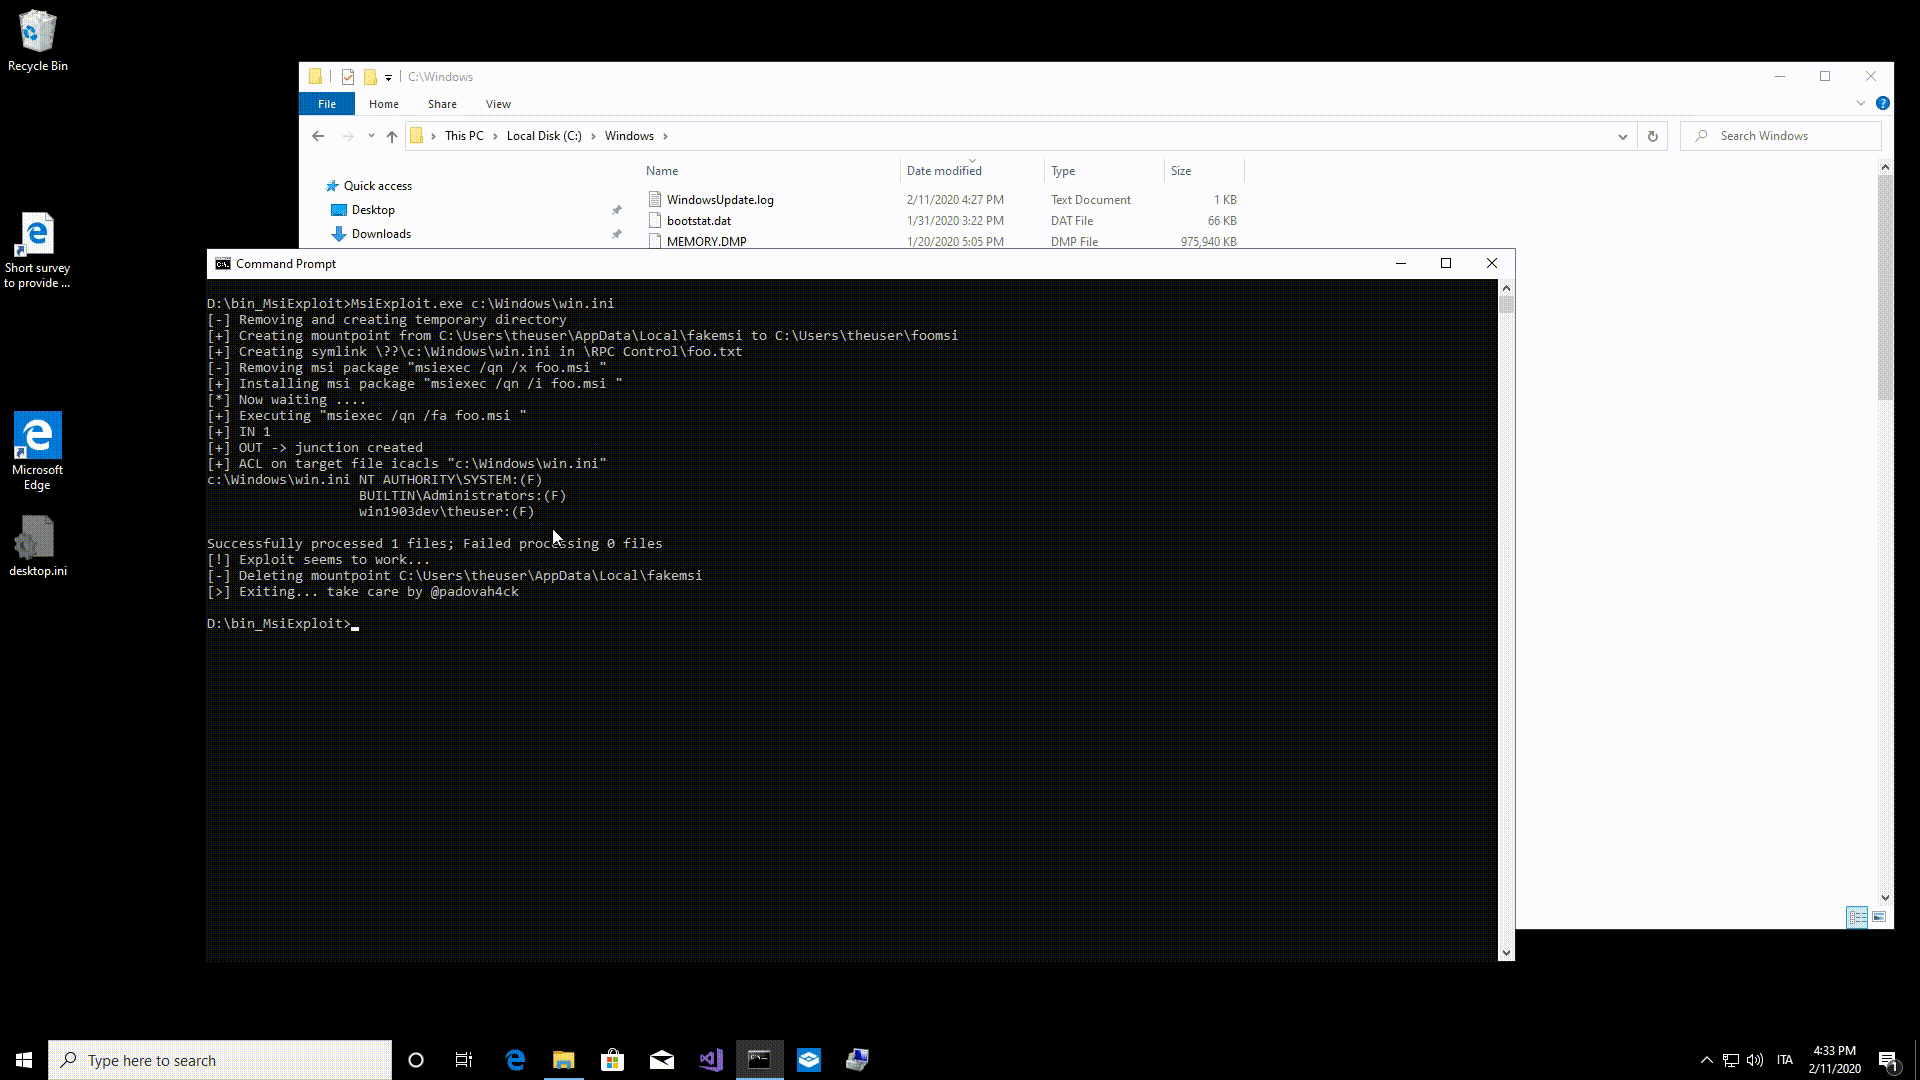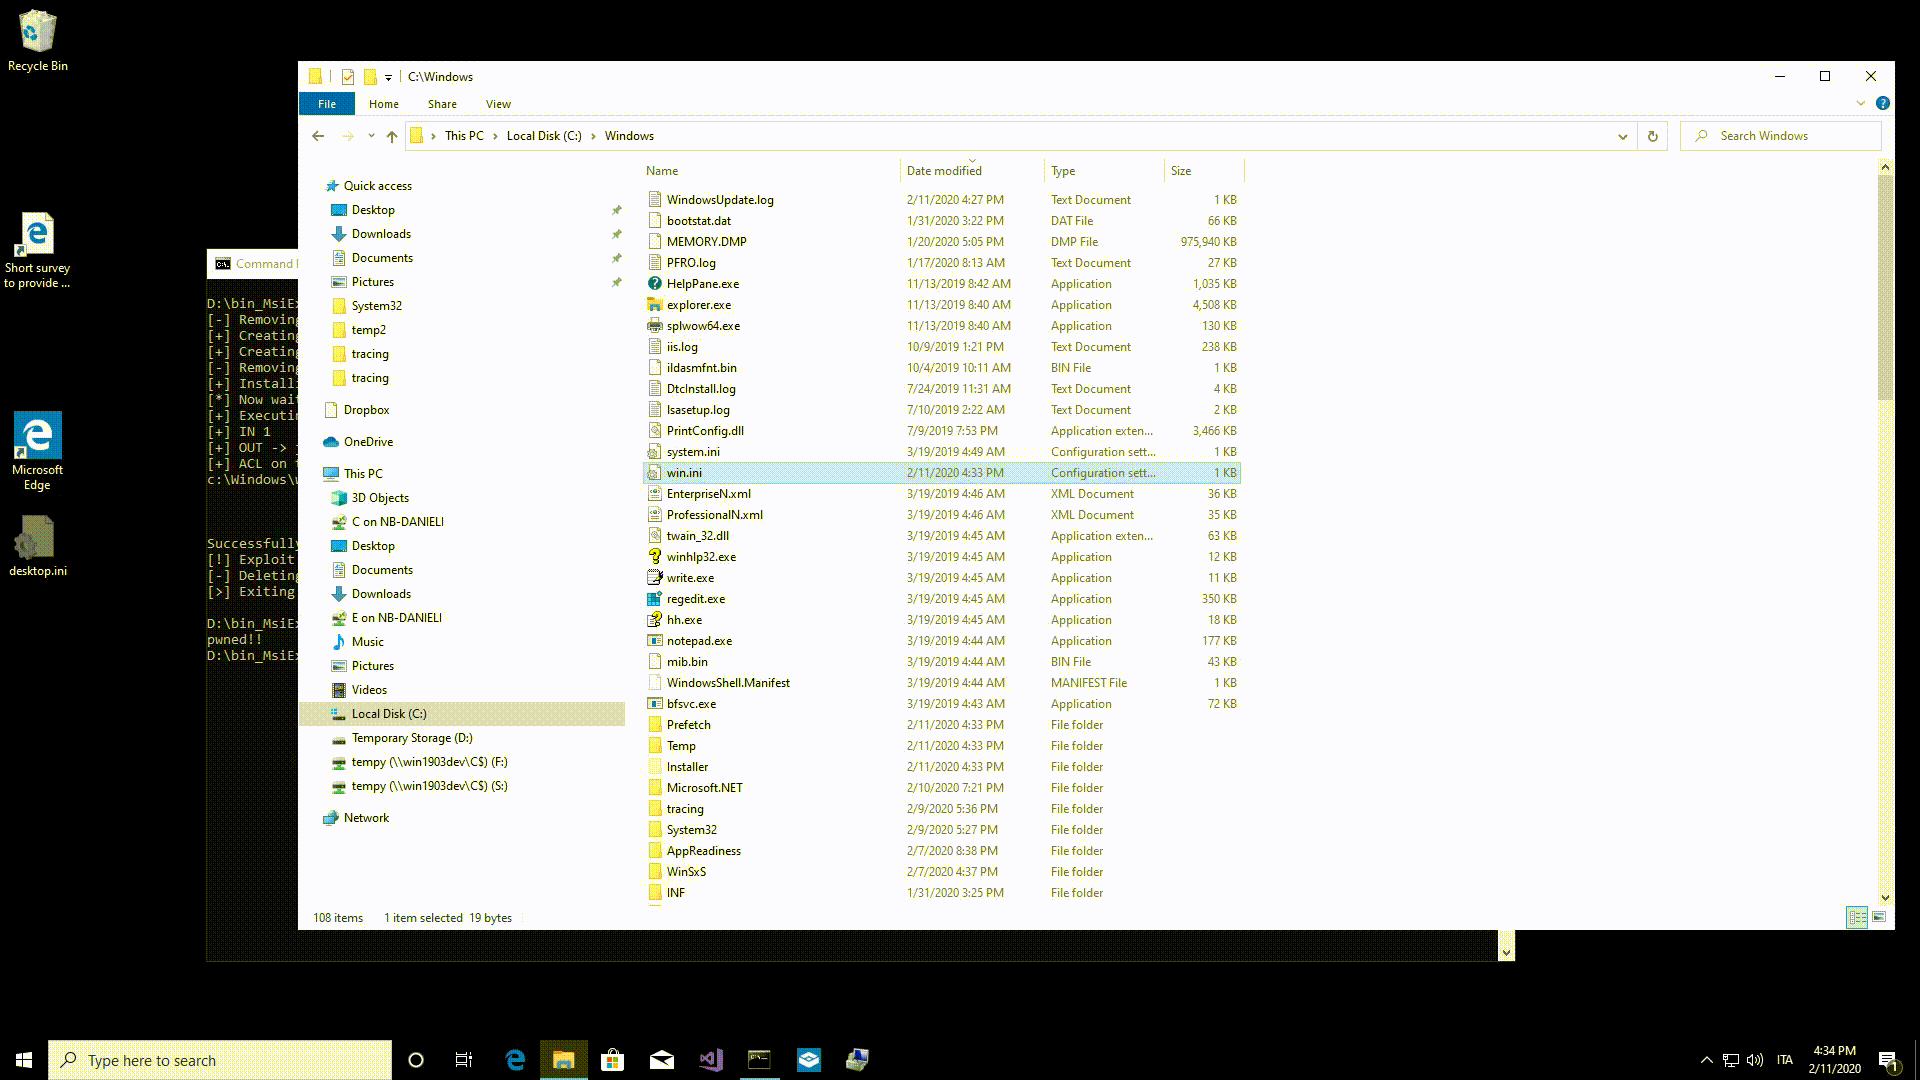 padovah4ck/cve-2020-0683
CVE-2020-0683 - Windows MSI “Installer service” Elevation of Privilege
 hi0u/poc-cve-2024-12227
# CVE-2024-12227 - NTIOLib_X64.sys DoS PoC
 offensive-panda/nt-authority-system-context-rtcore
This exploit rebuilds and exploit the CVE-2019-16098 which is in driver Micro-Star MSI Afterburner 4.6.2.15658 (aka RTCore64.sys and RTCore32.sys)…
 nextgenpentesters/cve-2024-37726-msi-center-local-privilege-escalation
C++ exploit for CVE-2024-37726, an arbitrary file overwrite vulnerability in MSI Center enabling local privilege escalation on Windows systems.
 rjt-gupta/cve-2021-29337
CVE-2021-29337 - Privilege Escalation in MODAPI.sys (MSI Dragon Center)
 hessandrew/cve-2020-9442
OpenVPN Connect for Windows (MSI) - 3.1.0.361 - Privilege Escalation
 g3tsyst3m/cve-2024-50804
Proof-of-concept exploit for CVE-2024-50804, an arbitrary write privilege escalation vulnerability in MSI Center Pro 2.1.37.0, with detailed writeup…
 fengjixuchui/cve-2021-27965
The MsIo64.sys driver before 1.1.19.1016 in MSI Dragon Center before 2.0.98.0 has a buffer overflow that allows privilege escalation via a crafted…
 elsevar11/cve-2024-0670-checkmk-agent-local-privilege-escalation-exploit
This repository contains an exploit demonstration for CVE-2024-0670, a local privilege escalation vulnerability affecting the CheckMK Agent for…
 carsonchan12345/cve-2024-37726-msi-center-local-privilege-escalation
Proof-of-concept for CVE-2024-37726: local privilege escalation in MSI Center via arbitrary file overwrite using symlink/junction attacks and OpLock…
 barakat/cve-2019-16098
Local privilege escalation PoC exploit for CVE-2019-16098