
libextractor-privesc
 haitam-lazaar/libextractor-privesc
Proof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
binary-exploitationeducationexploitation+3
haitam-lazaar/libextractor-privescProof-of-concept for CVE-2026-100310, a local privilege escalation in GNU libextractor ≤1.15 via the LIBEXTRACTOR_PREFIX untrusted search path, with…
 haitam-lazaar/libextractor-ole2-rce
PoC for a Critical stack-based buffer overflow in GNU libextractor ≤ 1.14. A malicious .doc file triggers an unbounded VLA allocation causing…
 chosenonehacks/cve-2026-32746
Proof-of-concept exploit for a pre-authentication buffer overflow in GNU InetUtils telnetd (CVE-2026-32746), including a Docker lab environment and…
 jeffaf/cve-2026-32746
CVE-2026-32746 - GNU InetUtils telnetd LINEMODE SLC Buffer Overflow PoC (pre-auth RCE, CVSS 9.8)
 rvzsec/cve-2024-2961
CVE-2024–2961 Security Issue Mitigation Script
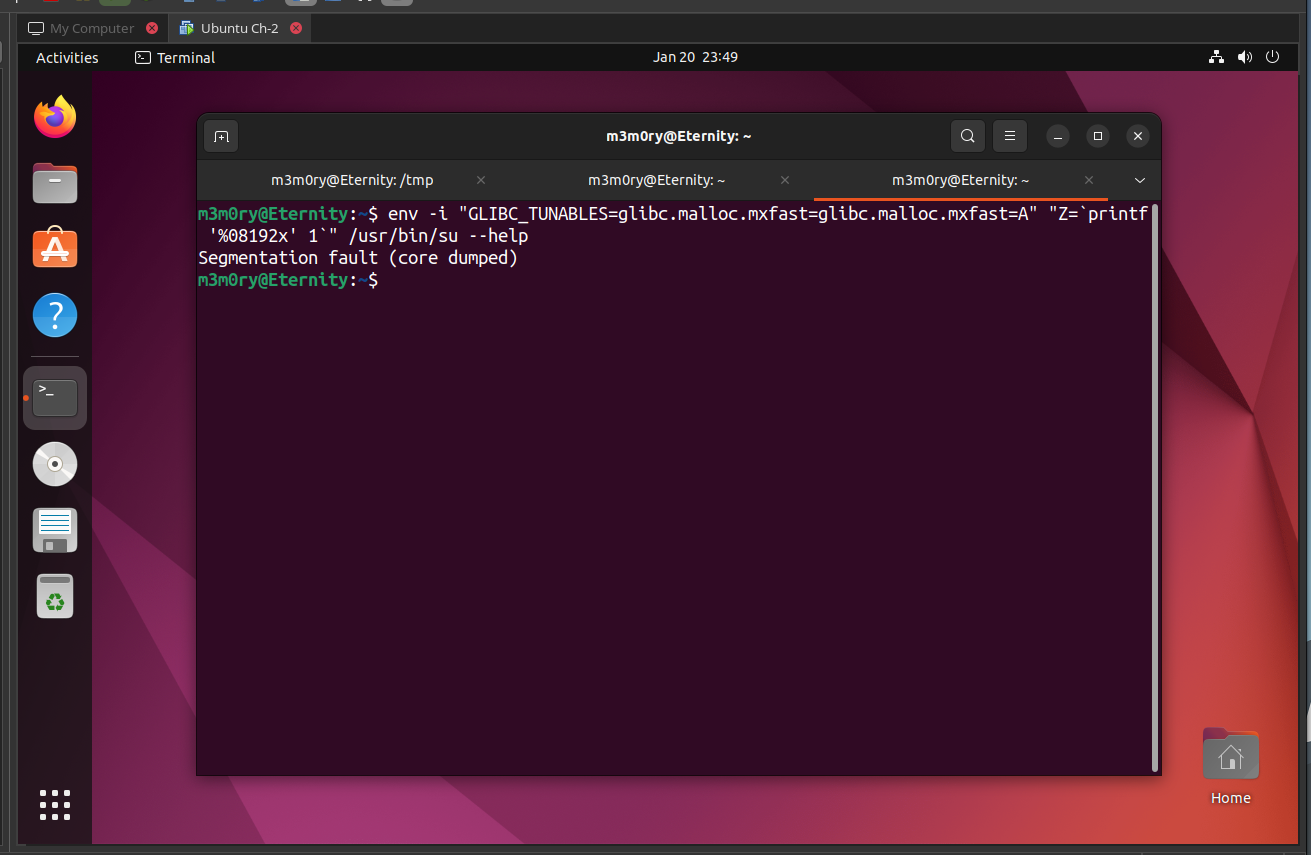 nishanthanand21/cve-2023-4911-poc
Repository containing a Proof of Concept (PoC) demonstrating the impact of CVE-2023-4911, a vulnerability in glibc's ld.so dynamic loader, exposing…
 4d4j/objdump-out-of-bounds-write
Proof of Concept (PoC) demonstrating the CVE-2026-18220, an out-of-bounds (OOB) write vulnerability in the DLX ELF backend of GNU binutils…
 hironull/cve-2018-1207-better
Reverse Shell CVE for iDRAC 7 & 8 with firmware 2.52.52.52 and below.
 exfil0/test_iconv
This repository contains a C program to test for CVE-2024-2961, a buffer overflow vulnerability in the iconv() function of glibc.
 jedai47/cve-2018-17182
Proof-of-concept exploit for CVE-2018-17182, a Linux kernel use-after-free vulnerability in the mm subsystem, demonstrating privilege escalation via…
 valentin-metz/writeup_split
Writeup of a heap overflow vulnerability in the GNU coreutils split program. CVE-2024-0684
 ekomssavior/telnet_scan
scanner/exploiter CVE-2026-24061 & CVE-2026-32746
 aryan20057/cve-2023-4911
Exploit for CVE-2023-4911, a privilege escalation vulnerability in GNU C Library's dynamic loader, demonstrating buffer overflow exploitation.
 0xmoga/cve-2023-4911-lab
Docker-based CVE-2023-4911 lab for analyzing glibc ld.so buffer overflow and developing a local privilege escalation exploit with GDB debugging.