
fuck_cve_2026_31431
Kernel module exploiting CVE-2026-31431 to bypass system stop mechanisms, with configurable fake implementation for testing on non-stoppable machines.
binary-exploitationexploitationprivilege-escalation+1
Kernel module exploiting CVE-2026-31431 to bypass system stop mechanisms, with configurable fake implementation for testing on non-stoppable machines.

Proof-of-concept exploit for CVE-2022-26809, a Windows RPC runtime integer overflow vulnerability. Includes trigger scripts using PetitPotam-style…

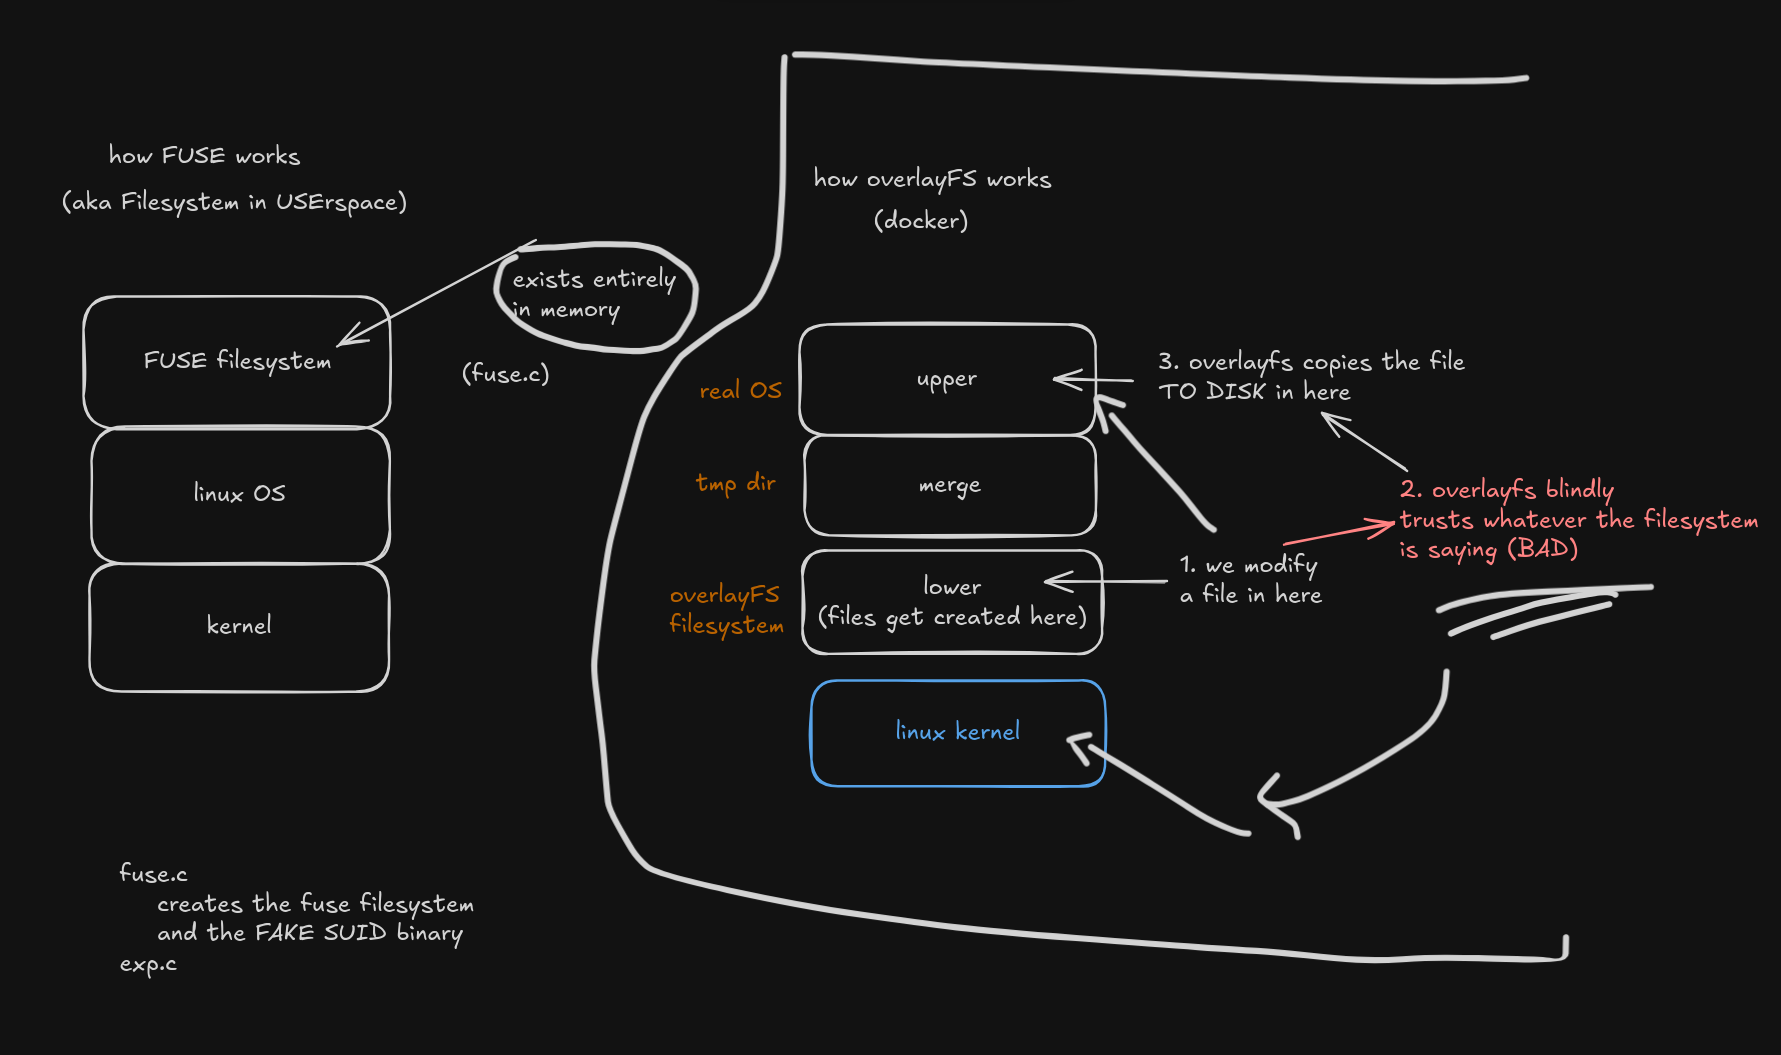
Copy fake in-memory files to disk using overlayFS

Proof-of-concept exploit for CVE-2017-9606: local privilege escalation in ViPNet Client/Coordinator via crafted update files with arbitrary code…