
CVE-2022-22715
 vportal/cve-2022-22715
Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
binary-exploitationexploitationpapers-research+2
vportal/cve-2022-22715Exploit code for CVE-2022-22715 (Windows Dirty Pipe), a sandbox escape and privilege escalation via named pipe TOKEN object corruption, with a linked…
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 themalwareguardian/cve-2022-34302
Demonstrates CVE-2022-34302, a Secure Boot bypass via the New Horizon Datasys signed bootloader whose built-in custom PE/COFF loader executes…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 abdul-kalam2000/retbleed-speculative-execution-poc
Reproduction of the Retbleed (CVE-2022-29900/29901) micro-architectural attack in gem5. RSB underflow, Flush+Reload side-channel leak, and a verified…
 vudangducminh/cve-2022-0847
Proof-of-concept exploit for CVE-2022-0847 (Dirty Pipe), a Linux kernel race condition enabling unprivileged writes to read-only files and privilege…
 uname1able/cve-2026-24291
Proof-of-concept exploit for CVE-2026-24291 targeting Windows 10 21H2 (build 19044.6937) AMD64, developed in C# with Visual Studio 2022.
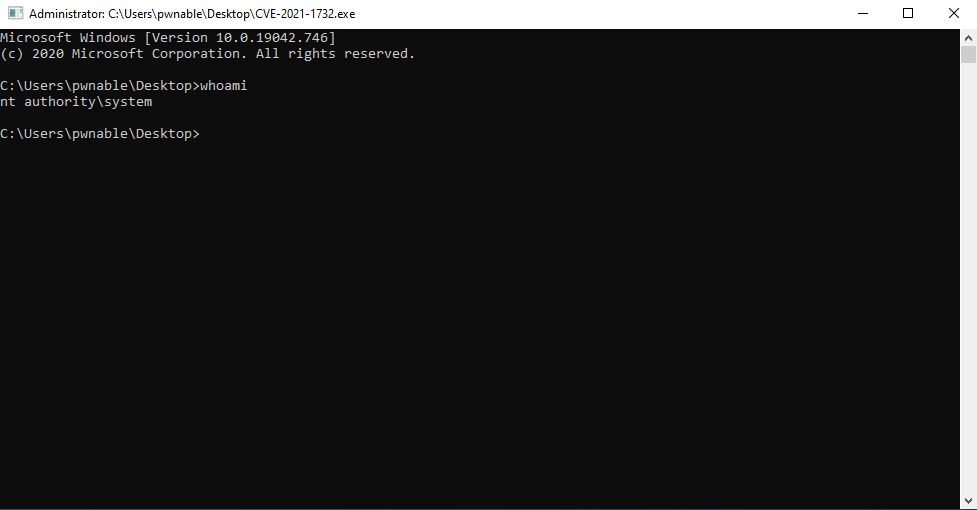 r1l4-i3pur1l4/cve-2021-1732
Windows kernel privilege escalation exploit for CVE-2021-1732, a Win32k elevation of privilege vulnerability, with techniques inspired by related…
 uname1able/cve-2026-2636
Proof-of-concept exploit for CVE-2026-2636 targeting Windows 11 23H2 x64, built with Visual Studio 2022 and Windows SDK 10.0.
 uname1able/cve-2026-20820
Windows kernel exploit for CVE-2026-20820, targeting Windows 10 21H2 and Windows 11 23H2, built with Visual Studio 2022.
 an00brektn/cve-2021-4034
Golang implementation of CVE-2021-4034, a local privilege escalation exploit for polkit's pkexec, with mitigation instructions and educational notes.
 ericpardee/fire-hd-ownership
Owning a tablet Amazon kept shutting down — CVE-2022-38181 write-up, four AI models, and a blog
 veritas501/pipe-primitive
An exploit primitive in linux kernel inspired by DirtyPipe
 pablomk7/enlbufferpwn
Information and PoC about the ENLBufferPwn vulnerability
 alfarom256/hphardwarediagnostics-poc
PoC exploit for HP Hardware Diagnostic's EtdSupp driver
 edubr2020/rp_recordclip_dll_hijack
Remote DLL hijack exploit for Real Player (CVE-2022-32291) using malicious DLLs from WebDAV/SMB shares to achieve code execution.
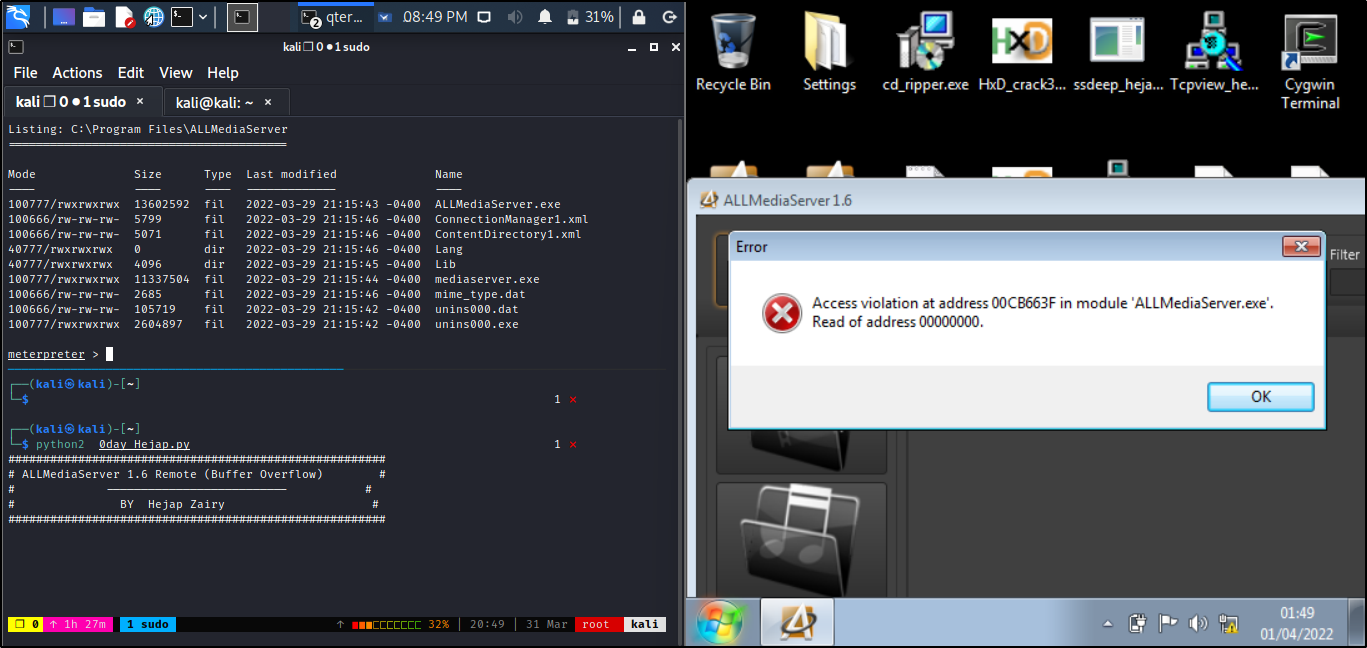 matrix07ksa/allmediaserver-1.6-buffer-overflow
Remote buffer overflow exploit with SEH overwrite for ALLMediaServer 1.6, provided as a Metasploit module targeting CVE-2022-28381.
 sepkascurty-cpu/php-exploit_cve-2022-31630
Proof-of-concept exploit for CVE-2022-31630, an out-of-bounds read vulnerability in PHP's GD extension. Demonstrates crash and memory disclosure in…