

GateX
 abraxas/gatex
FortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
binary-analysisbinary-exploitationcryptography+8
1
abraxas/gatexFortinetHunter (@YogSoth0) binary cracking application. Part of CTF for FortinetHunter. ELF door: a stripped Nuitka onefile, an XOR-scrambled…
 xf1les/fsop-finder
Binary Ninja plugin that scans glibc libio for FSOP code paths capable of hijacking control flow and stack pointer, aiding heap exploitation research.
 y198nt/nginx-chain-rift-poolslip
ASLR-independent nginx RCE chain PoC combining the PoolSlip heap over-read leak (CVE-2026-9256) with the rift overflow (CVE-2026-42945) to reach…
 structio-labs/n0xis
AI-first reverse-engineering toolkit: static analysis, SSA decompiler, live memory, provenance. Source-available (PolyForm Noncommercial).
 habanada/nativepe
Object Pascal (Delphi) library for parsing, mapping, loading, and dumping Windows PE files, with relocations, imports, TLS, and remote process memory…
 pyyyc/honor-6.12.38-43499-research
Research repository documenting exploitation attempts of CVE-2026-43499 futex UAF on Honor YLP-W00 kernel 6.12.38, including PoC sources, kernel…
 imeiplus/cve-2026-23111-poc
Working local privilege escalation exploit for CVE-2026-23111, a use-after-free in the Linux kernel nf_tables subsystem, with KASLR bypass and ROP…
 mein-0/gvcidrv64
Proof-of-concept exploit for Gigabyte's GVCIDrv64.sys kernel driver, achieving local privilege escalation via arbitrary physical memory and I/O port…
 fortbridge-uk/libheif-grid-nextjs-rce
Private Fortbridge PoC for the CVE-2026-32740 Next.js/sharp leak-to-memcpy-GOT RCE chain
 akatorich/kernelflirt
Windows kernel-level debugger with OllyDbg/IDA-style UI, software and hardware breakpoints, PDB symbols, decompiler, and 17 plugins for reverse…
 gmh5225/icall-gadget
Exploit for redirecting control flow of a legit kernel module to your own illegitimate kernel module to evade anti-cheats stack walking
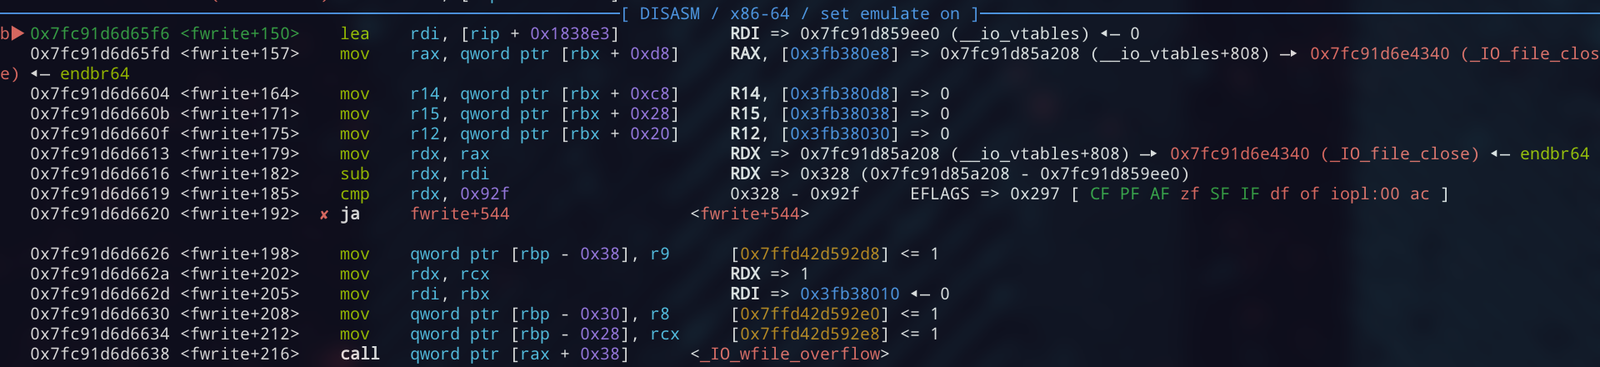 jazho76/house_of_apple_2
Interactive GDB walkthrough of the House of Apple 2 FSOP technique on glibc 2.43, with a reproducible sandbox covering vtable bypass, stack pivoting,…
 rafabd1/vectorfreed
Documents the VectorFreed librsvg use-after-free RCE chain (CVE-2026-96889) with an SVG generator PoC and remediation guidance for librsvg, Next.js,…
 se1ims/pixelsmash
Proof-of-concept and lab harness for CVE-2026-8461, an out-of-bounds write in FFmpeg's MagicYUV decoder, with payload generator and Qt demo player.
 adeadukagi/cve-2023-32233-reproduction
Reproduction and root-cause analysis of CVE-2023-32233, a Linux kernel nf_tables use-after-free enabling local privilege escalation, with PoC and…
 yutori-natsu/cve-2023-6931-pipa
Kernel LPE exploit for CVE-2023-6931 on Xiaomi Pad 6 (pipa), chaining a perf read_size overflow to root and disabling SELinux via data-only…
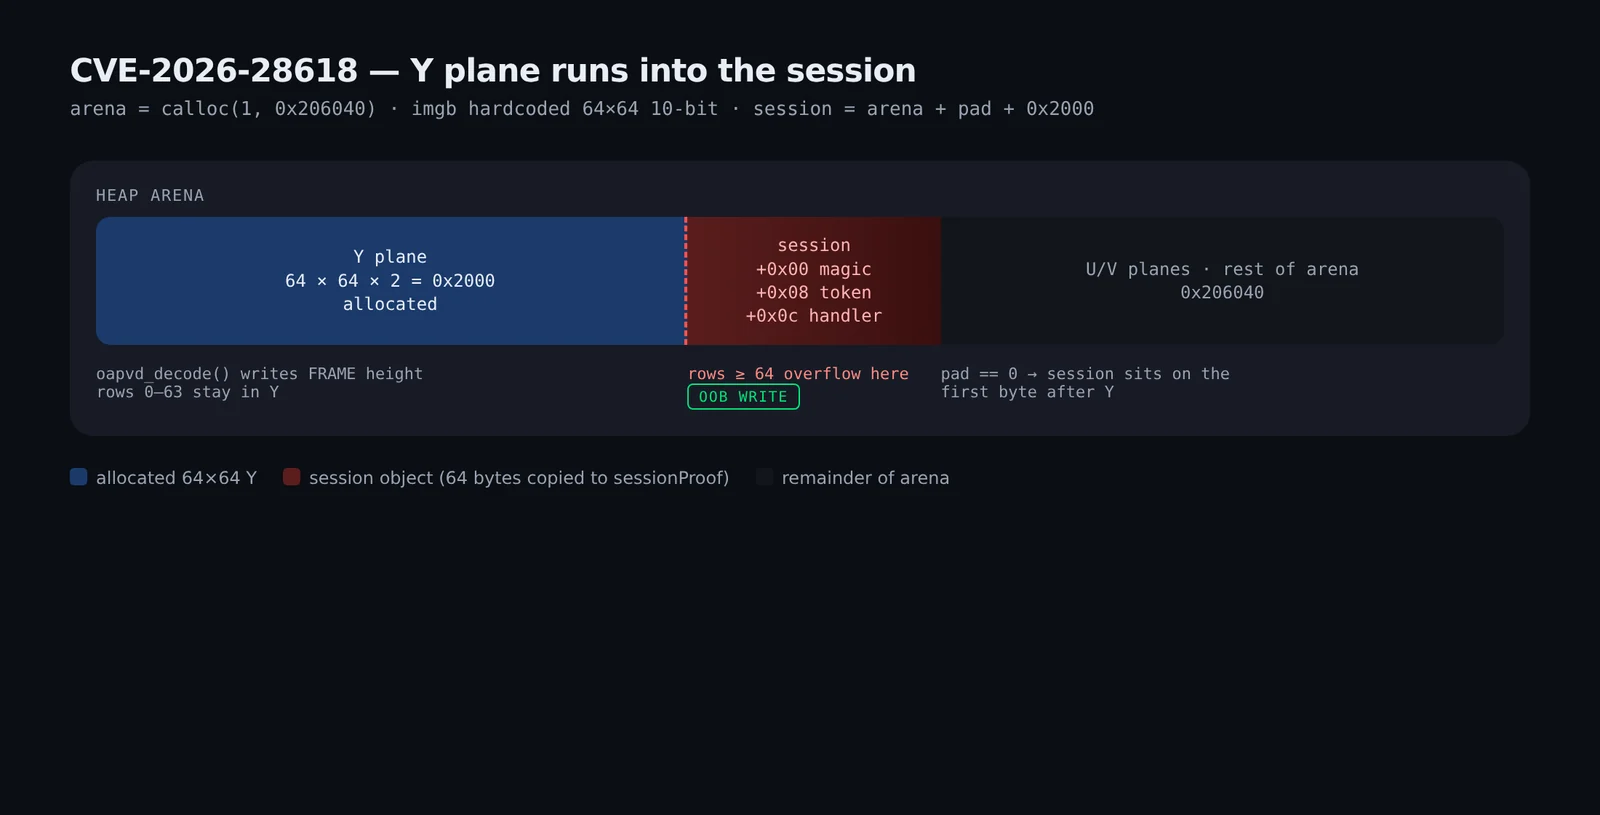 raafatabualazm/streambox-cve-2026-28618
Redacted notes on CVE-2026-28618 / StreamBox APV lab — heap write into a session object via FRAME height mismatch
 imeiplus/ghostlock-pfem10
GhostLock (CVE-2026-43499) for OPPO Find X5 Pro (PFEM10) — OPlus watchdog & heap-spray detector reverse engineering