

CVE-2022-34301
 themalwareguardian/cve-2022-34301
Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
binary-exploitationeducationexploitation+4
1
themalwareguardian/cve-2022-34301Demonstrates CVE-2022-34301 Secure Boot bypass via Eurosoft signed UEFI Shell (esdiags.efi), using the mm command to nullify gSecurity2 and load…
 themalwareguardian/cve-2022-34303
Demonstrates CVE-2022-34303 Secure Boot bypass via CryptoPro signed UEFI Shell, using the mm command to nullify gSecurity2 and load unsigned UEFI…
 mein-0/forti-research
Proof-of-concept exploiting a Fortinet fortimon3_74.sys kernel driver flaw to bypass PPL and terminate protected processes like lsass.exe via an…
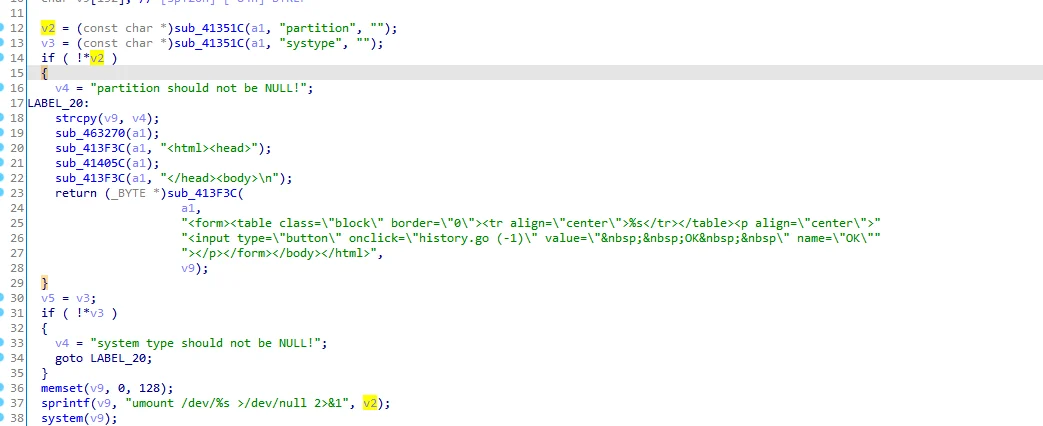 hackspeak/cve-2026-82592
Proof-of-concept exploit for D-Link DIR-825M stack buffer overflow and command injection in /boafrm/formDiskFormat, enabling remote code execution as…
 shinycolumn/cve-2025-56799
OS Command Injection Vulnerability via Cache Clearing Scheduler in Reolink Desktop Application
 livepwn/cve-2025-55616
Exploit for CVE-2025-55616, a local RCE in Zsh via history expression, achieving arbitrary code execution with user privileges.
 hrishitjoshi/cve-2021-4034
PWNKIT - Local Privilege Escalation Vulnerability on Linux (Polkit)
 cryingn/cve-2026-44656
Reproduction environment for CVE-2026-44656, a Vim modeline command injection vulnerability. Includes Docker setup, PoC file, and exploit script to…
 ck00004/cve-2021-4034
Exploit for CVE-2021-4034 (pkexec) targeting CentOS 8, allowing custom command execution via modified pwnkit-dry-run.c. Includes compilation and…
 h1d3r/copy-fail_lpe_interactive
Exploit for CVE-2026-31431, a Linux kernel page cache corruption vulnerability, providing interactive root shell and non-interactive command…
 s3c/globalprotect-ca-cert-ipc
Proof-of-concept exploit for CVE-2025-0117 in GlobalProtect, achieving privilege escalation to SYSTEM via a backdoored installer and DLL injection.
 trustsig-eu/wasm2c-tableflip
wasm2c sandbox escape. An untrusted WebAssembly module breaks out of the generated C sandbox and executes an arbitrary shell command on the host.
 kentox493/cve-2026-42945_nginxrift
Automates CVE-2026-42945 exploitation in NGINX containers: verifies vulnerable targets, brute-forces heap offsets, executes commands, and opens an…
 petitoto/chromium-exploit-dev
Toolkit to weaponize Chromium vulnerabilities into reliable, cross-platform, full-chain exploits
 mbadanoiu/mal-009
MAL-009: Insecure Chaining of Flags T and TT in Zip for Linux
 bishopfox/cve-2021-35211
Python exploit for Serv-U SSH vulnerability (CVE-2021-35211) with multiple payload modes: stage, exec, and download-execute, enabling shellcode…
 kaanaryoverflow/ipfire-2-25-auth-rce
ipfire 2.25 authenticated remote code execution